

System Requirements
The Job Description Sync makes use of existing Workday functionality. The customer will need a TechWolf contract with a live TechWolf tenant, populated with (a subset of) the Job entities in Workday, and job descriptions authored in the TechWolf Console. This integration authenticates with OAuth only, through Direct Tenant Communication or through Workday’s API gateway (WCP). It always uses the same method as the Job Skill Sync. TechWolf sets that method.Workday Configuration
A Workday integration user must be configured in the Workday tenant with an implementation security group.If you already have a Job Skill Sync integration configured, the same ISU,
security group, and API Client can be reused: steps 1–3 of the General
setup and the Direct Tenant Communication or WCP gateway setup are already
in place, and the
Job Information domain policy from that setup is already
sufficient for this integration’s read access. The only new step is the
business process permission in step 4 — after granting it, run Activate Pending Security Policy Changes and continue to the Console Configuration
section.General setup
1
Create Integration System User (ISU)
-
Create Integration System Userbusiness process. - Do not allow UI sessions as this user will only be used for automations.
- Please securely store the username and password of this user.
-
Set the ISU’s language preferences: The integration requires the ISU’s
locale and display language to be English (United States); this language
preference can be set when proxying as the ISU. Note that ISUs do not show up
in the
Start Proxytask. Instead, starting the proxy can be done by running theAll Workday Accountsreport, filtering the “User Name” column on the ISU’s username, and then, from the account’s related actions, choosing “Security Profile” > “Start Proxy”.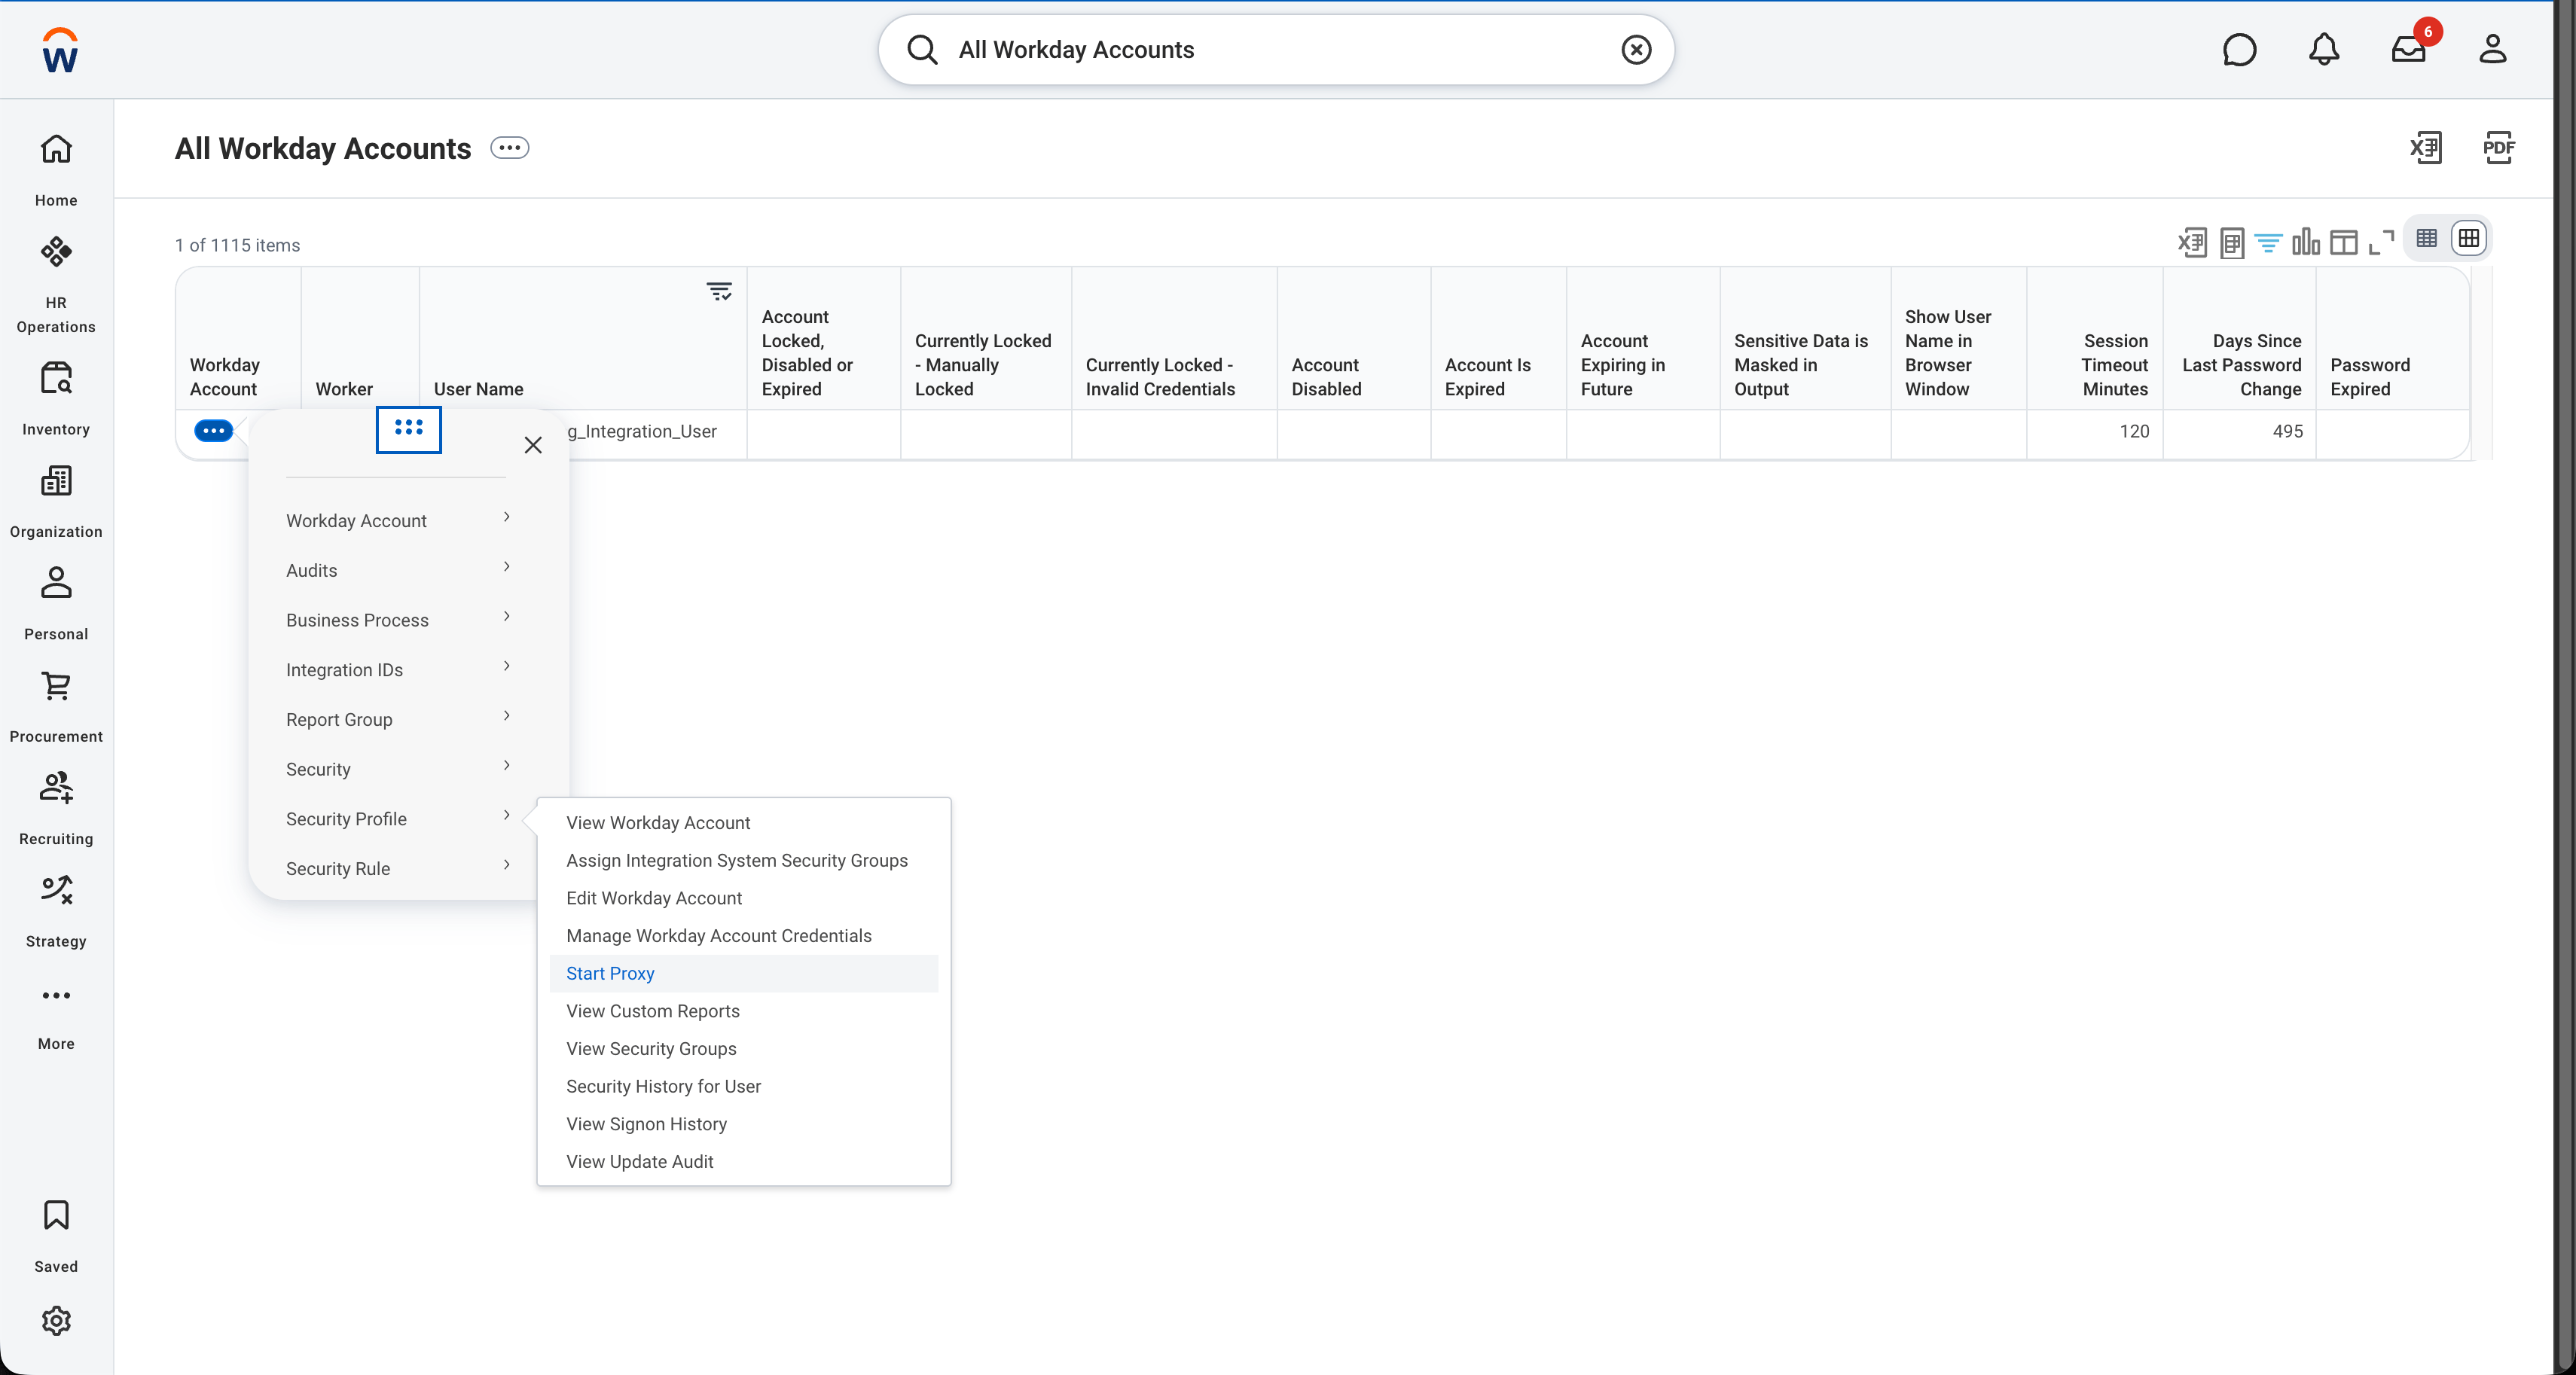
Change Preferencestask and set the fields from the table below: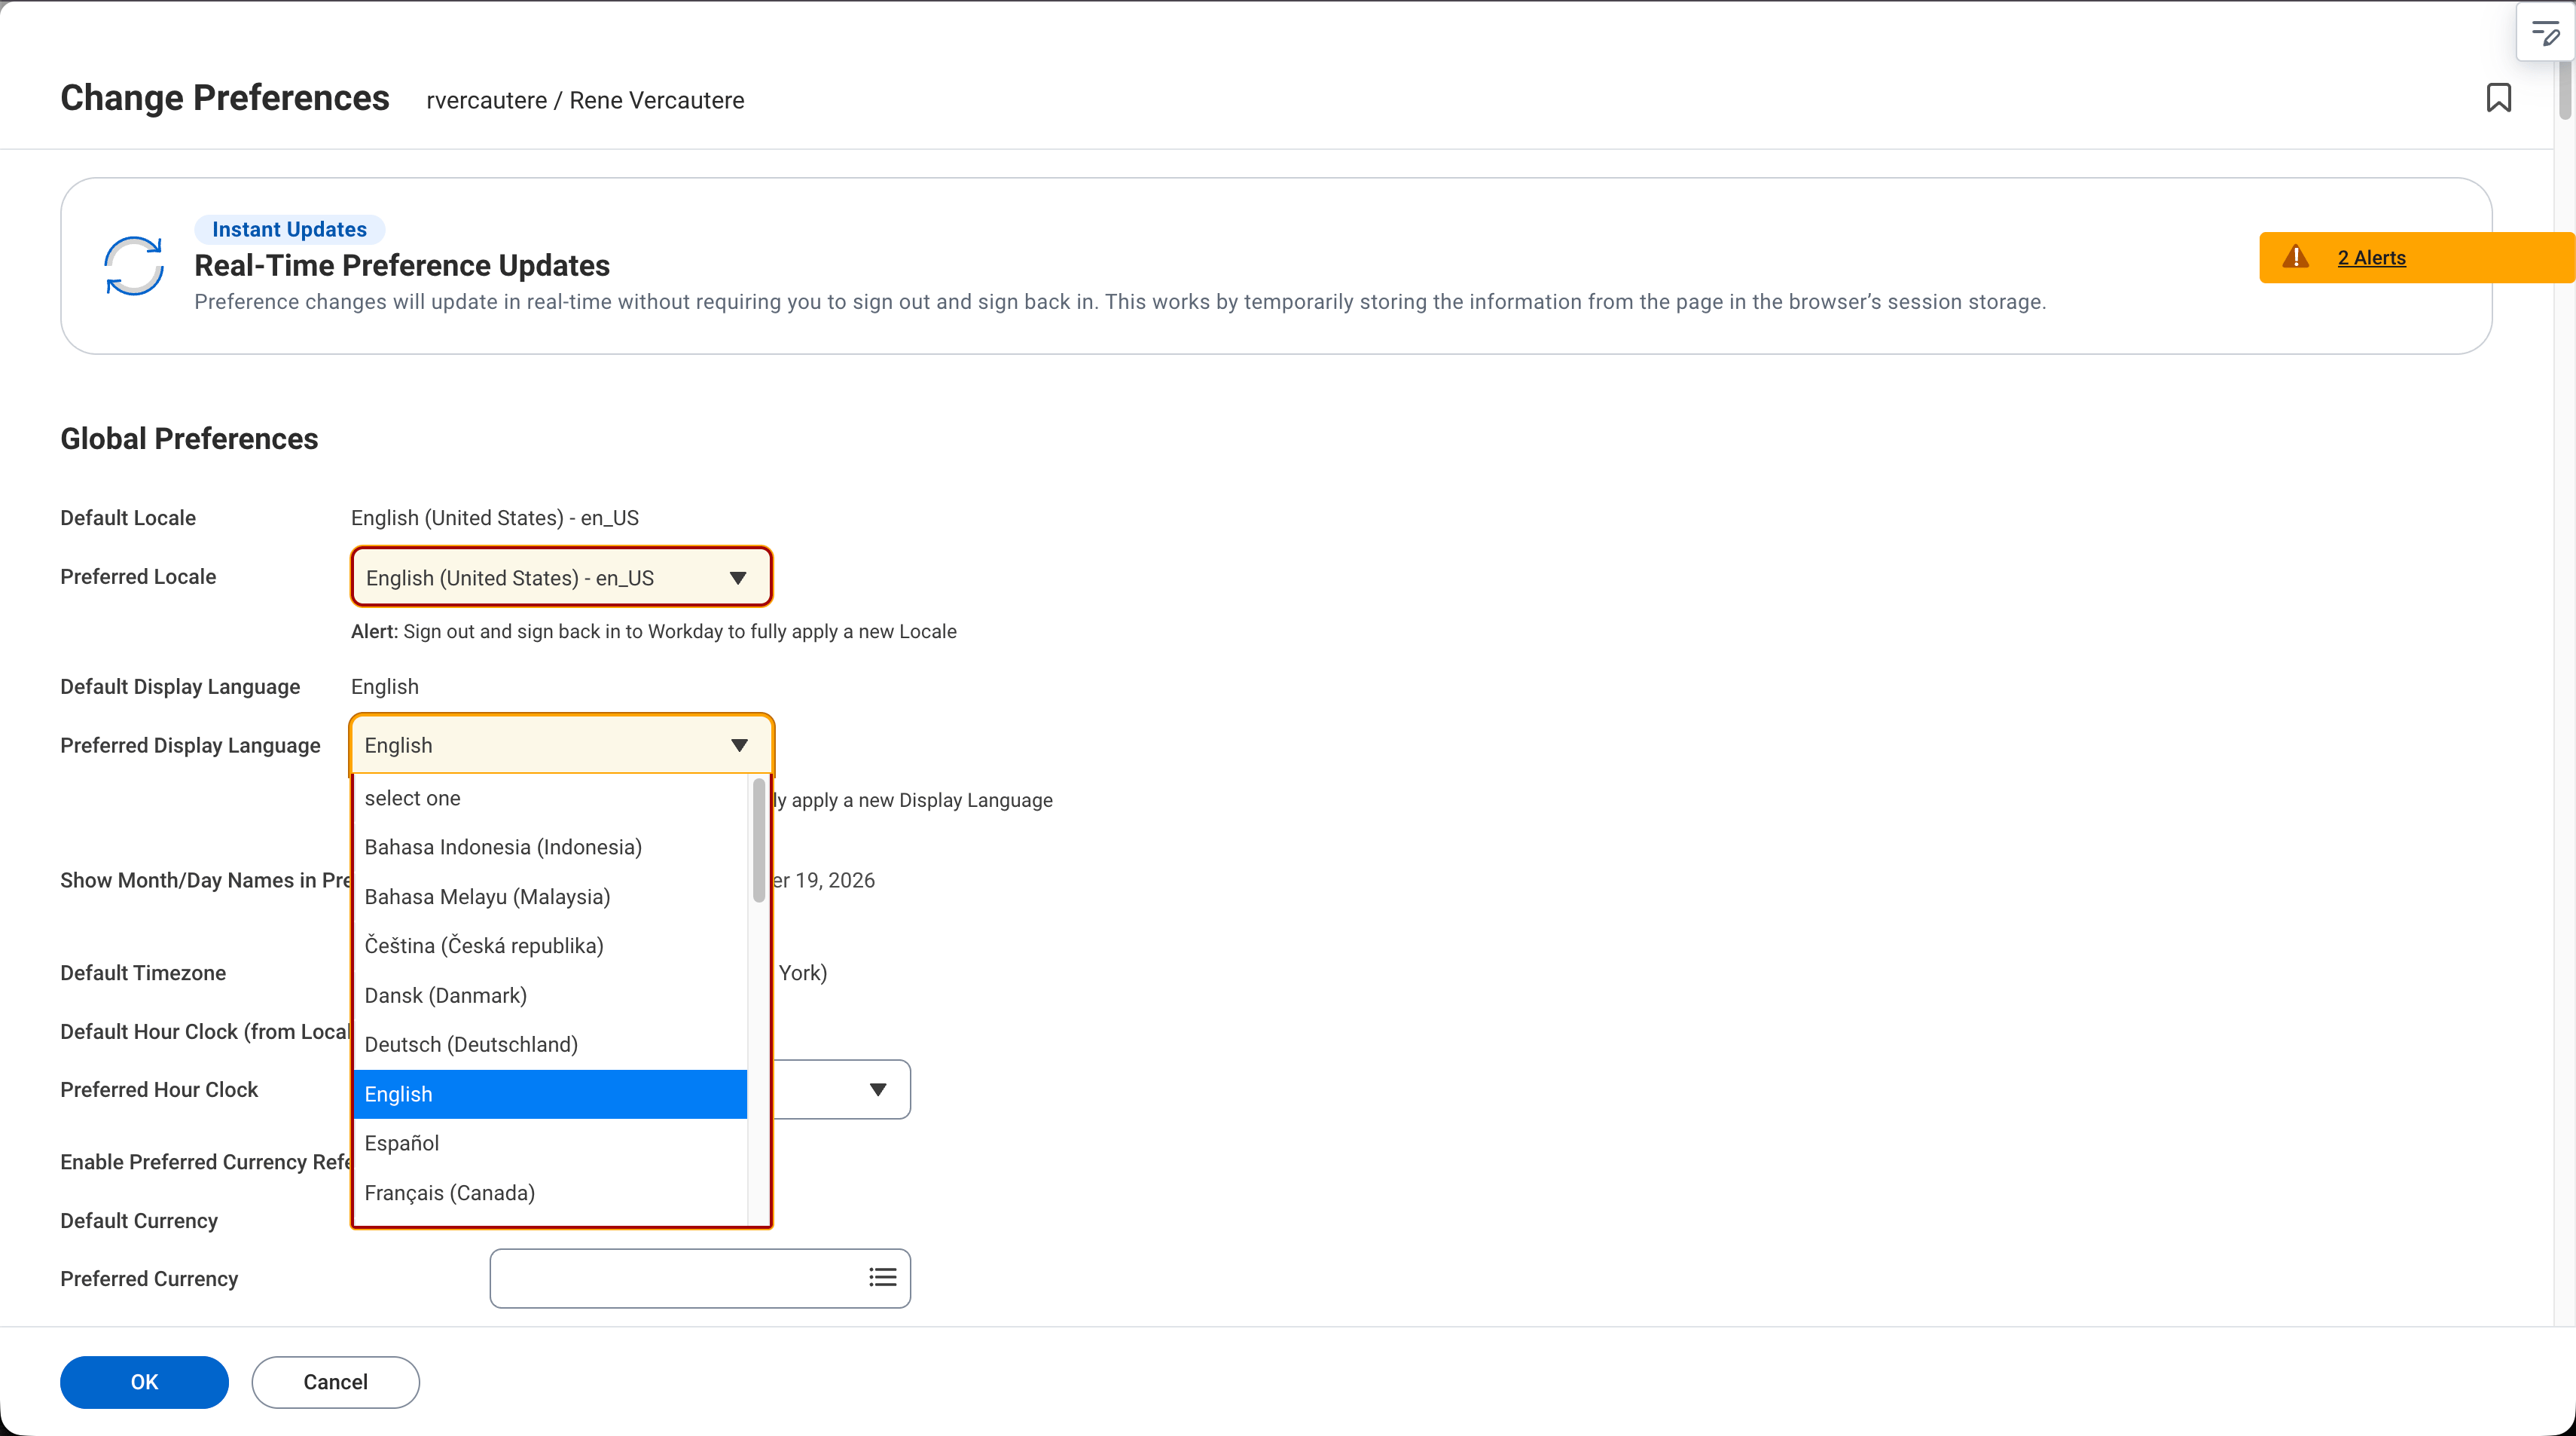
Stop Proxytask.
2
Update password expiration rules for ISU
-
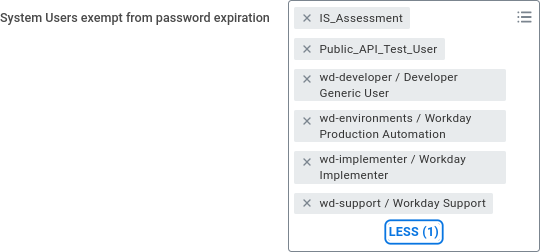
In the
Maintain Password Rulesbusiness process under “System Users exempt from password expiration” add the newly created ISU to the list. -
Note: This ensures the integrations will keep running without
interruptions due to password expiration.
3
Set up security permissions for the ISU through security policies
-
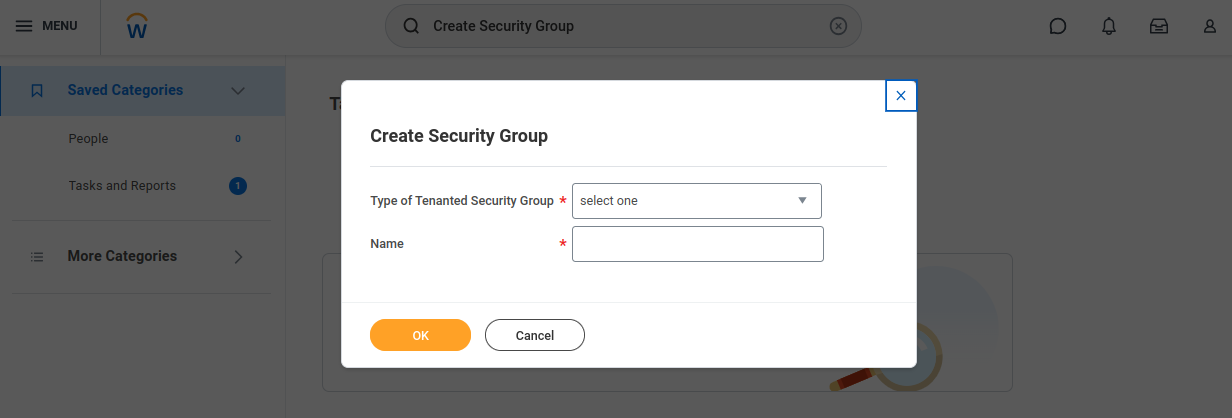
Go to
Create Security Group, choose “Integration System Security Group (Unconstrained)”. -
Note on acceptance testing: Consider using two different security groups,
one Unconstrained and one Constrained. This way, the test-set is scoped while
the correct permissions are applied for other Web Services.
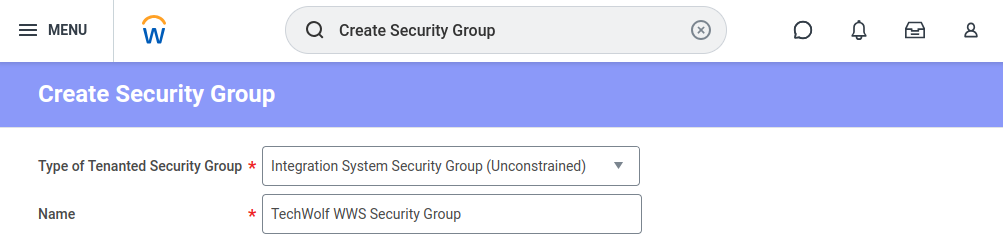
-
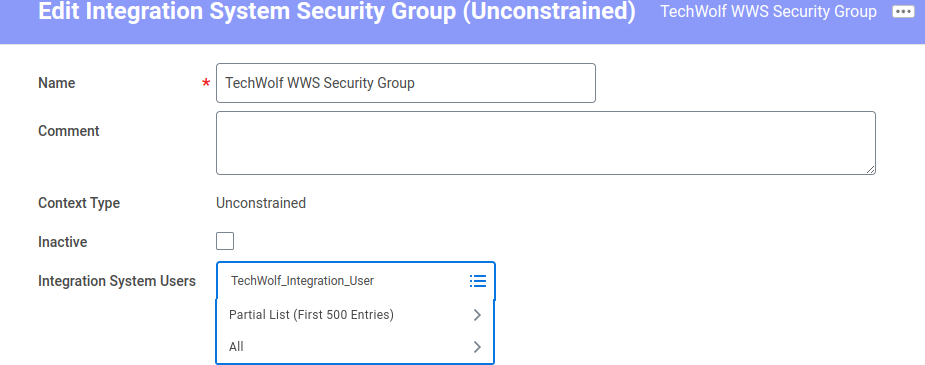
The next screen presents you with an Edit form to add additional information.
Add your ISU to the list. This can be changed later too. Do not check
“Inactive”.
4
Set up the Security Group's permissions
Job descriptions live on the Workday Job Profile, and Workday manages changes to
job profiles through the Manage Job Profile business process — the same
process that runs when an admin edits a job profile in the Workday UI. The
integration therefore needs two kinds of permissions: domain access to read
job profiles, and permission to start the business process that updates them.Domain security policies (read access)
- Search for “View Security Group” and select your created security group.
- Select the option menu next to the Security Group’s name, go to “Security Group” and select “Maintain Domain Permissions for Security Group”.
- Under Integration Permissions add the following Domain Security Policy:
Business process permission (update access)
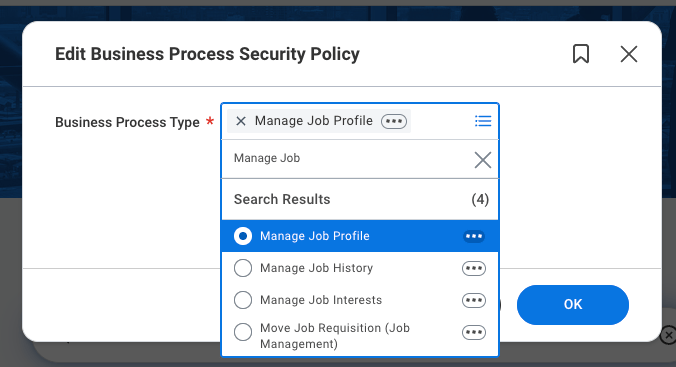
- Search for “Edit Business Process Security Policy” and select the Manage Job
Profile business process.
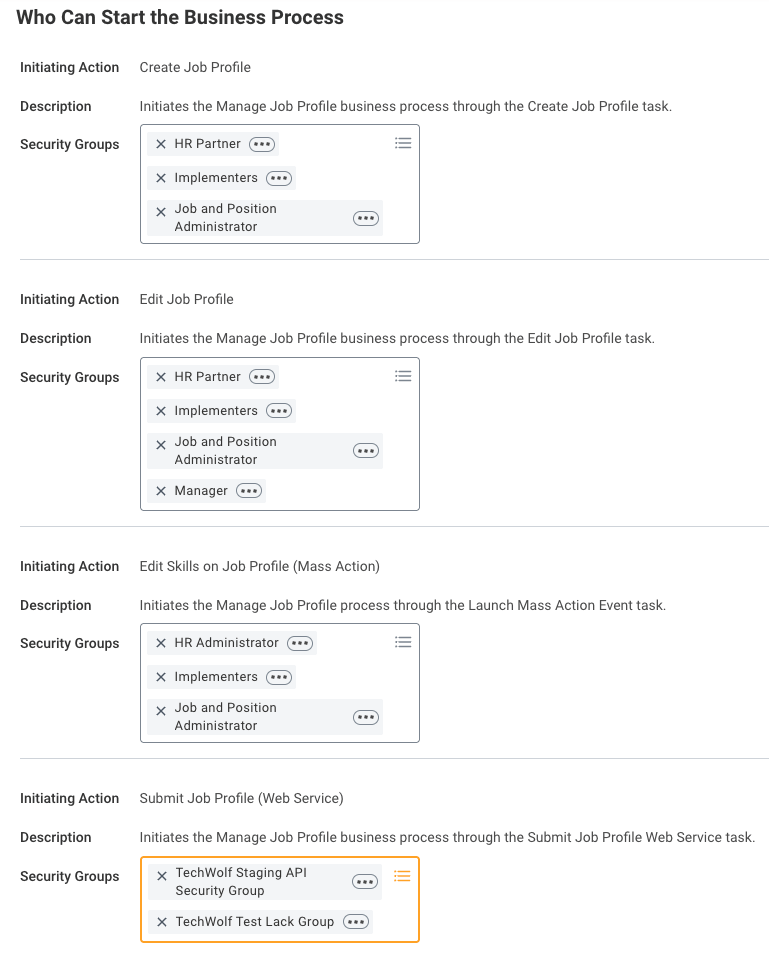
- Under “Who Can Start the Business Process”, find the Initiating Action
Submit Job Profile (Web Service) and add your security group to its
Security Groups.
- Run the
Activate Pending Security Policy Changestask to apply both changes.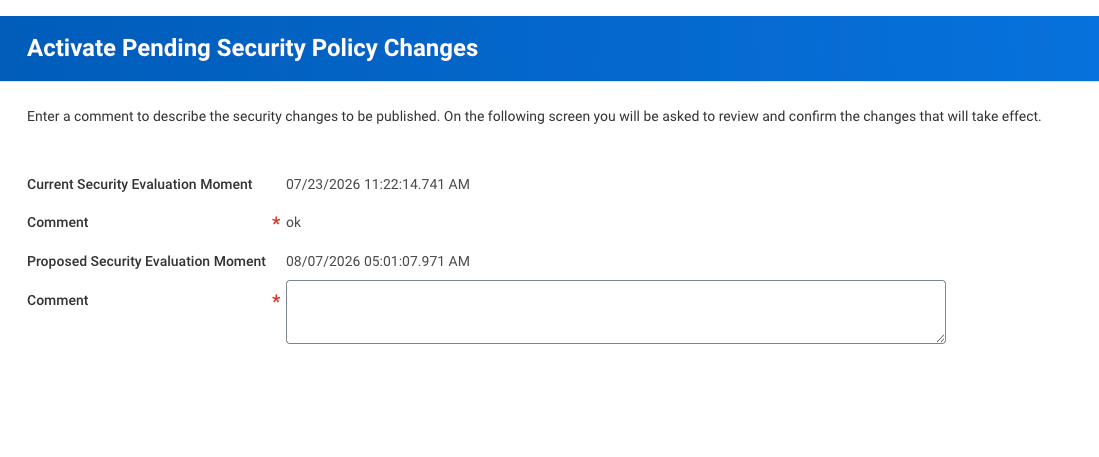
This business process permission is the entire update-side key: with it, the
integration’s updates complete automatically and are recorded as regular,
auditable Manage Job Profile events in your tenant’s history. The
integration only ever submits the job description field — skills and all
other profile fields are never part of its payload. If your security team
wants Workday itself to enforce description-only updates as well, an opt-in
server-side restriction is available — ask your TechWolf contact.
OAuth: Direct Tenant Communication setup
1
Find out the correct Workday API URL
-
Search for
Public Web Servicesin the search bar at the top of the Workday home page. -
In the list, click the three dots next to the
Human Resources (public)entry. SelectView WSDLunderWeb Service.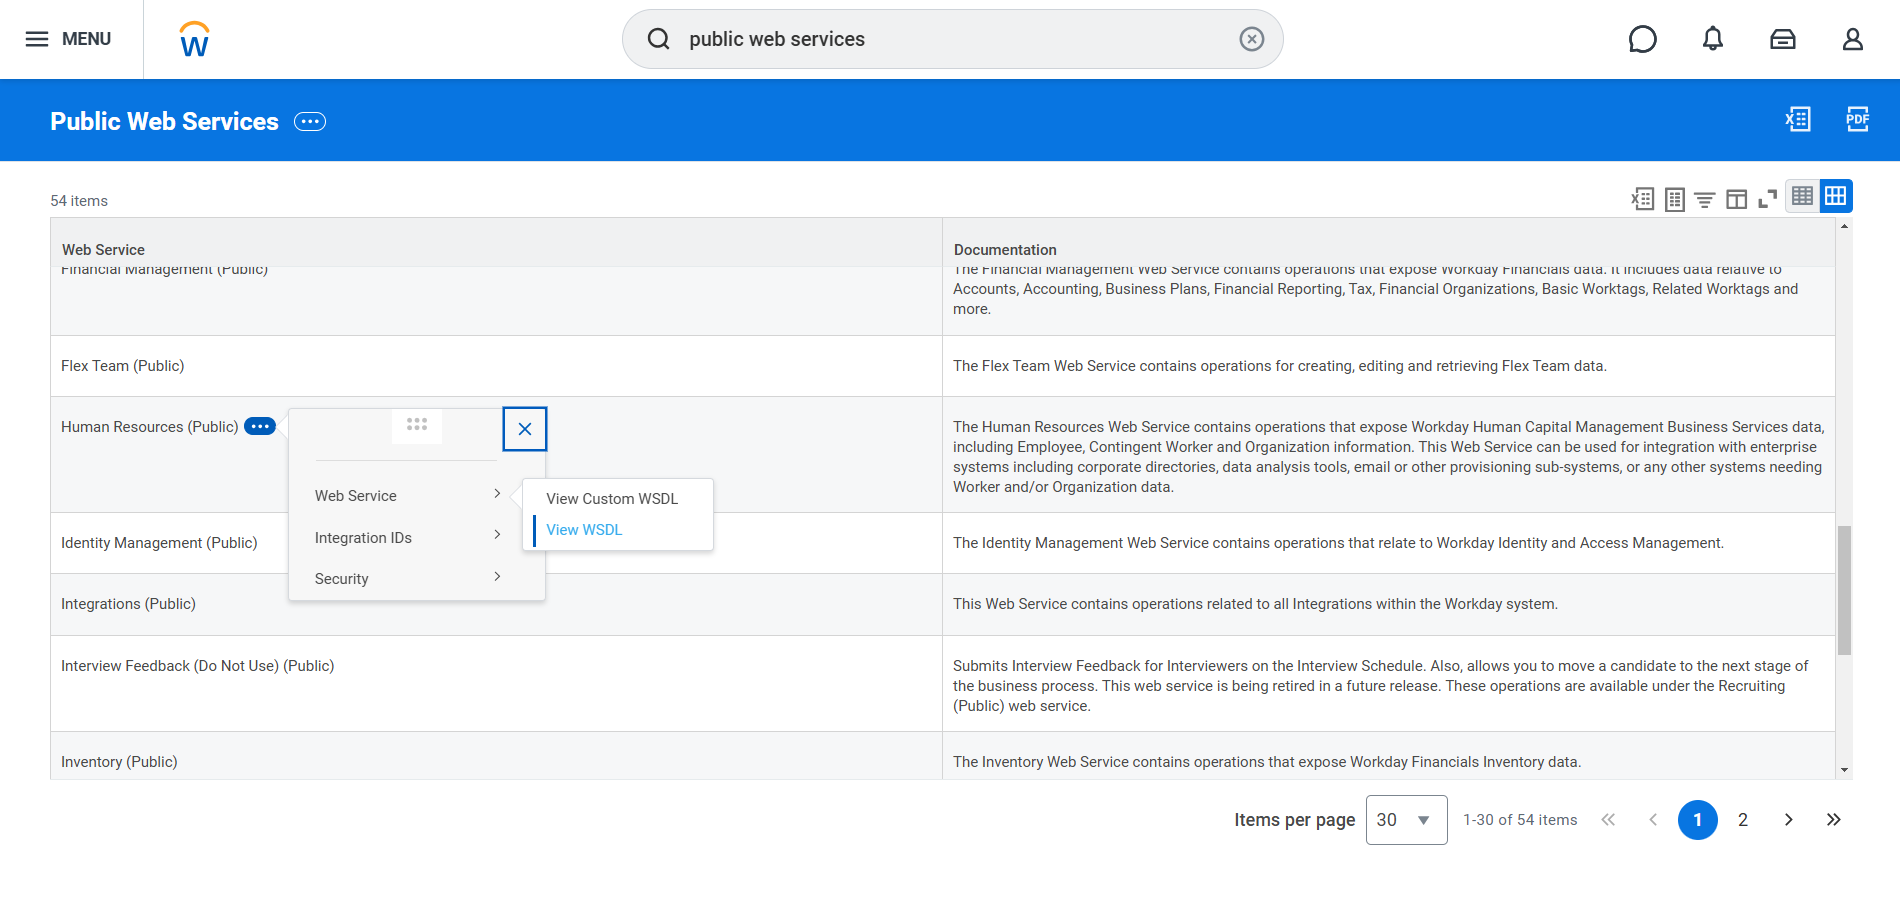
-
The resulting page will take some time to load. Once it is loaded, look for
“soapbind:address location” near the bottom of the page. You will see a
section like this:
- Copy the base tenant URL up to and including your tenant name. The service name and version should be excluded from the URL.
- Note that the API URL can differ between implementation tenants and production tenants, so the steps described above need to be repeated for each tenant individually.
2
Create API Client for Integrations
- Search for “Register API Client for Integrations” business process
- Enable non-expiring refresh tokens to ensure continuity of service
-
Under “Scope (Functional Areas)”, add exactly these scopes:
Scope (Functional Area) Needed for - Optionally, restrict the client to TechWolf’s IP ranges by filling in the “Restricted to IP Ranges” field with the values from the IP Addresses page
-
Securely store the client ID and client secret
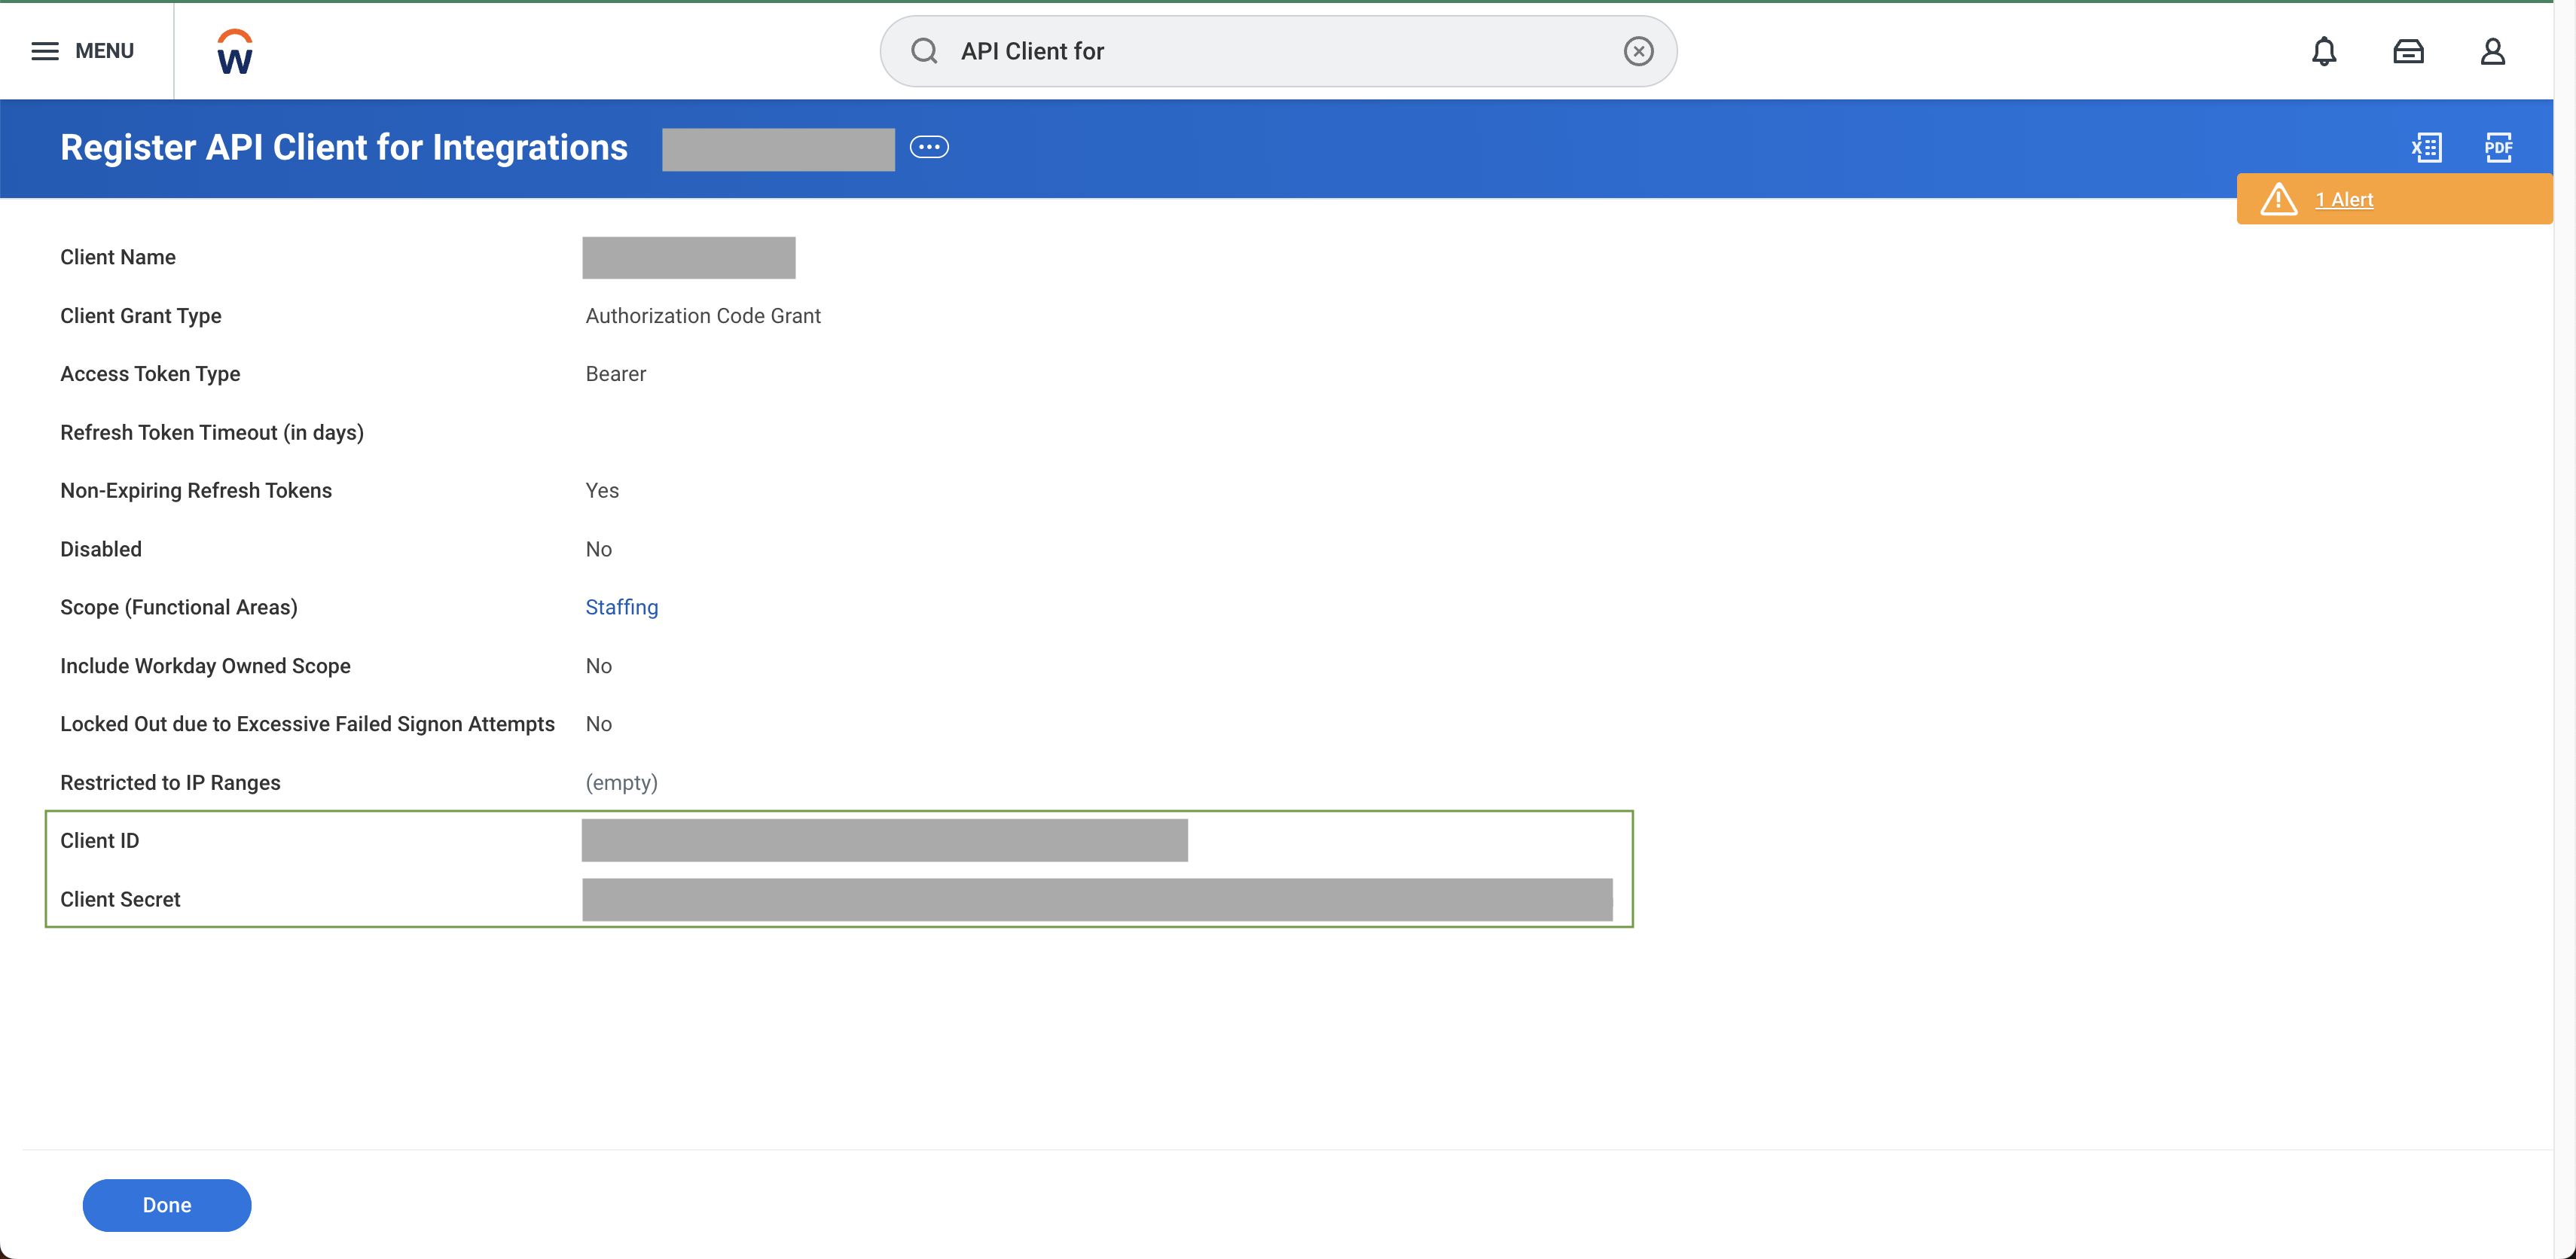
3
Generate Refresh Token
- Search for “View API Clients” report
- Click “API Clients for Integrations” tab
- Note down the token endpoint. You will need to share this later.
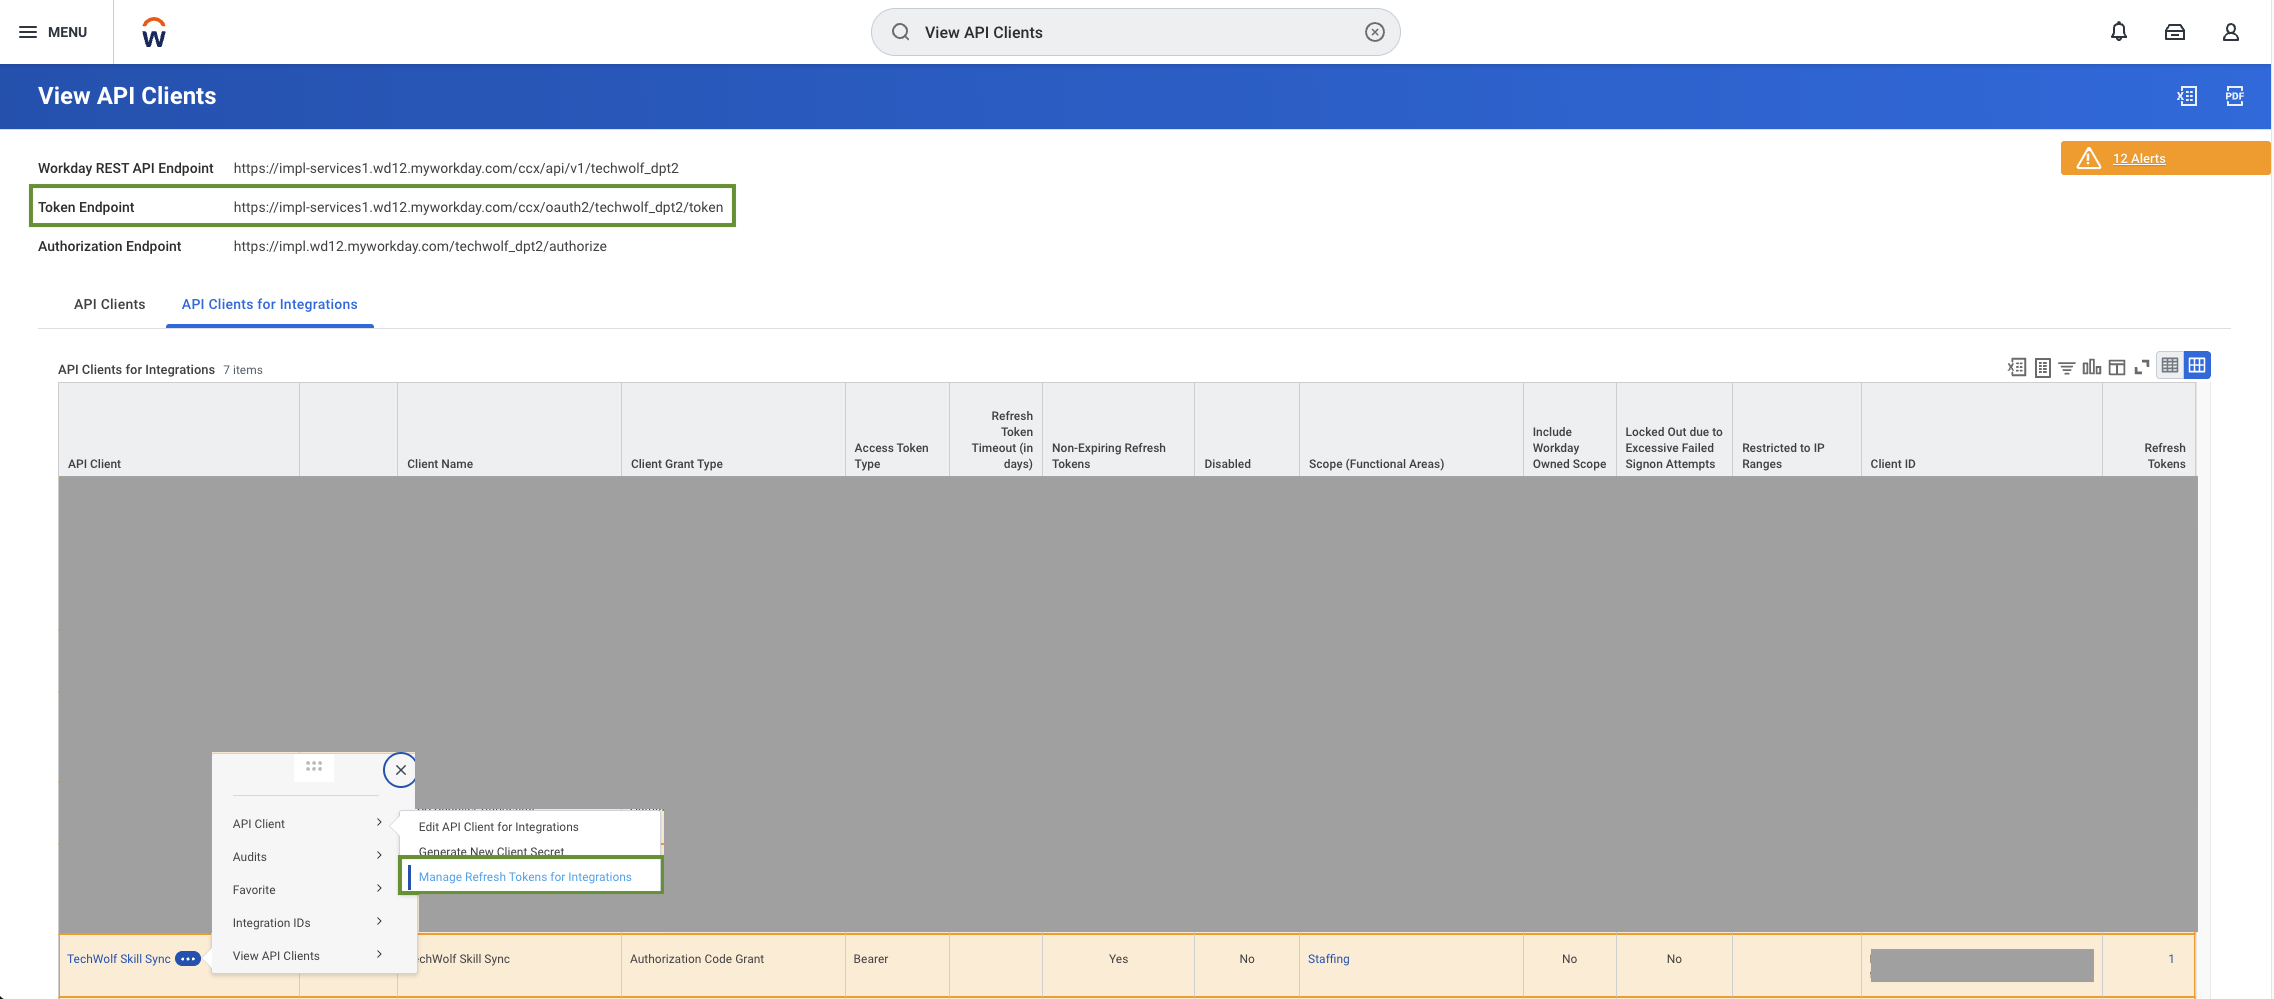
- Find your API client and select “Manage Refresh Tokens for Integrations”
- Under “Workday Account”, type in your ISU
- Press OK
- Check the box “Generate new refresh token”
- Press OK
- Securely store the refresh token.
OAuth: WCP gateway setup
The gateway uses the ISU and the domain security policies from the General setup. What you need- An administrator on the Developer Site, to create the API client.
- A Company Administrator, to authorize a non-development tenant.
- A Workday security administrator, to map the API client to the ISU.
- Your company’s Workday Named Support Contact, only if the tenant is not listed for Workday Extend.
1
Check that the tenant is listed
On the Workday Developer Site, open Console → Tenants.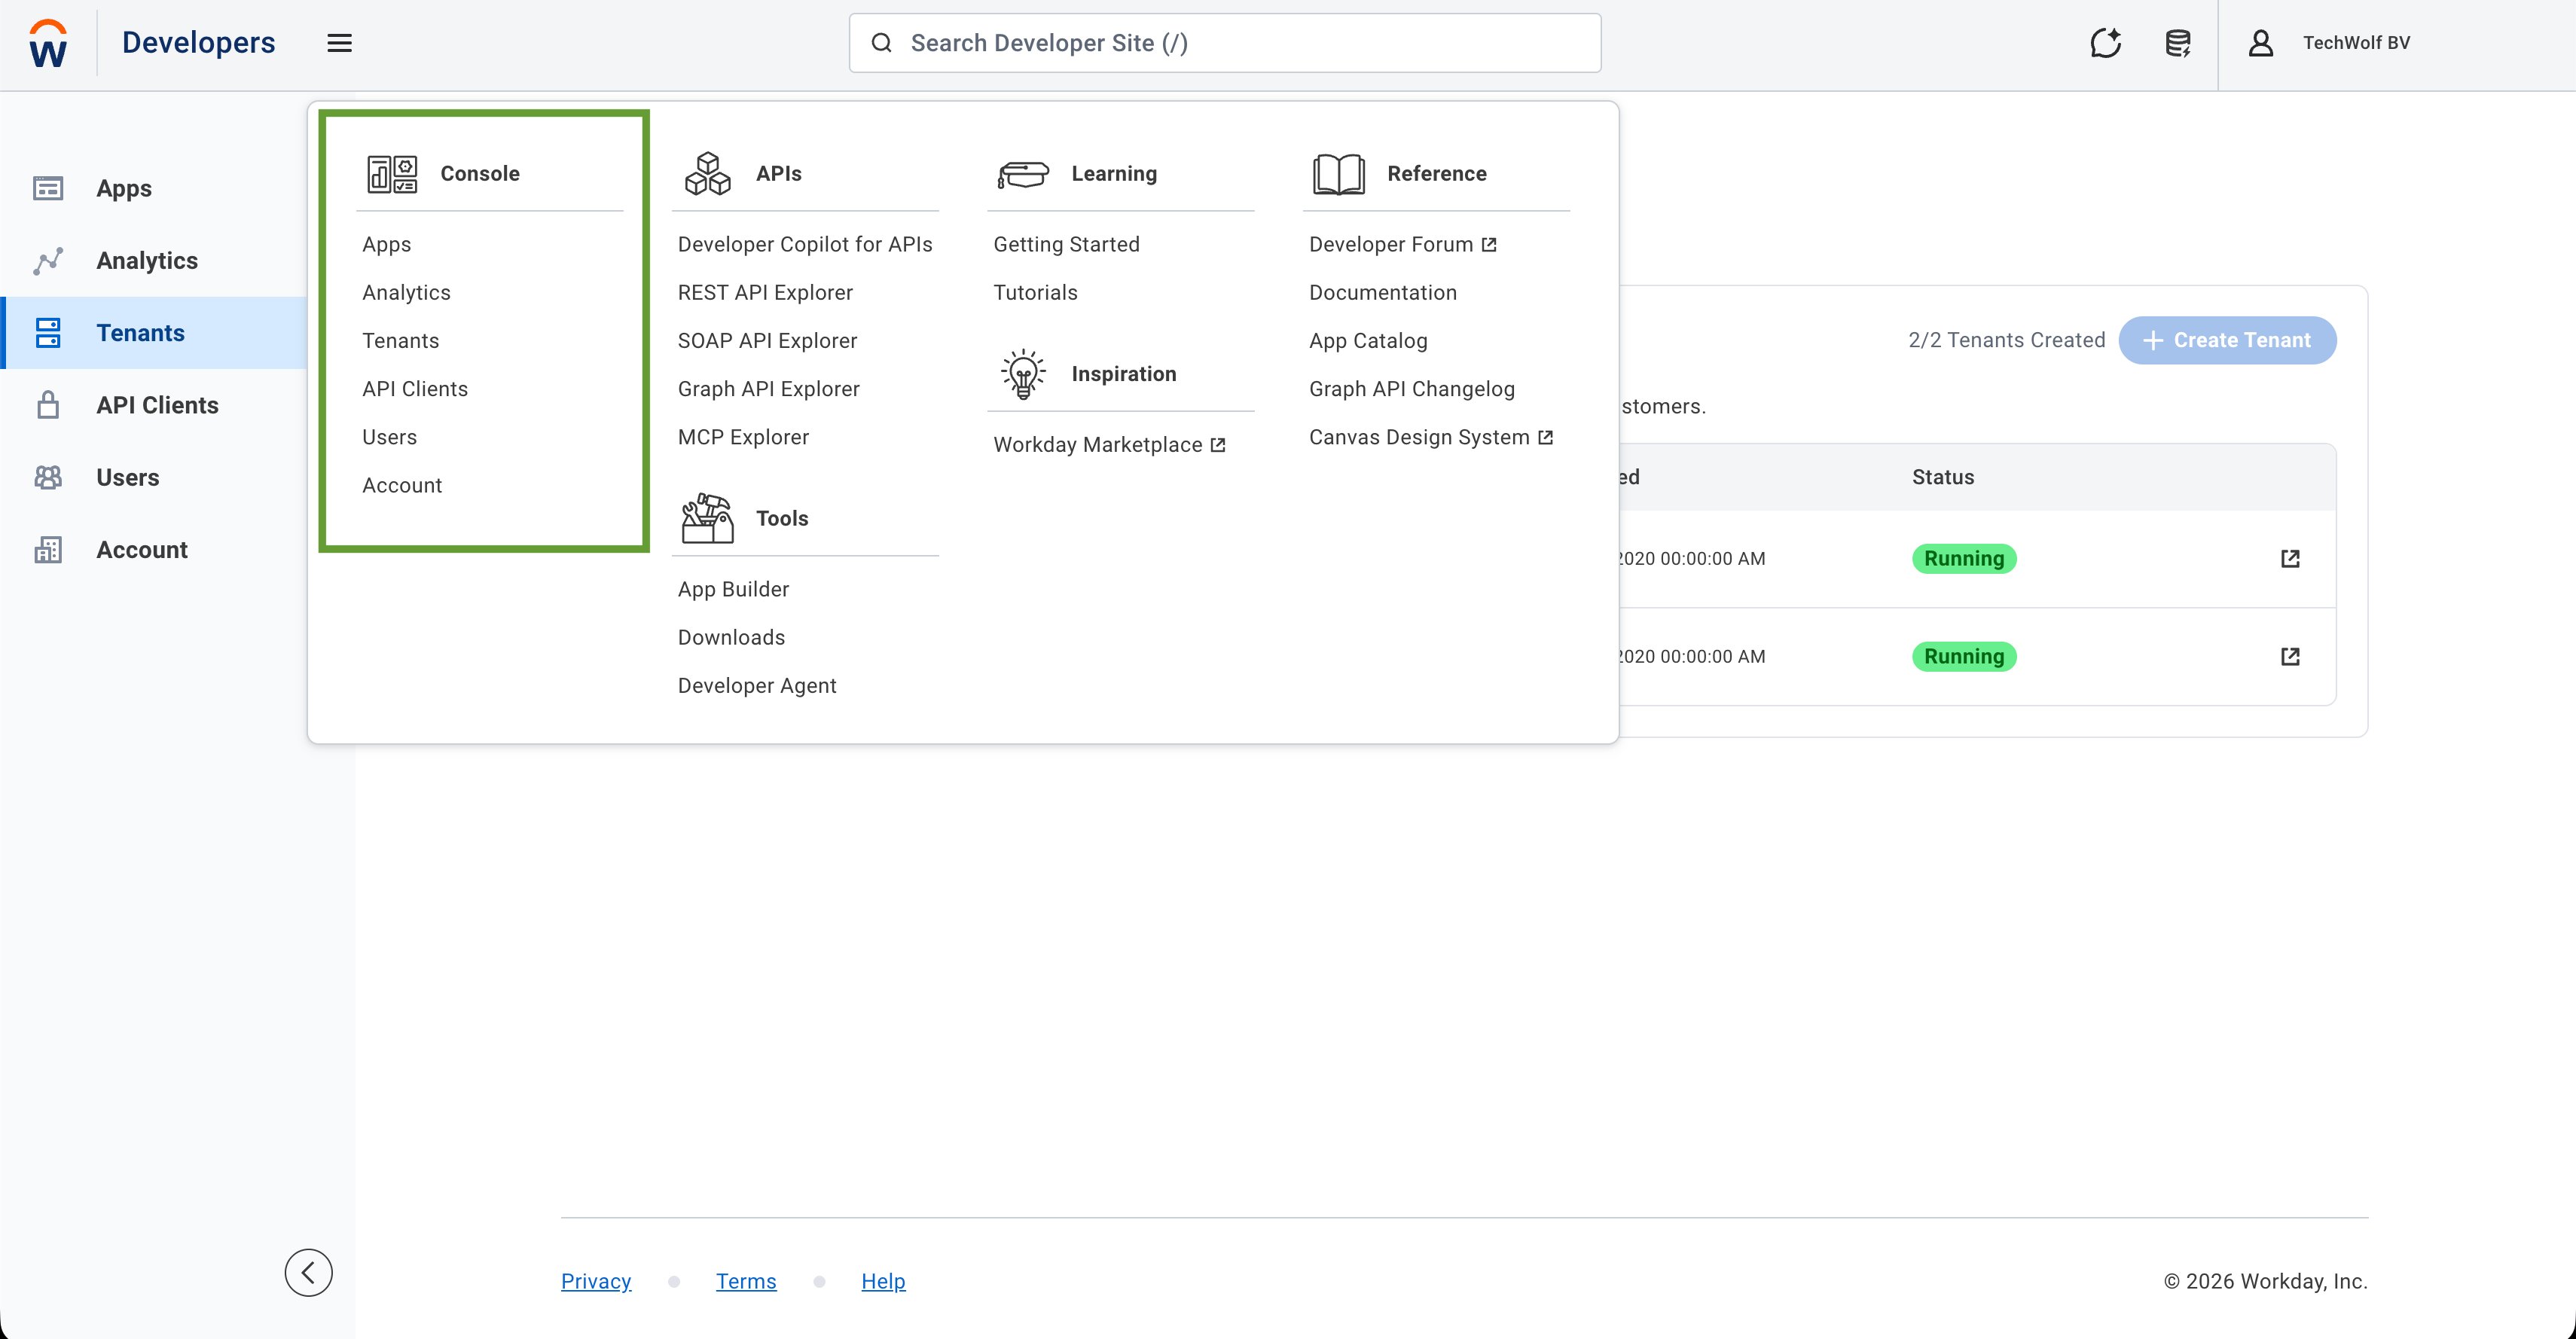
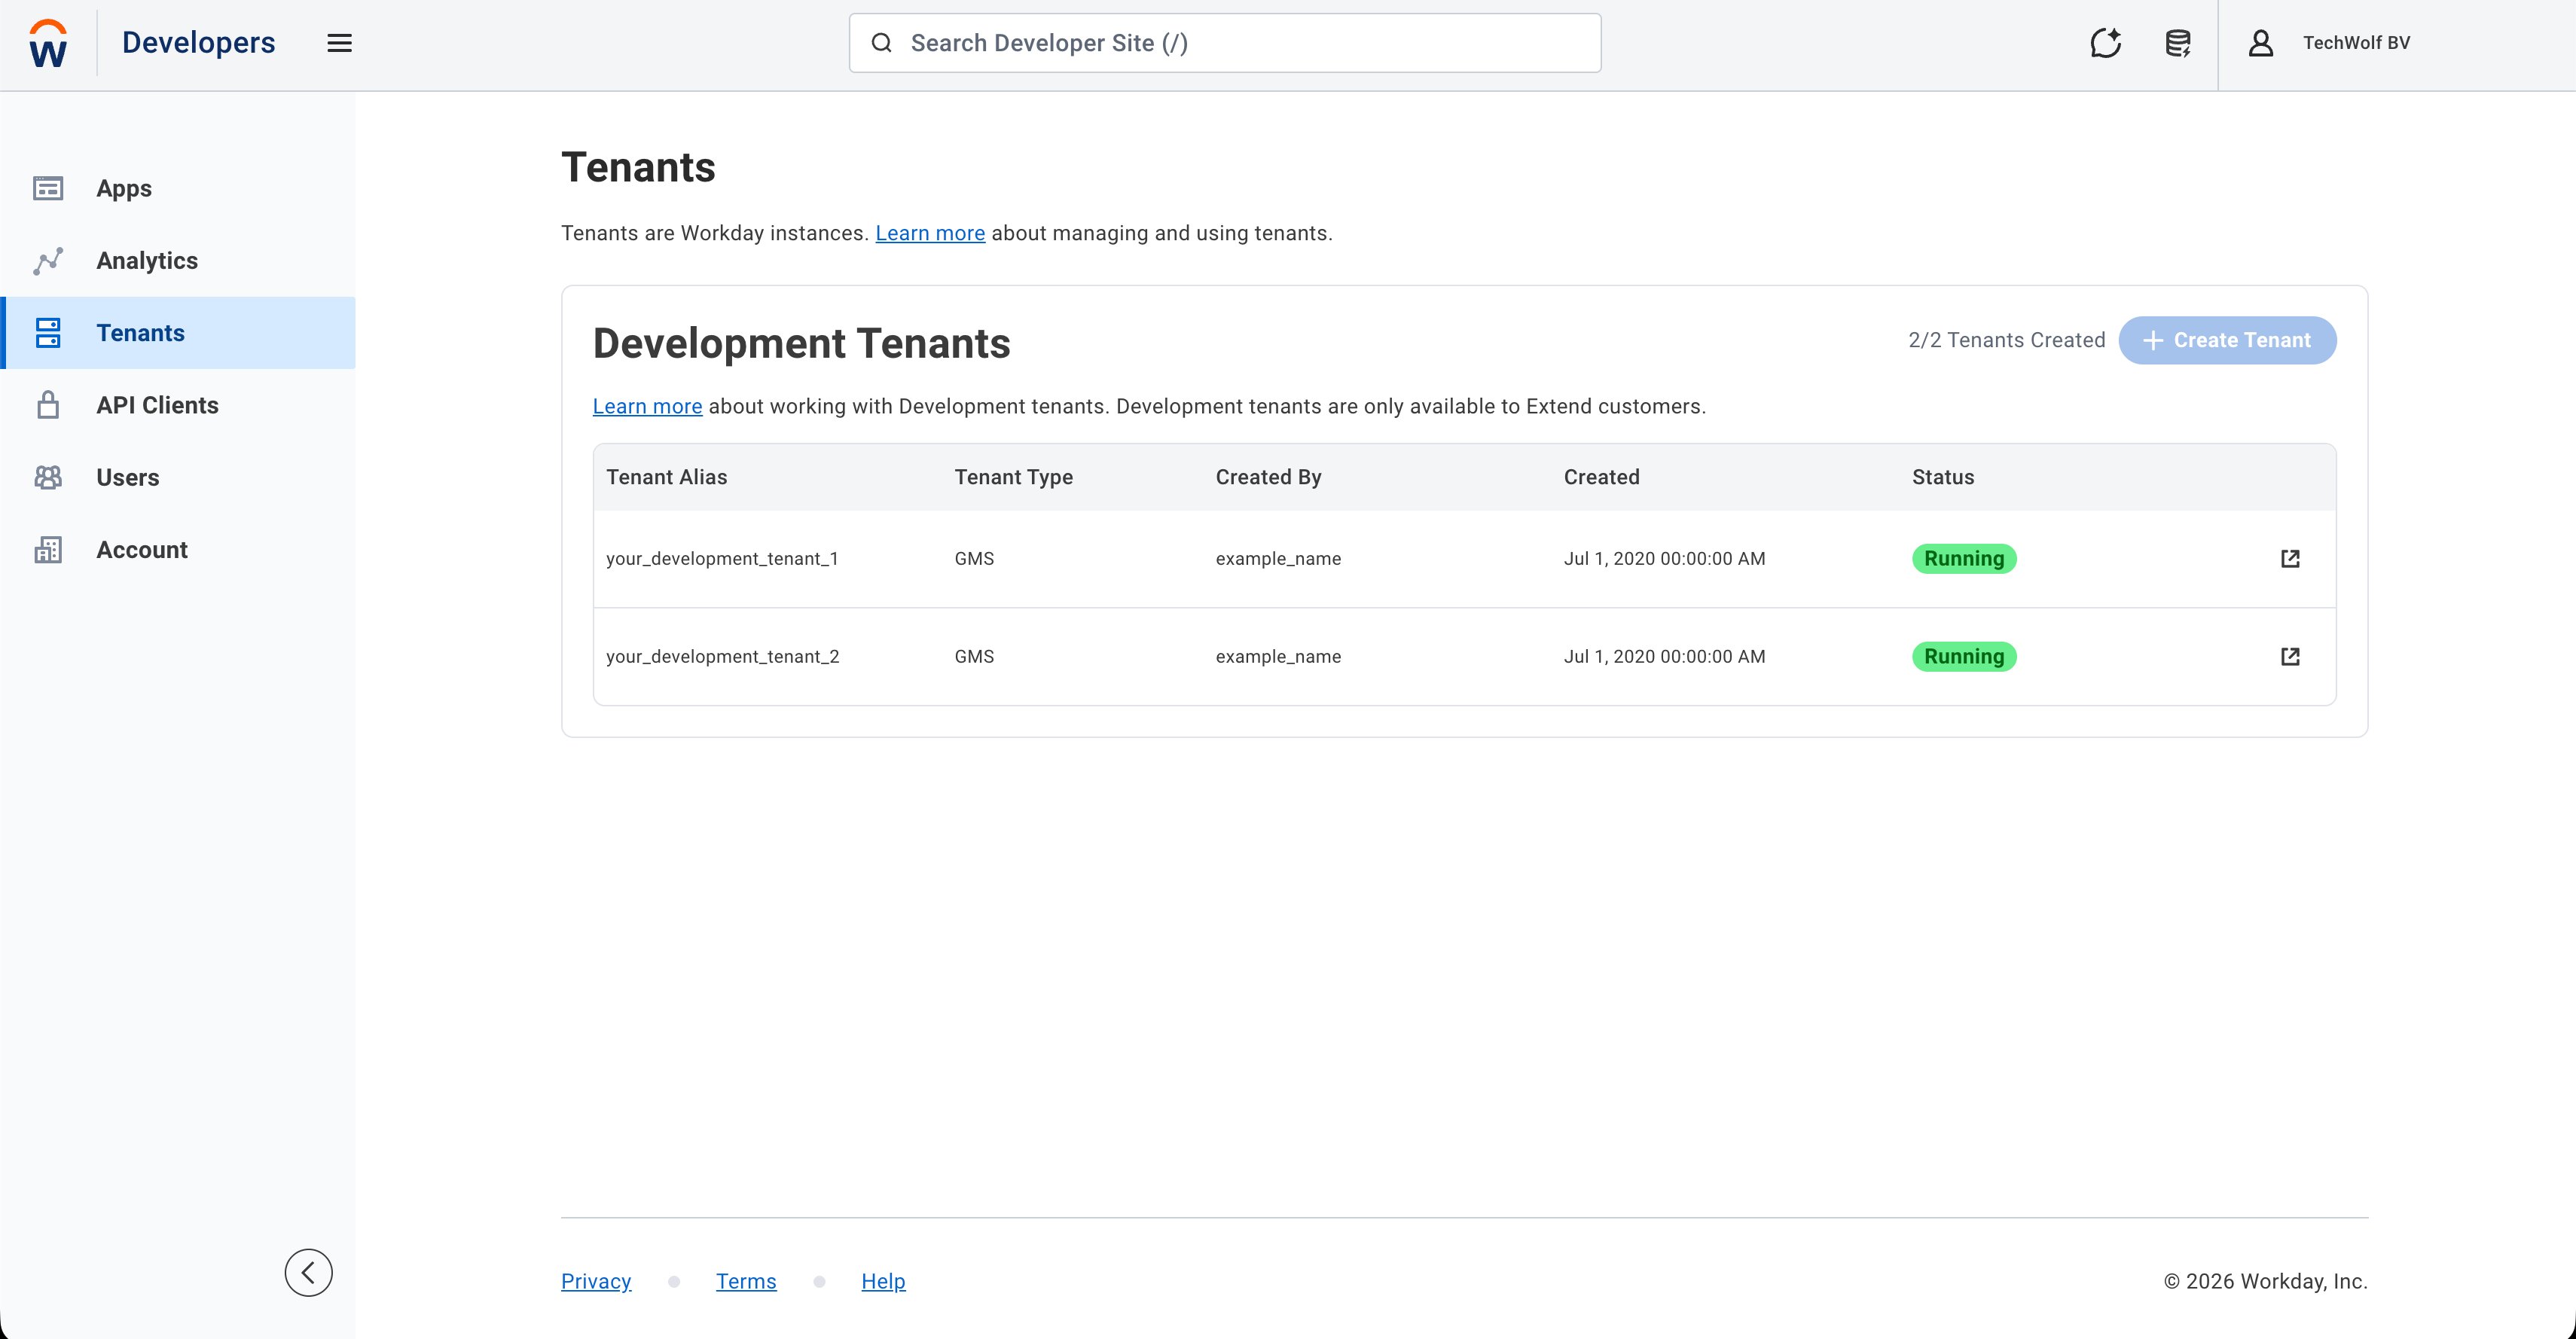
Manage Workday Cloud Platform task, once per
tenant.
See
Enable Non-Development Tenants for Workday Extend.2
Create the API client
- On the Developer Site, open Console → API Clients → Create API Client.
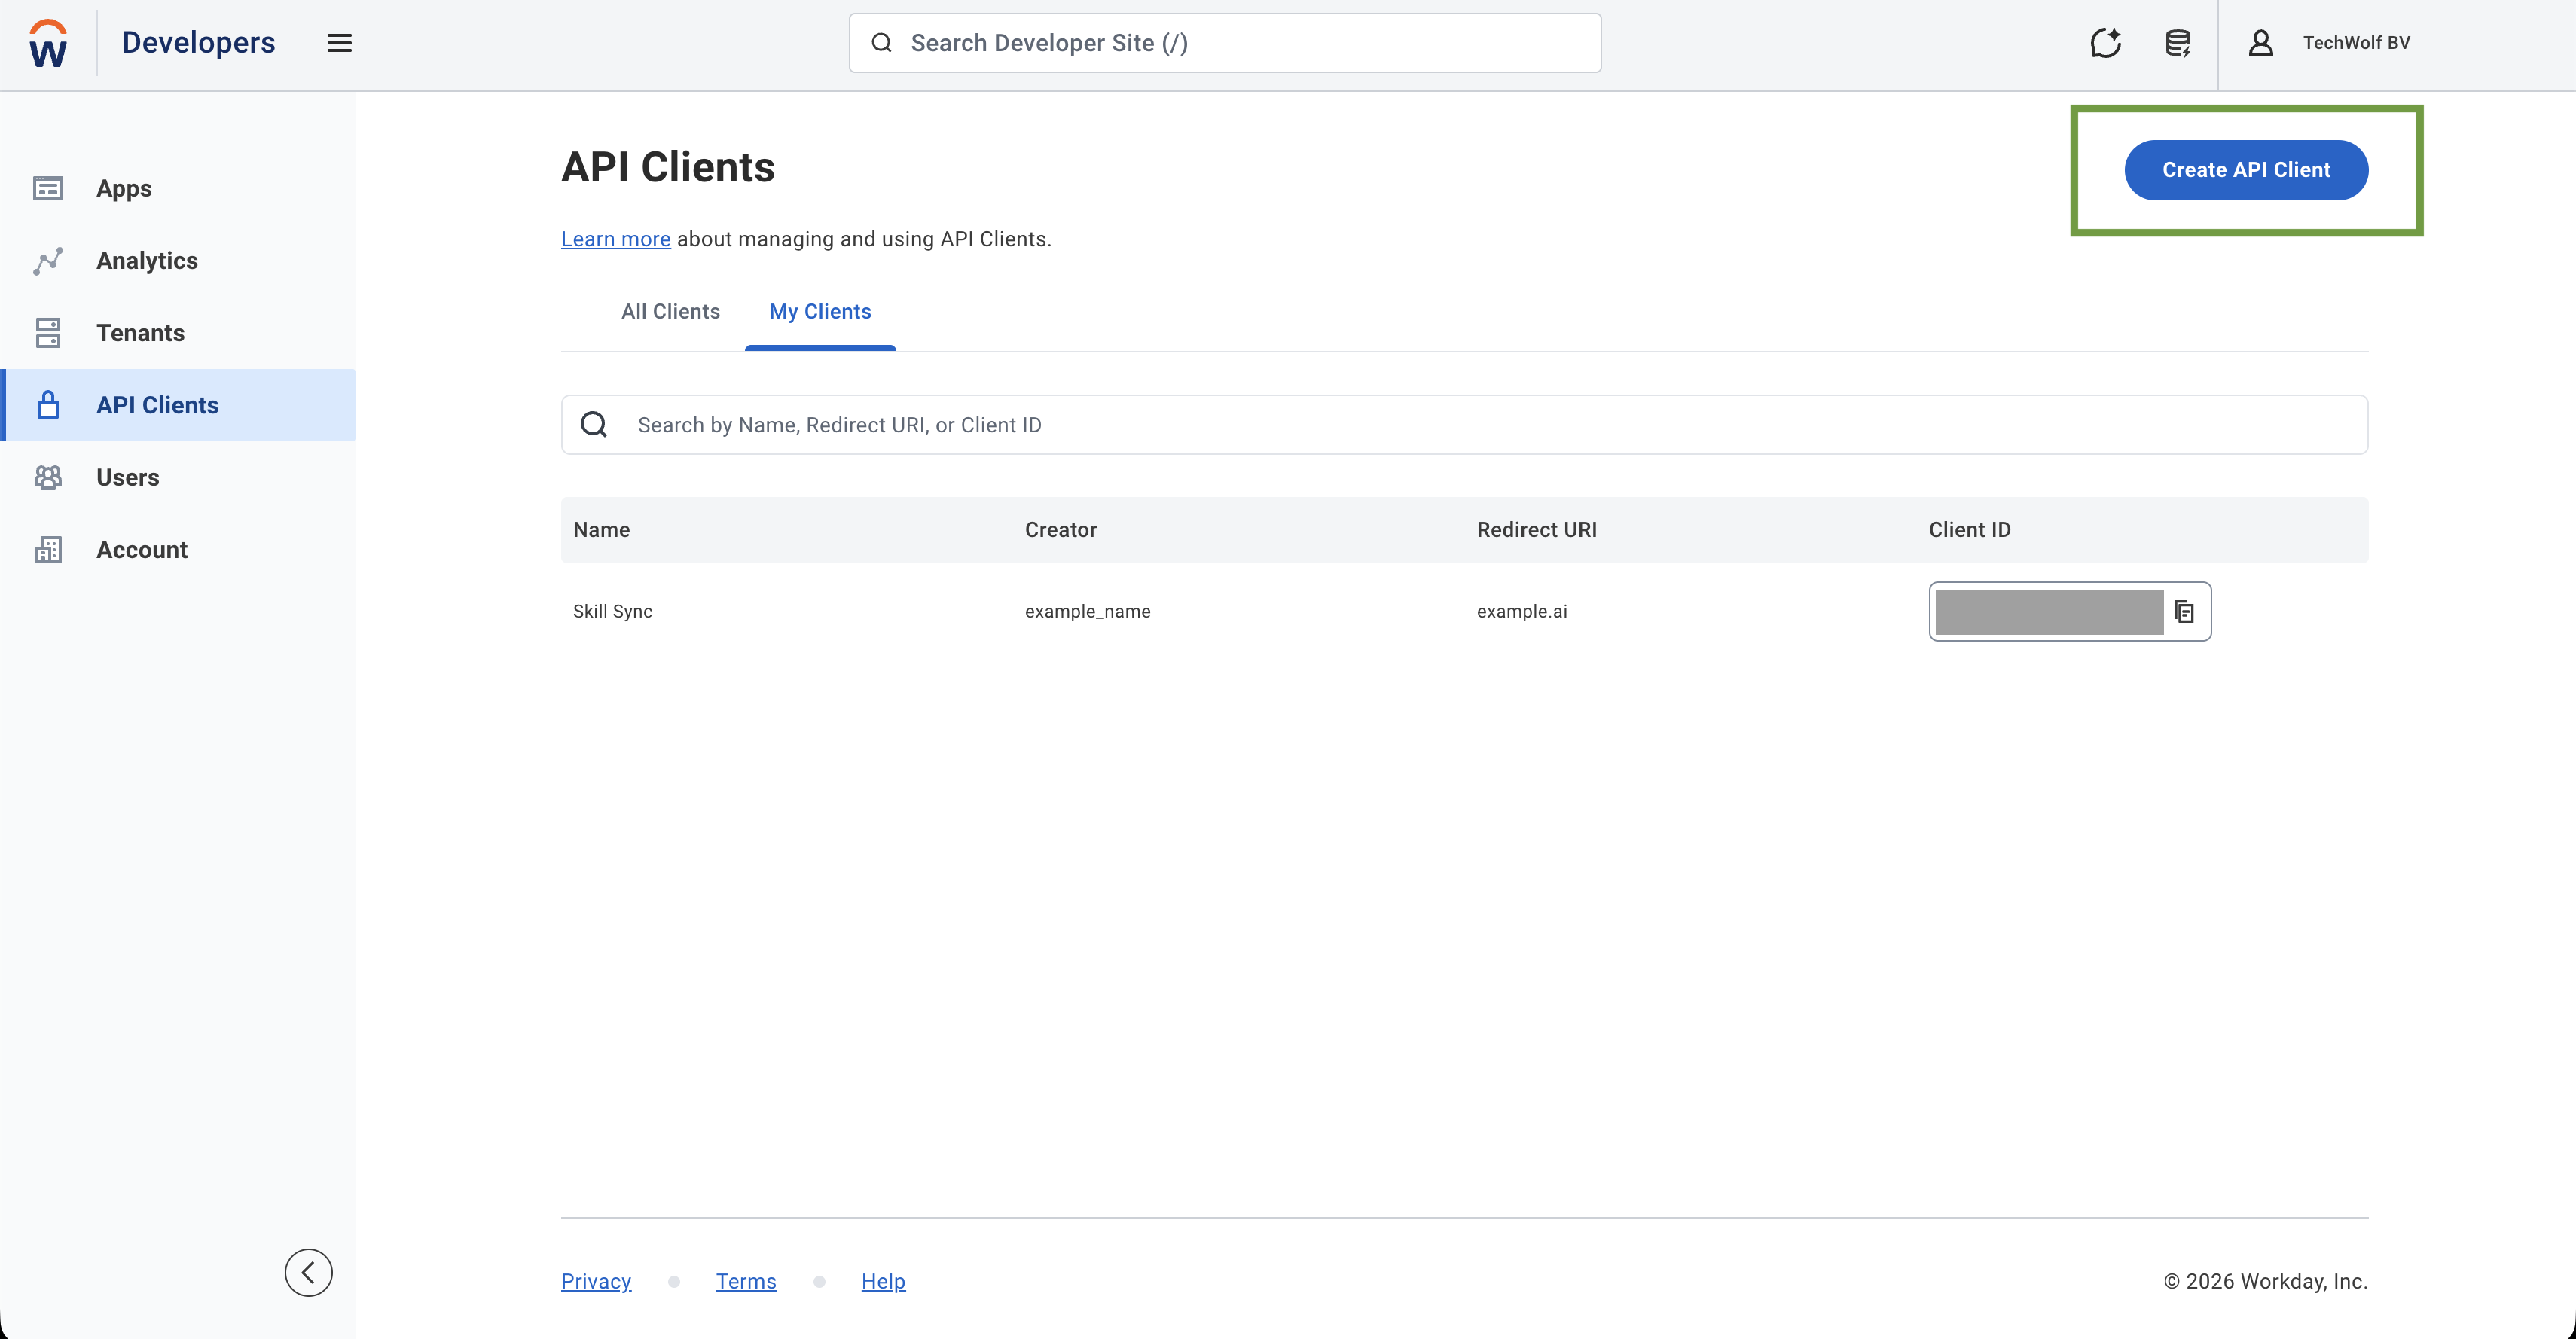
- Select the scopes Staffing, Talent Core and Talent Marketplace.
- Redirect URI and CORS are required, but this flow uses neither. Any value
works, such as your company’s own domain.
- The client secret is shown once, when the client is created. Store it
securely then. If it is lost,
Generate New Client Secreton the client creates a new one and retires the old one.
3
Authorize a non-development tenant
Only a Company Administrator can do this. Development tenants are authorized
automatically and skip this step.
- On the API client, select
Modify Authorized Tenants.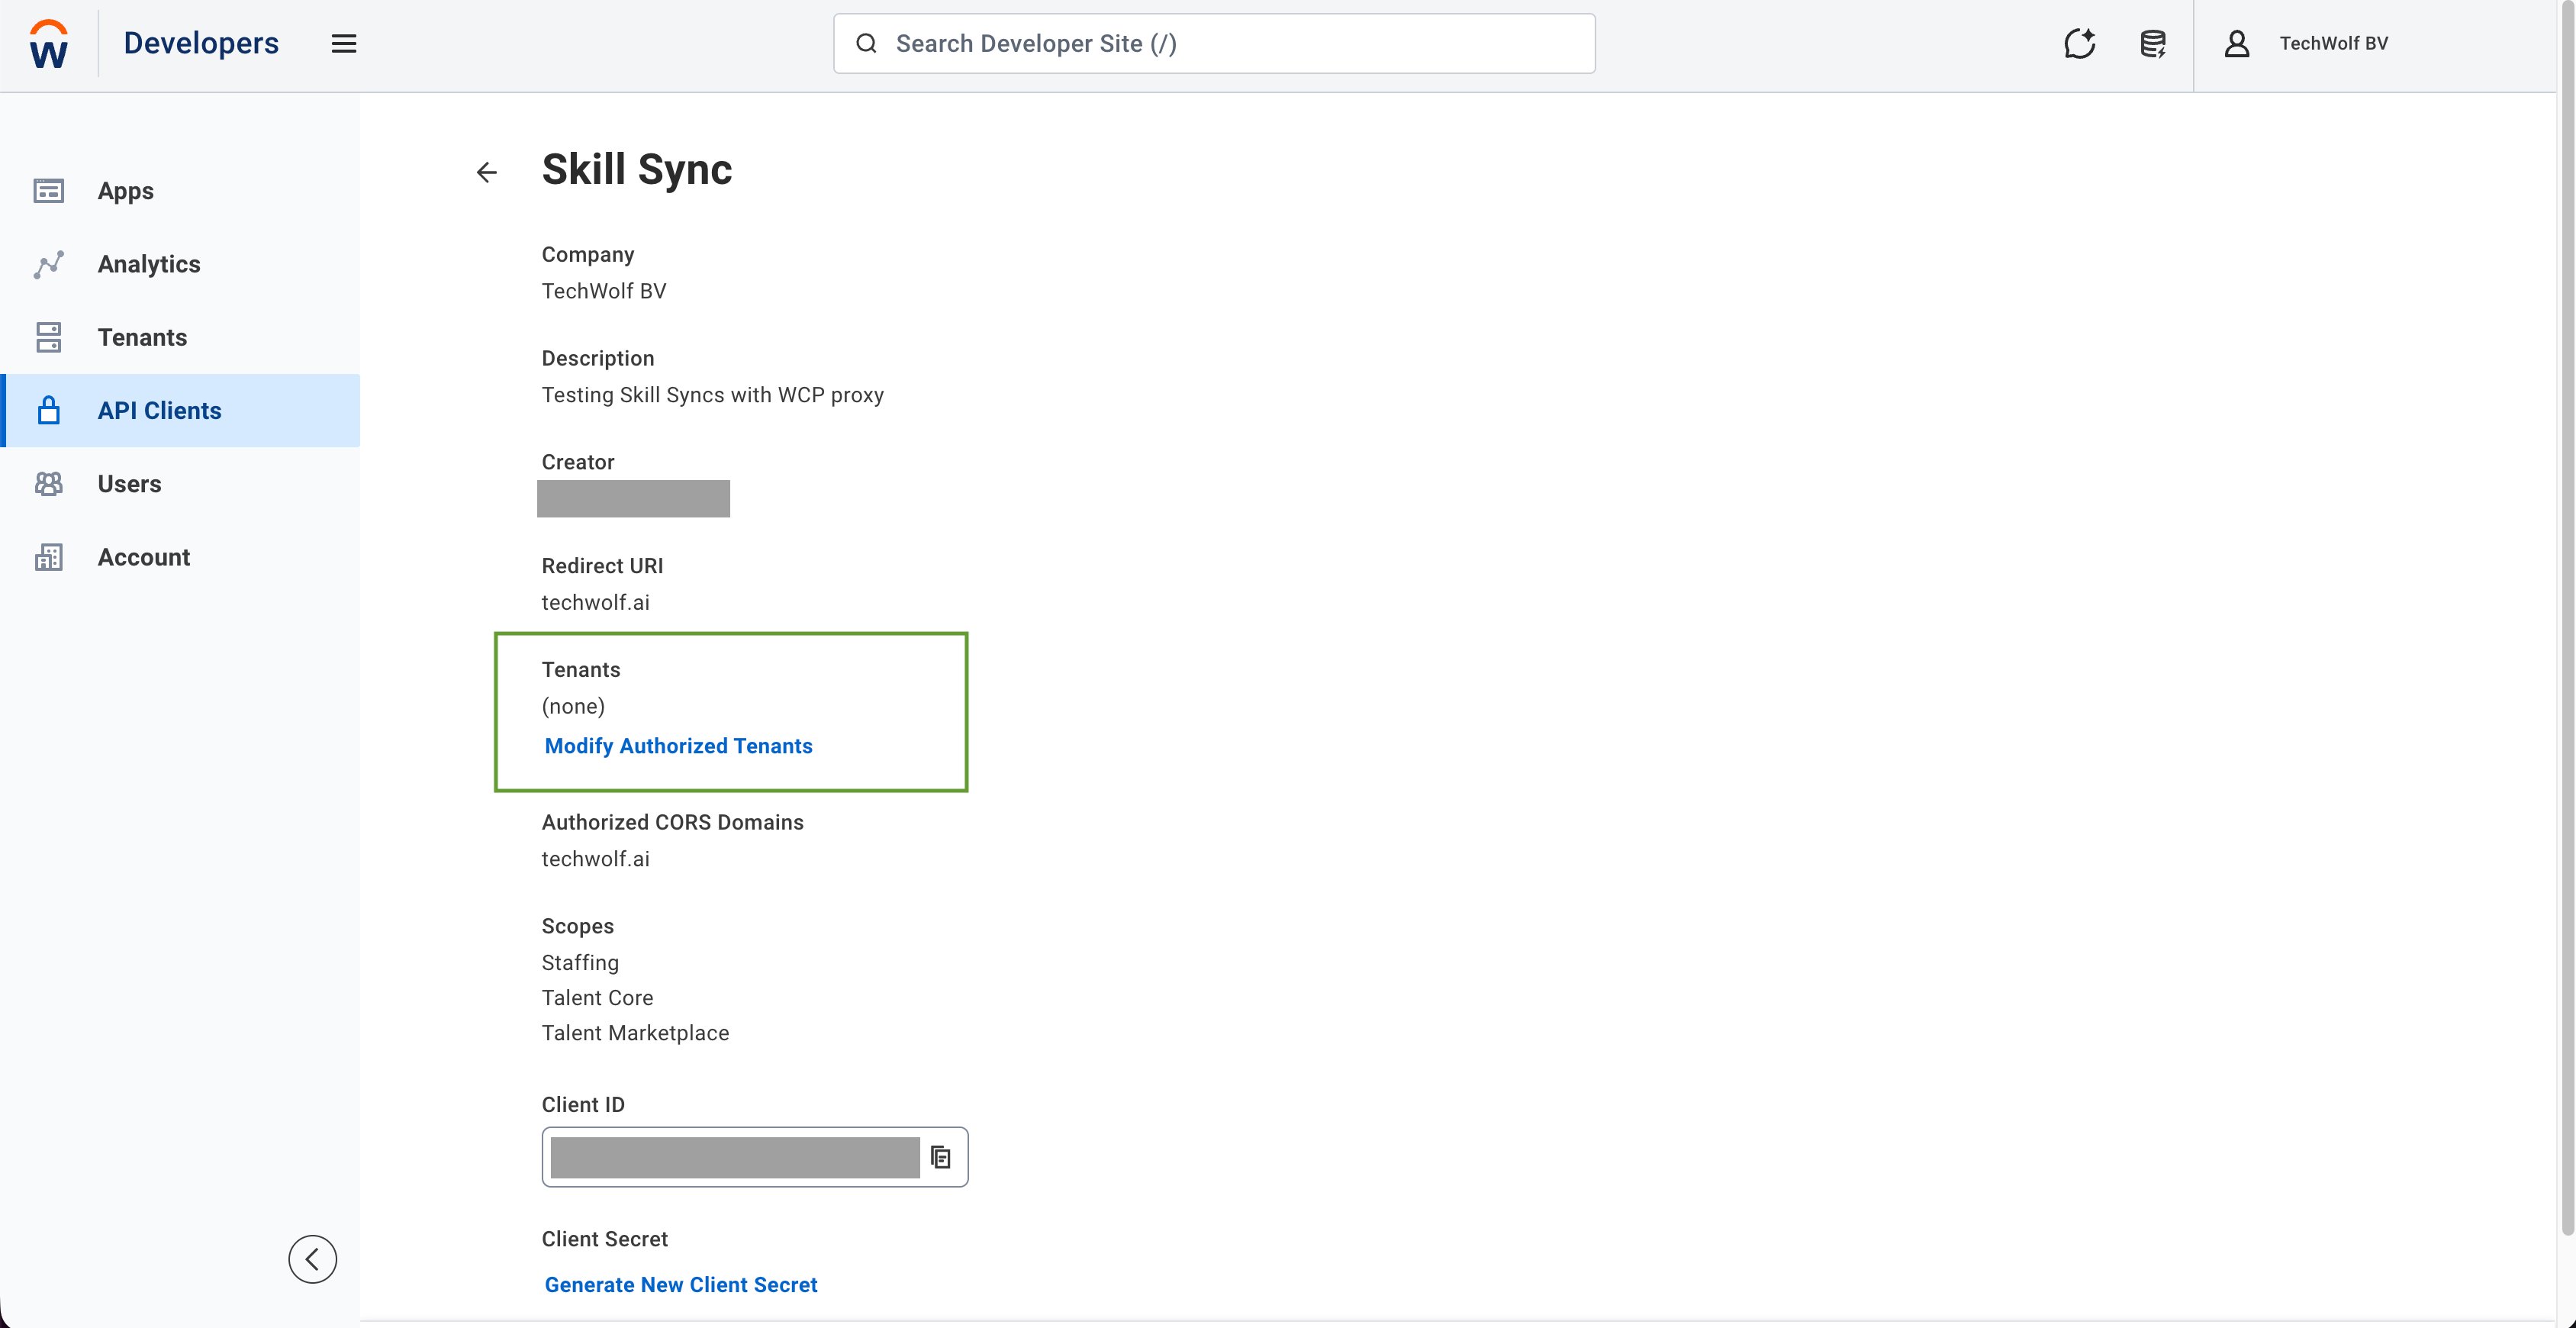
- Pick the tenant from the list and select
Save Changes.
4
Find the tenant alias
The Tenants page from the first step shows the alias in the Tenant Alias column.
For a production, implementation or sandbox preview tenant, the alias is the
tenant name. For a sandbox tenant, it is the tenant name followed by
-sb.5
Find the region
Open the account menu at the top right of the Developer Site. The entry of your
company shows its region.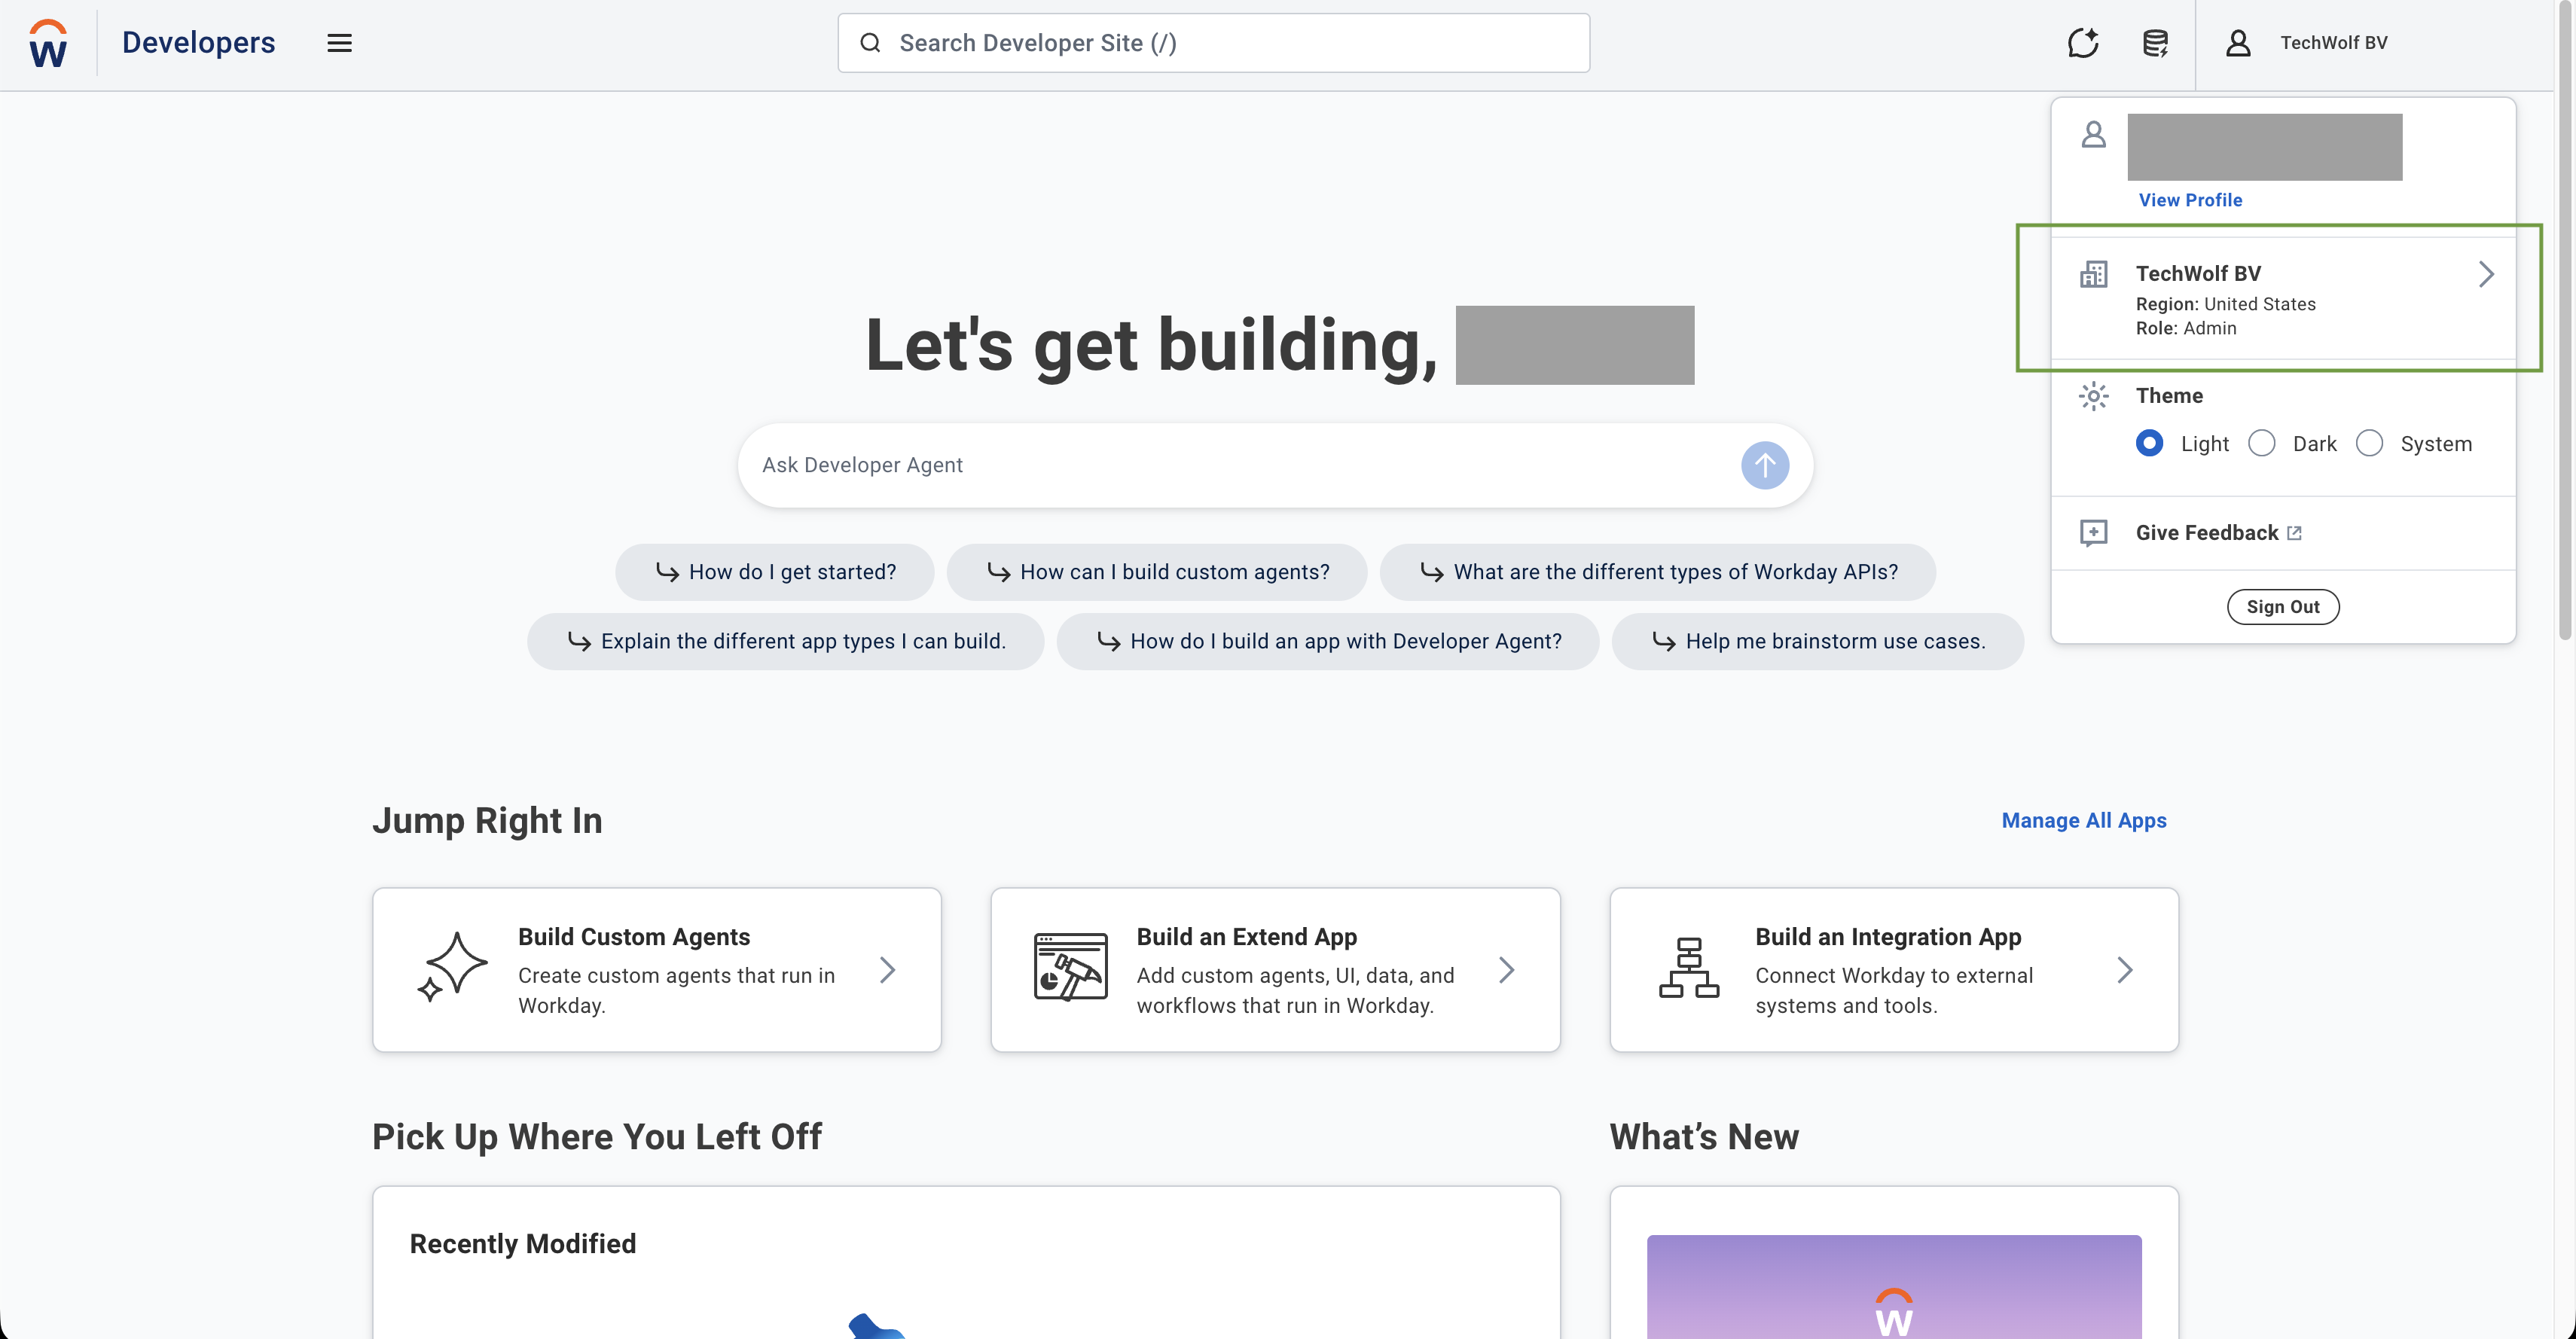
6
Map the API client to the ISU
In the Workday tenant, run the 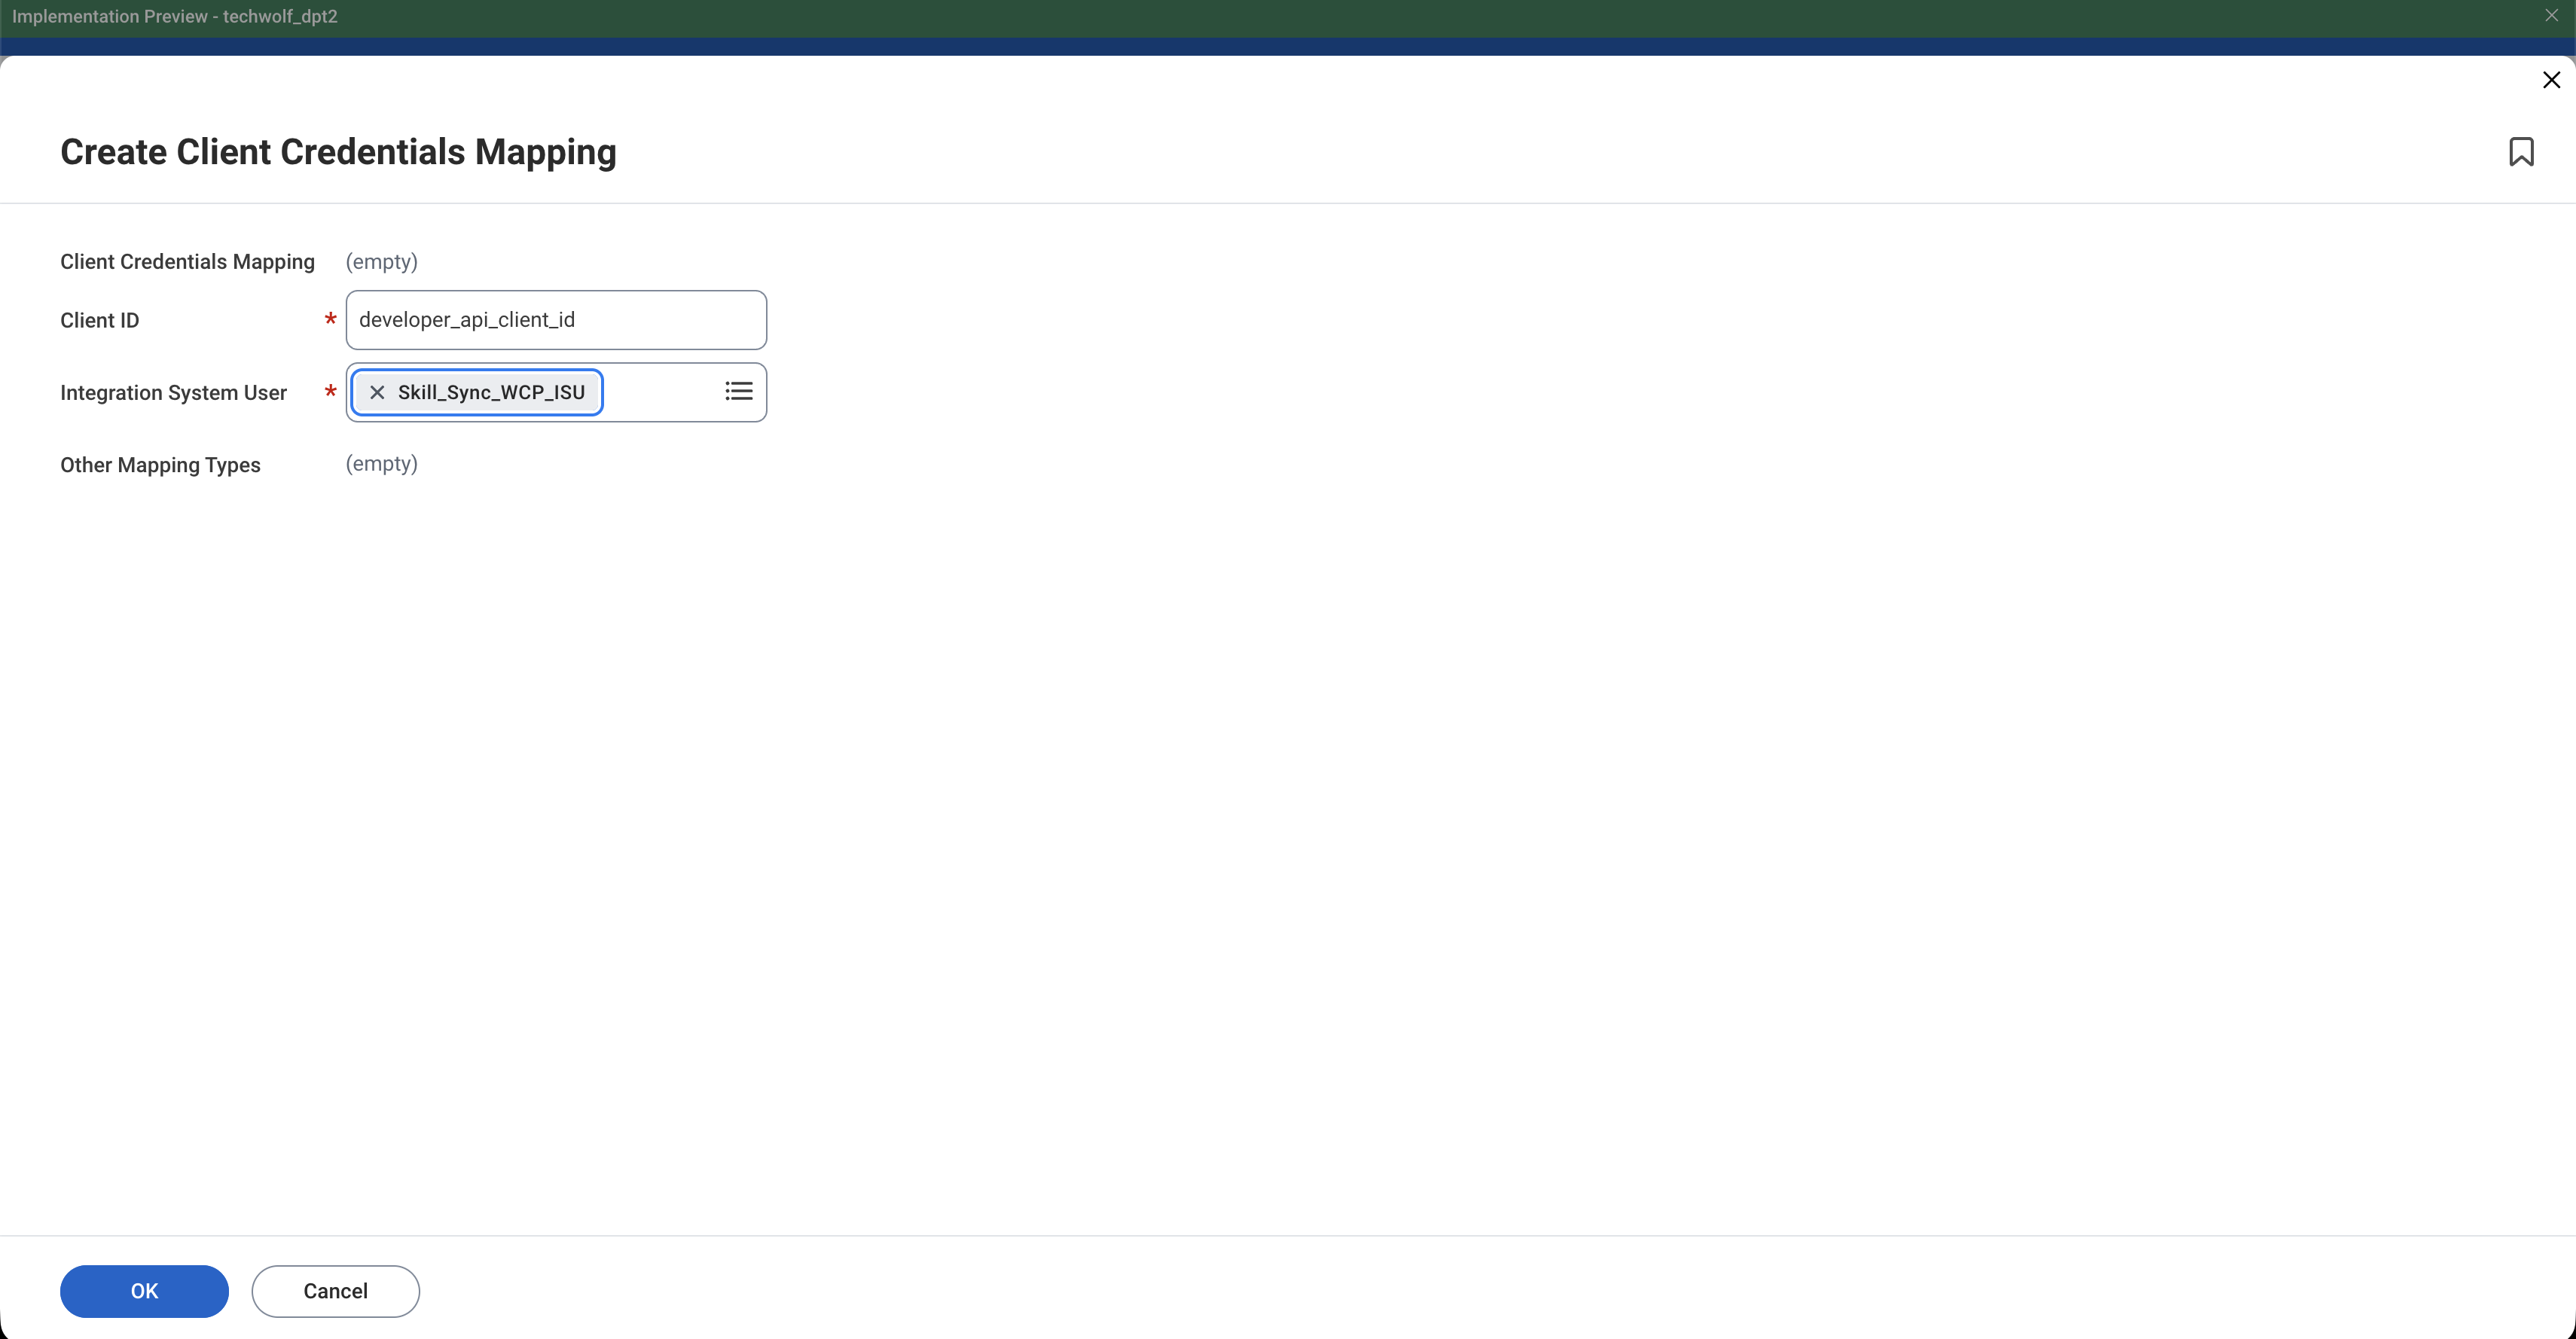
Create Client Credentials Mapping task:- Client ID: the ID of the API client you created on the Developer Site. Using WCP does not require an API client in the tenant itself.
- Integration System User: the ISU from the General setup.
View Client Credentials Mapping to see what was saved. See
Authenticate Using the Client Credentials Grant Type.Console Configuration
This integration is configured self-service in the TechWolf Console:- Enter the connection details of your chosen method. Further explanation
specified in section beneath
Linking Workday & TechWolf
- OAuth through Direct Tenant Communication: Workday API URL, client ID, client secret, and refresh token
- OAuth through the WCP gateway: client ID, client secret, tenant alias and region
- Run the connection validation. It verifies each layer separately: the credentials (token fetch), read access (profile fetch), and update access — a reversible test write that appends a marker to one job profile’s description, confirms it, and restores the original.
- Enable the integration.
Choosing the validation job profile. The validation asks for the ID of a
job profile to test against, and remembers it for later validations. Pick a
low-traffic or seperate test profile — each validation shows up as a Manage
Job Profile event in that profile’s history.
Linking Workday & TechWolf
Jobs are matched on the same identifier configuration as the Job Skill Sync: either Workday Job Codes (Job Profile IDs) or Workday IDs (WIDs), matching the Jobexternal_id in TechWolf. If you run both integrations, they share this
setting.
Deployment Tasks & Responsibilities
- Customer: Create the Integration System User and grant the permissions described above (for existing Job Skill Sync tenants: only the business process permission).
- Customer: In the TechWolf Console, enter the connection details and the
ID of the Job Profile we use during validation, then run the validation:
- OAuth through Direct Tenant Communication: Workday API URL, client ID, client secret, and refresh token
- OAuth through the WCP gateway: client ID, client secret, tenant alias and region
- TechWolf: Potentially follow the first synchronization and confirm go-live with the customer.
- Customer: Check end-user test scenarios — publish a job description in the Console and verify it appears on the Workday Job Profile.