

System Requirements
The TechWolf Skills integration will make use of existing Workday functionality. The customer will need a TechWolf contract with a live TechWolf tenant. This TechWolf tenant must be populated with (a subset of) the Job’s entities in Workday. Additionally, Workday’s Synonym Management must be enabled in the Workday tenant, with the correct configuration. For Skills Cloud Skills, the sync only supports canonical Skills, not their synonyms; Synonym Management resolves synonyms to their canonical Skill so profiles remain fully syncable. See Automated Skill Management (Synonym Management) for the required configuration, also as it relates to the optional synchronization of custom skills managed in TechWolf to Workday as Maintained Skills.Workday Configuration
A Workday integration user must be configured in the Workday tenant with an implementation security group.If you already have an Employee Skill Sync integration configured, you can
either set up a new, separate configuration or reuse parts of the existing
one. When reusing the existing setup, the same ISU can be kept, with only
the Permissions needing to be updated in step 4 of the General setup.
Additionally, with Direct Tenant Communication, the API Client scopes also
need to be updated in step 2 of its setup. On the WCP gateway, the Developer
Site API client can be reused unchanged.
Authentication
The integration supports OAuth through Direct Tenant Communication, OAuth through Workday’s API gateway (WCP) and Basic Authentication. Basic Authentication is deprecated and only available on request. If you already have Basic Authentication configured, we continue to support it. Communicate your preference with TechWolf. Every method starts with the General setup. Then complete the setup of your chosen method: the OAuth: Direct Tenant Communication setup, the OAuth: WCP gateway setup or the Basic Authentication setup. The Custom Skill Sync has no credentials of its own. It uses those of the Employee or Job Skill Sync it runs with. What you’ll share with TechWolf: If you choose OAuth through Direct Tenant Communication:- Workday API URL
- Token URL
- Client ID
- Client secret
- Refresh token
- Client ID
- Client secret
- Tenant alias
- Region
- Workday API URL
- Username
- Password
General setup
1
Create Integration System User (ISU)
-
Create Integration System Userbusiness process. - Do not allow UI sessions as this user will only be used for automations.
- Please securely store the username and password of this user.
-
Set the ISU’s language preferences: The integration requires the ISU’s
locale and display language to be English (United States); this language
preference can be set when proxying as the ISU. Note that ISUs do not show up
in the
Start Proxytask. Instead, starting the proxy can be done by running theAll Workday Accountsreport, filtering the “User Name” column on the ISU’s username, and then, from the account’s related actions, choosing “Security Profile” > “Start Proxy”.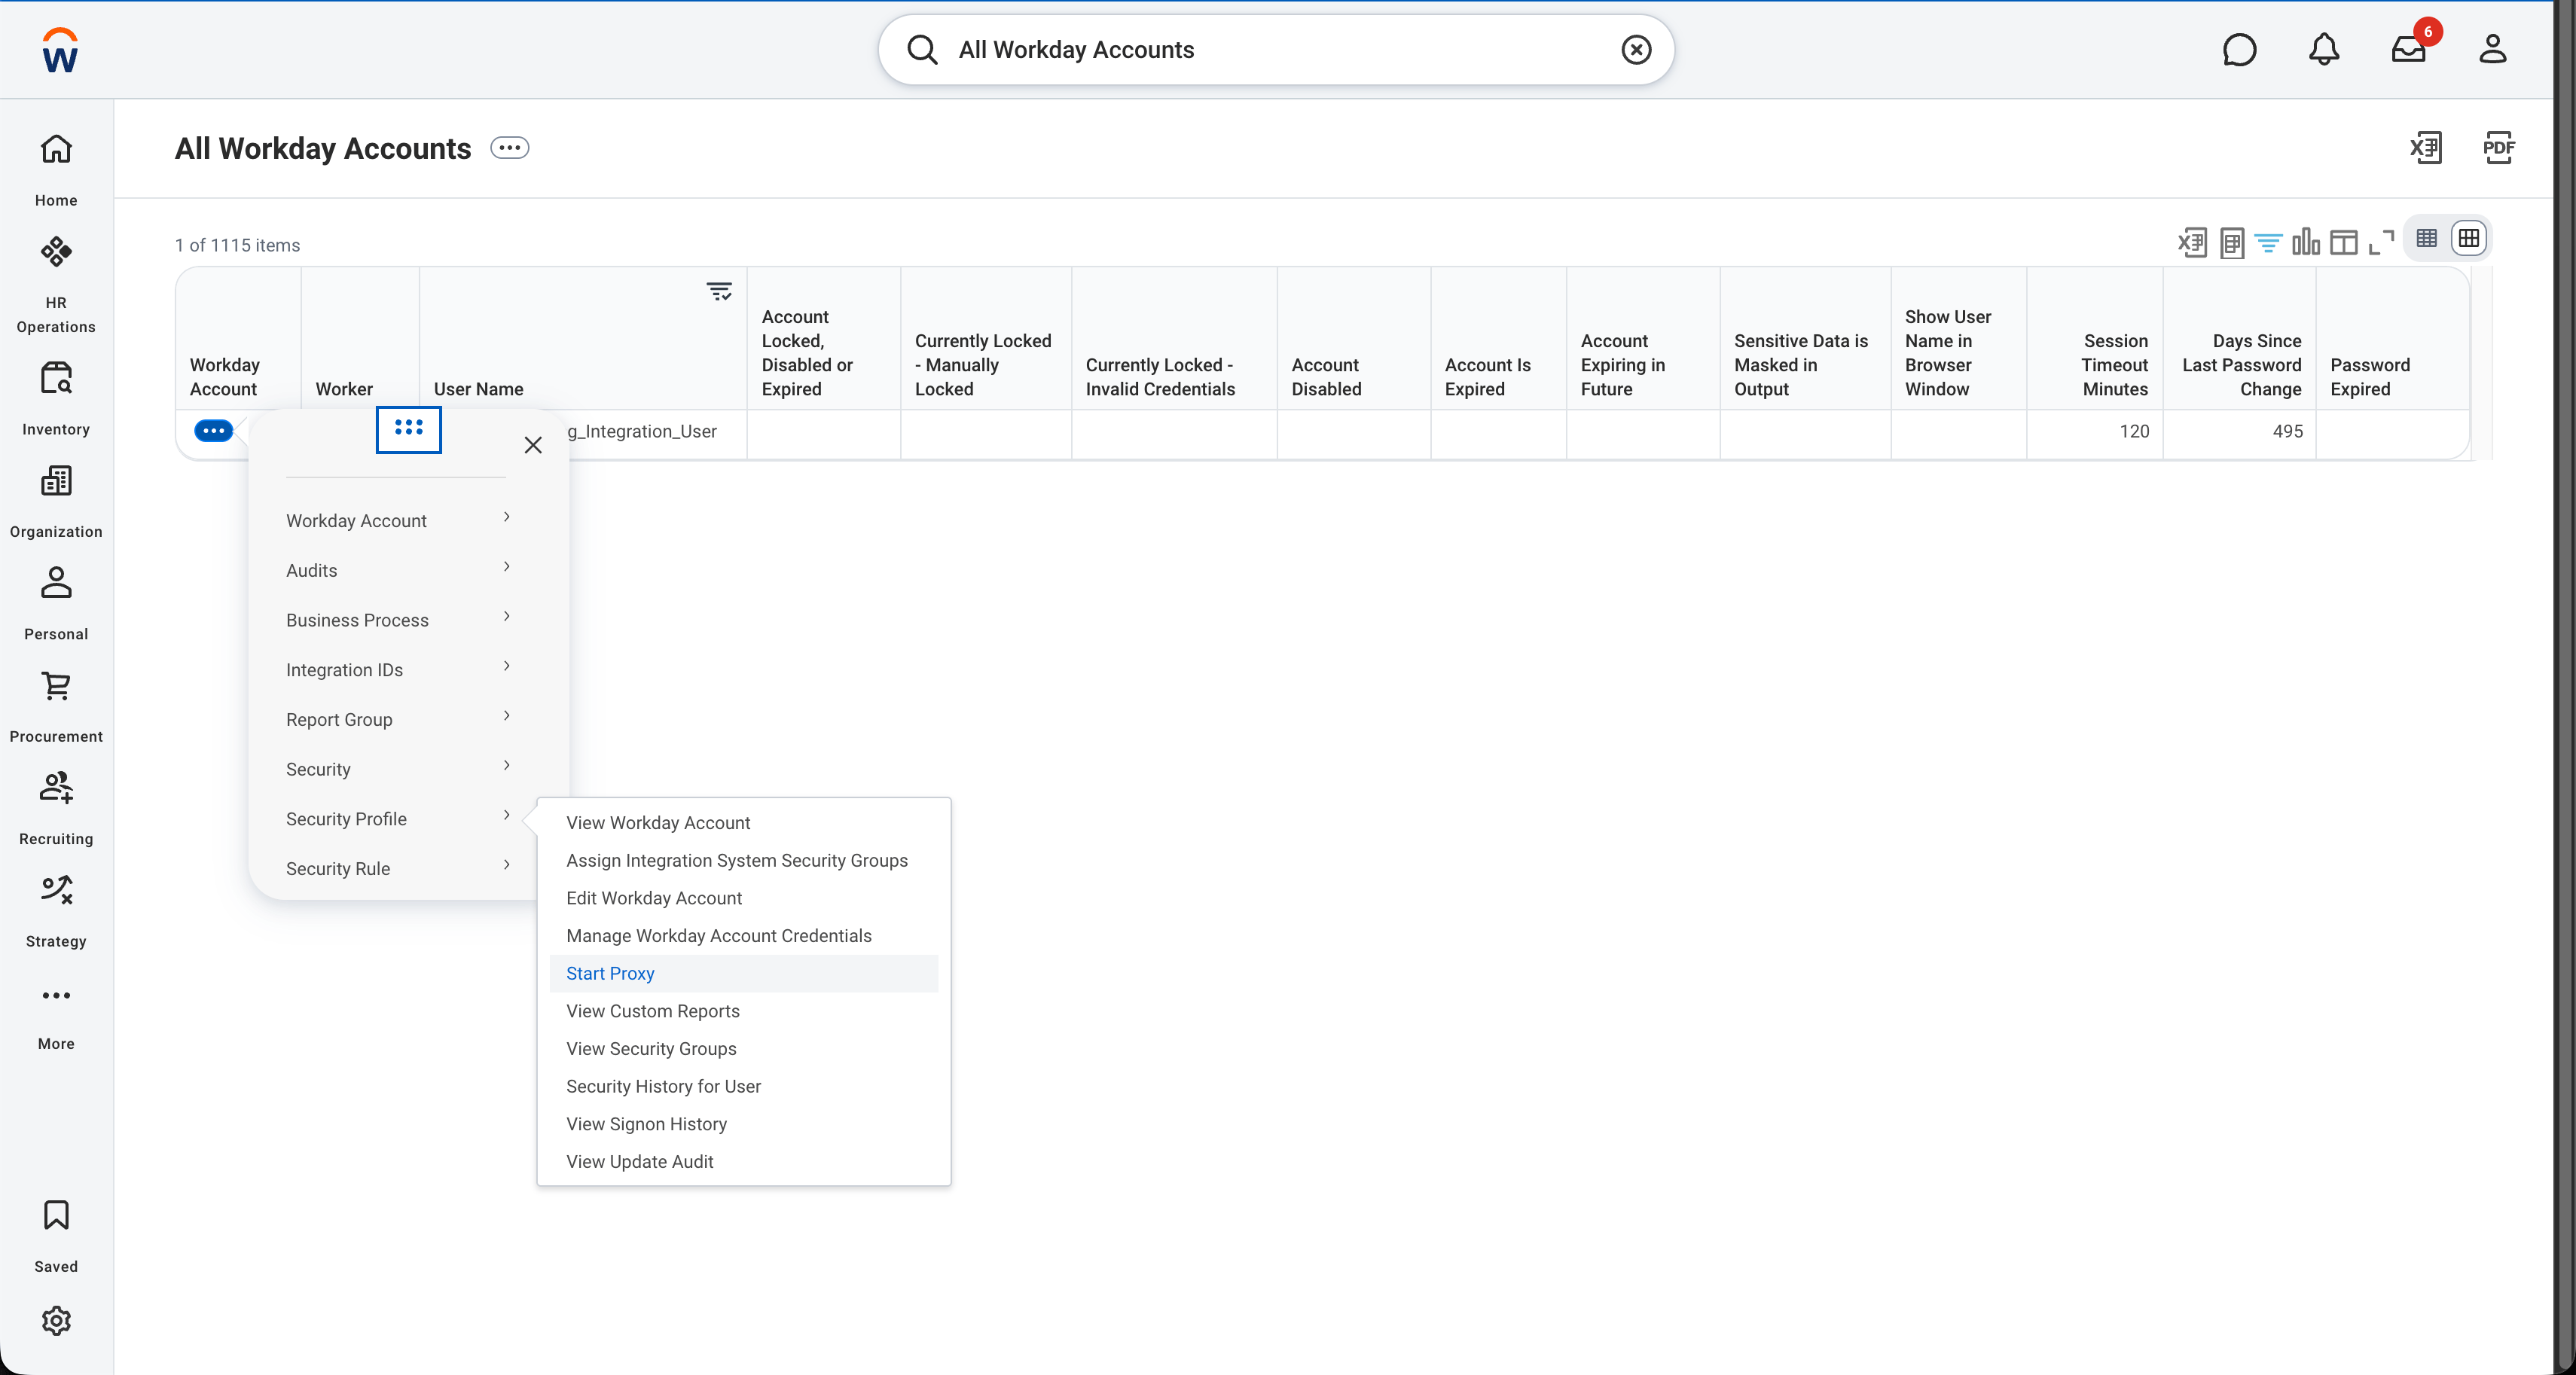
Change Preferencestask and set the fields from the table below: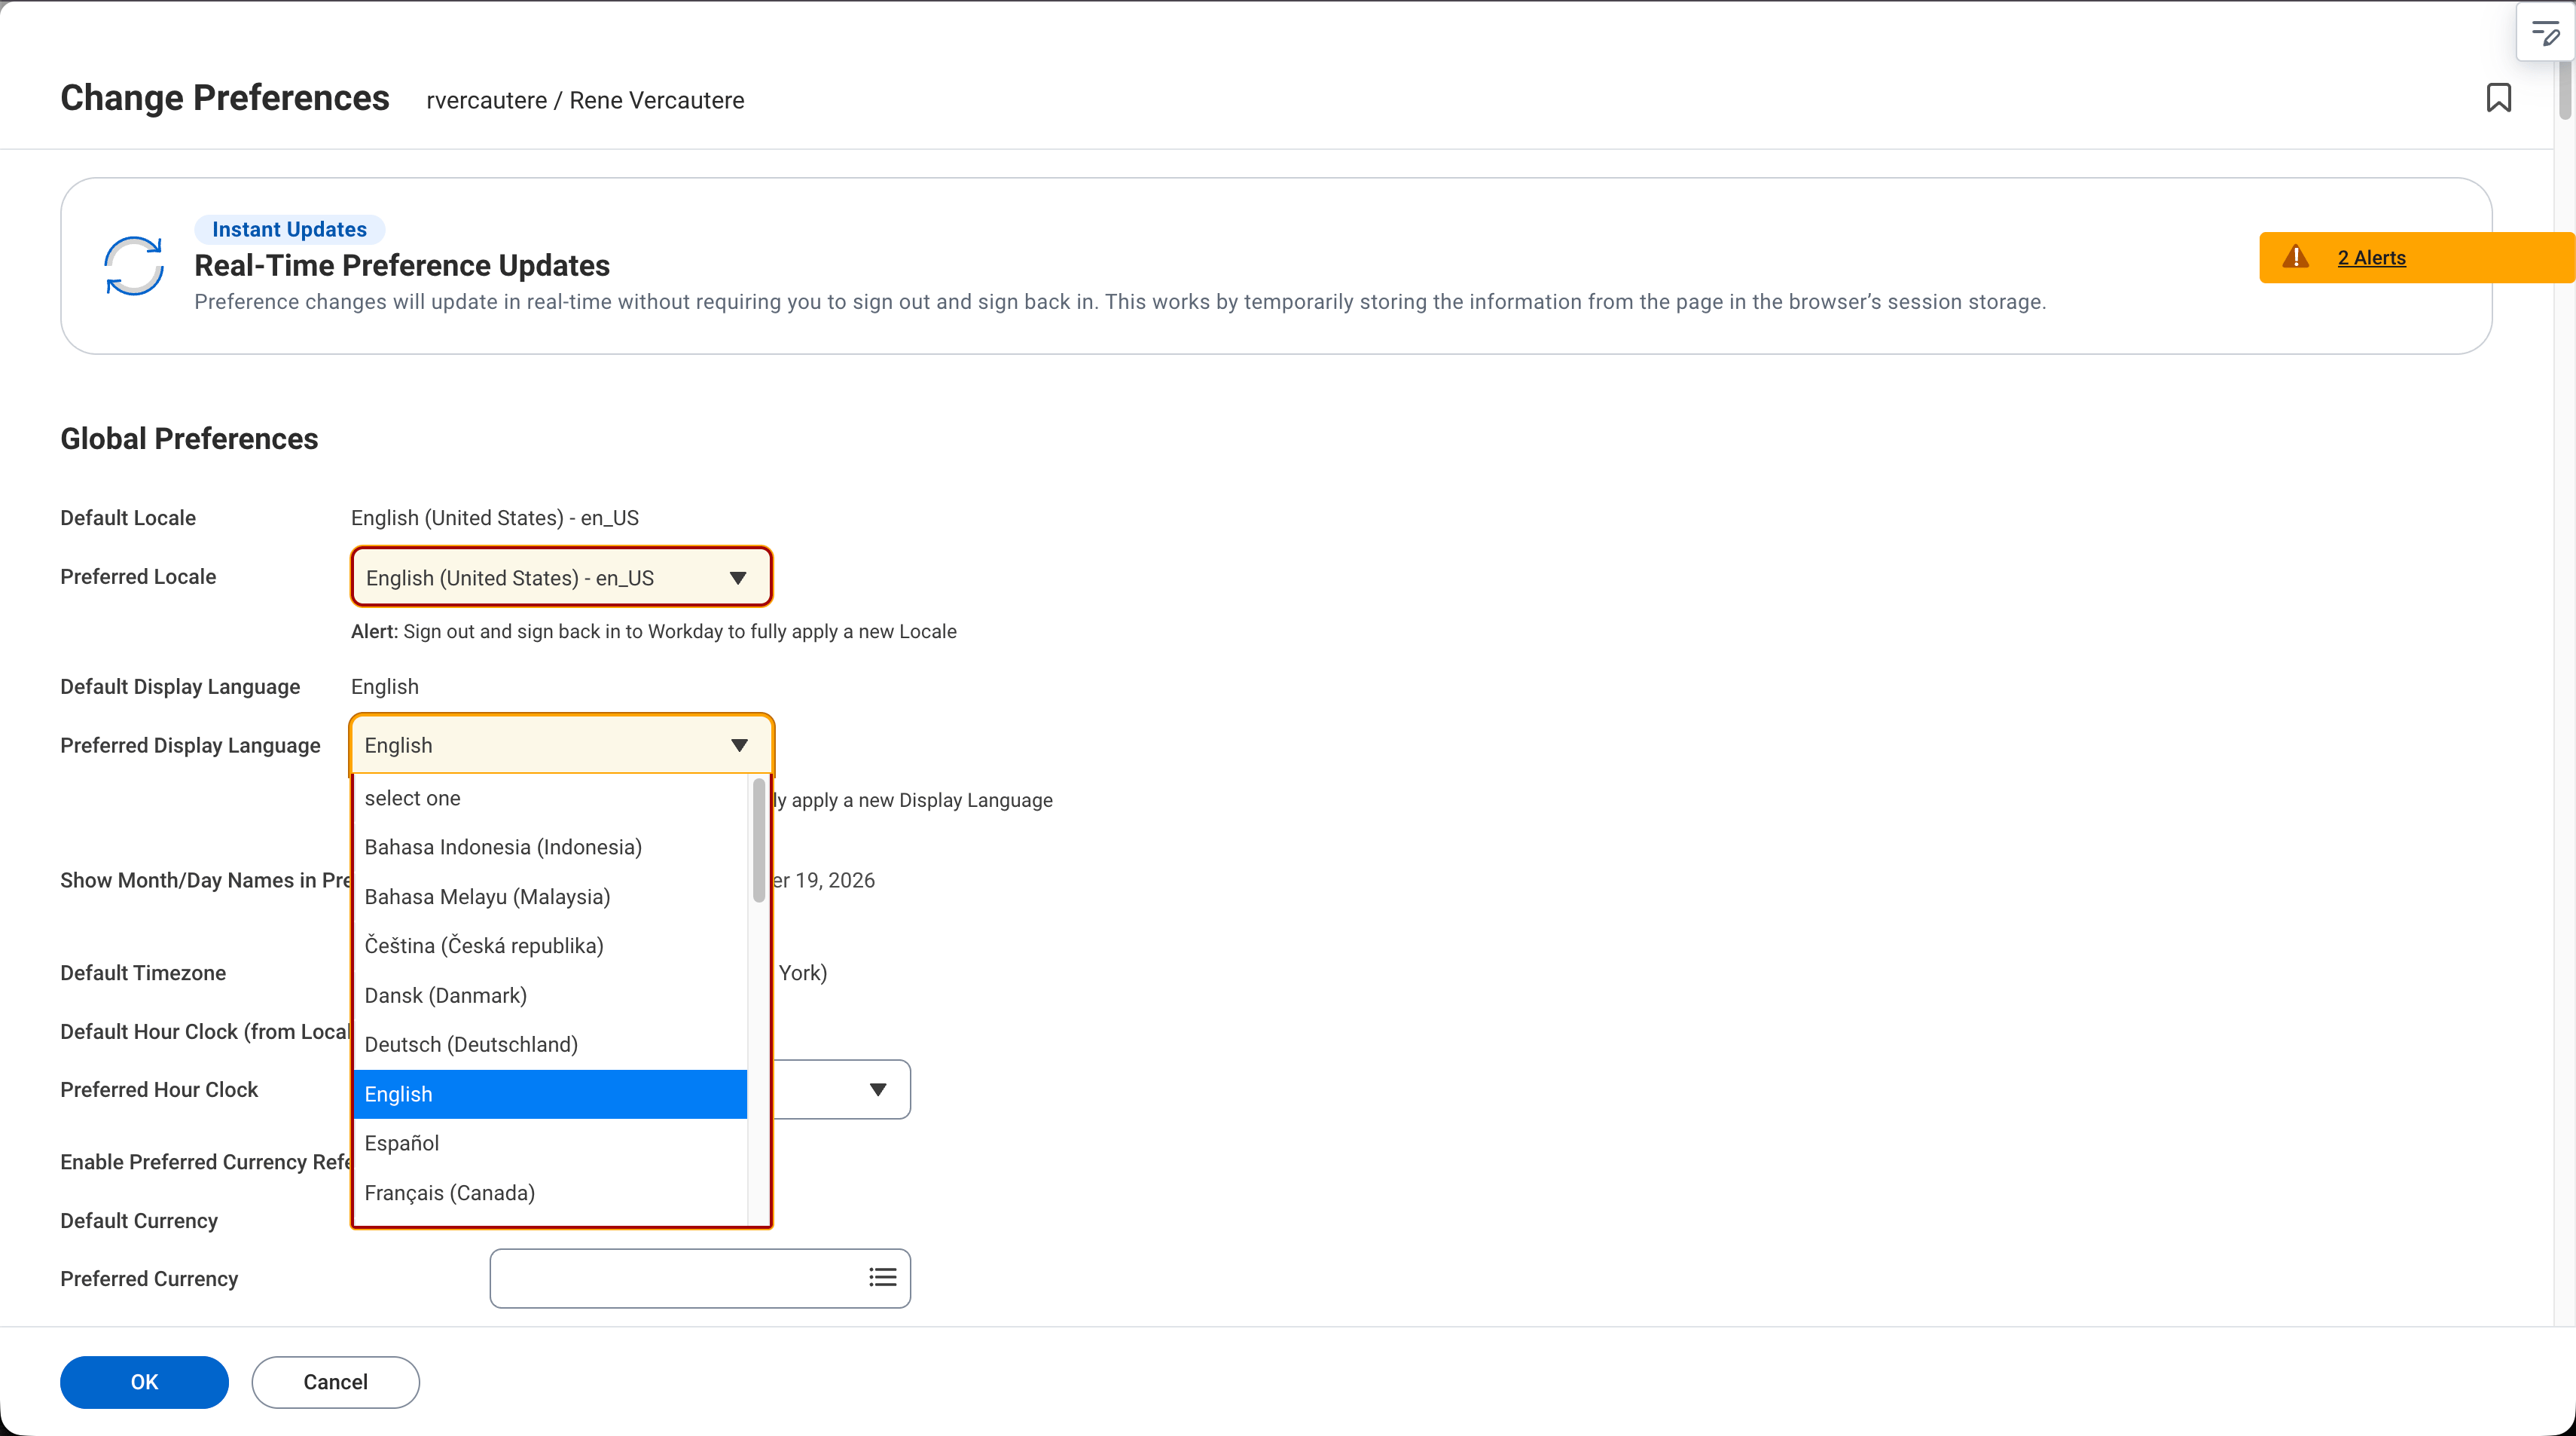
Stop Proxytask.
2
Update password expiration rules for ISU
-
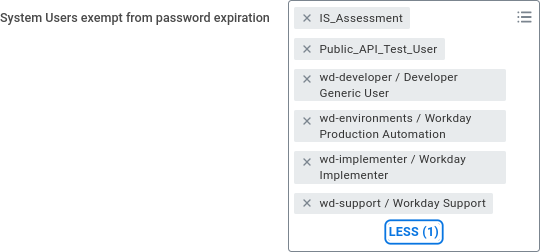
In the
Maintain Password Rulesbusiness process under “System Users exempt from password expiration” add the newly created ISU to the list. -
Note: This ensures the integrations will keep running without
interruptions due to password expiration.
3
Set up security permissions for the ISU through security policies
-
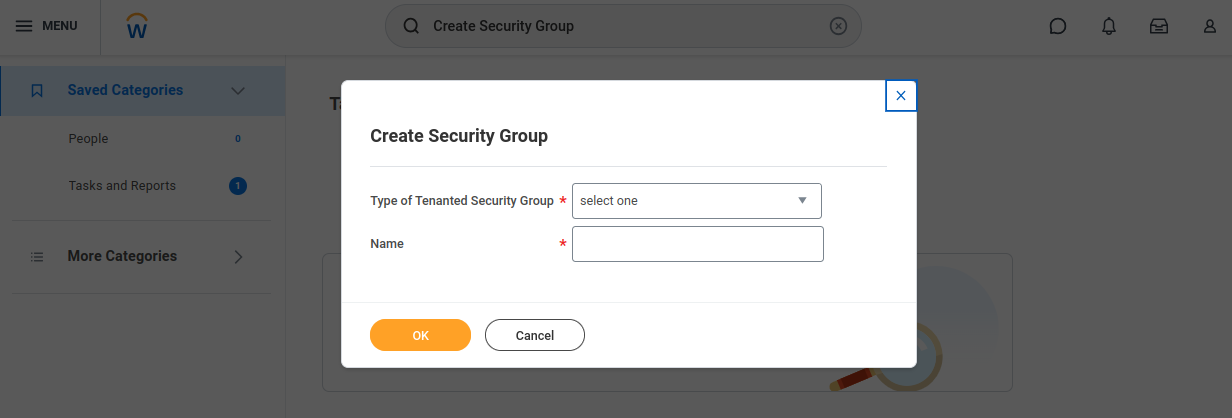
Go to
Create Security Group, choose “Integration System Security Group (Unconstrained)”. -
Note on acceptance testing: Consider using two different security groups,
one Unconstrained and one Constrained. This way, the test-set is scoped while
the correct permissions are applied for other Web Services.
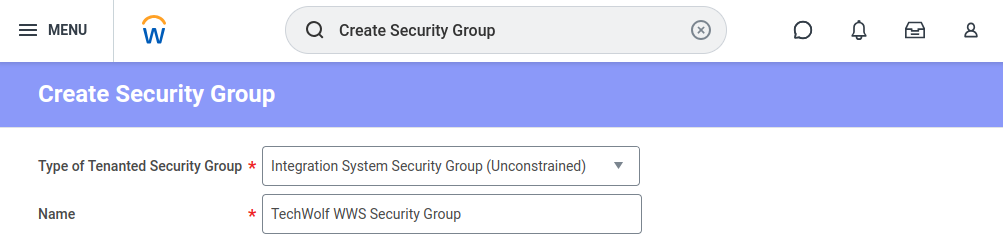
-
The next screen presents you with an Edit form to add additional information.
Add your ISU to the list. This can be changed later too. Do not check
“Inactive”.
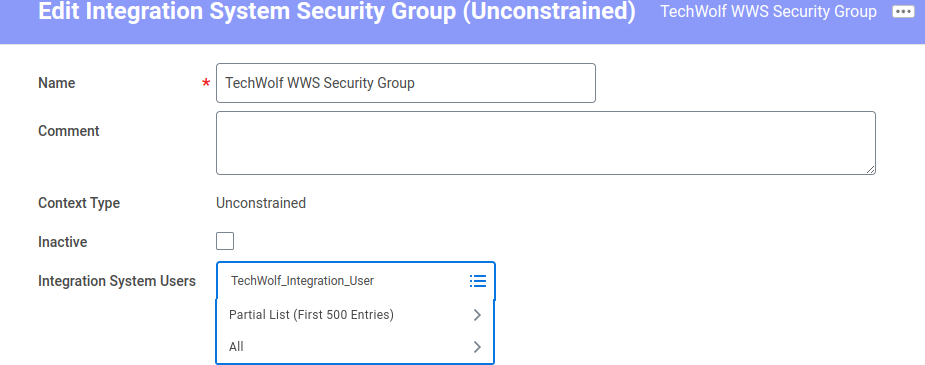
4
Edit the Security Group's domain security policies
- Search for “View Security Group” and select your created security group.
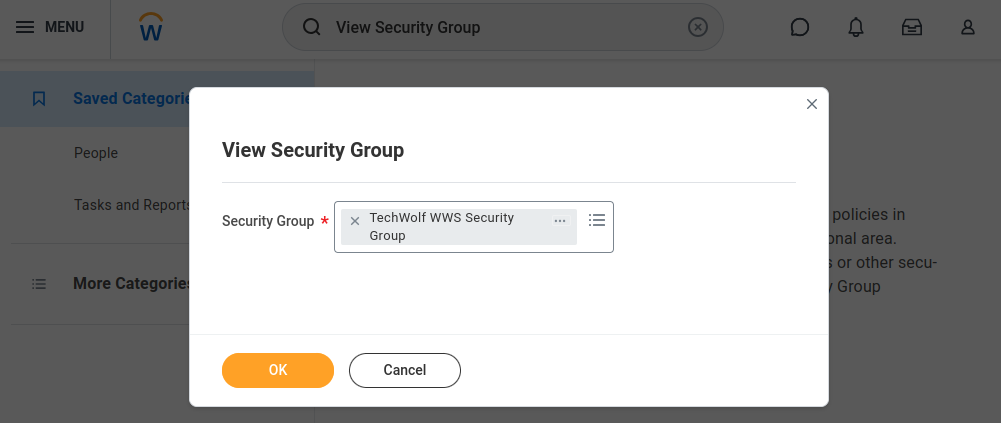
- Select the option menu next to the Security Group’s name, go to “Security
Group” and select “Maintain Domain Permissions for Security Group”.
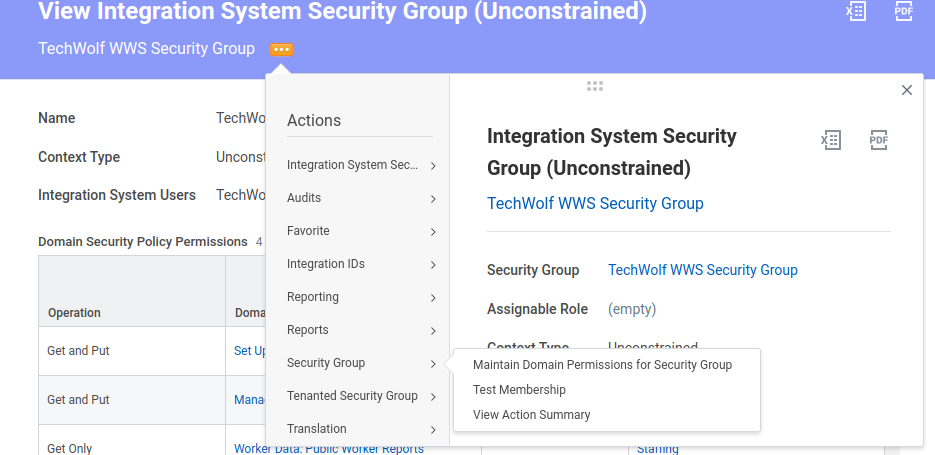
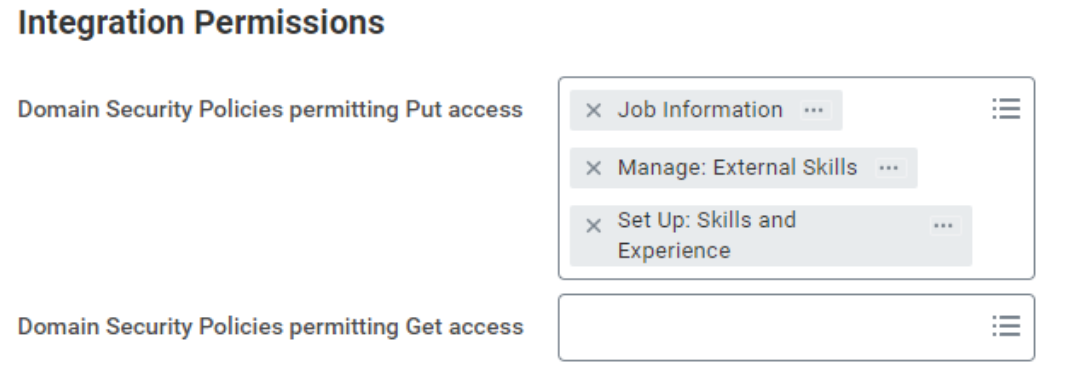
- Under Integration Permissions add the following Domain Security Policies, and
run the
Activate Pending Security Policy Changestask to apply the changes.
OAuth: Direct Tenant Communication setup
1
Find out the correct Workday API URL
-
Search for
Public Web Servicesin the search bar at the top of the Workday home page. -
In the list, click the three dots next to the
Human Resources (public)entry. SelectView WSDLunderWeb Service.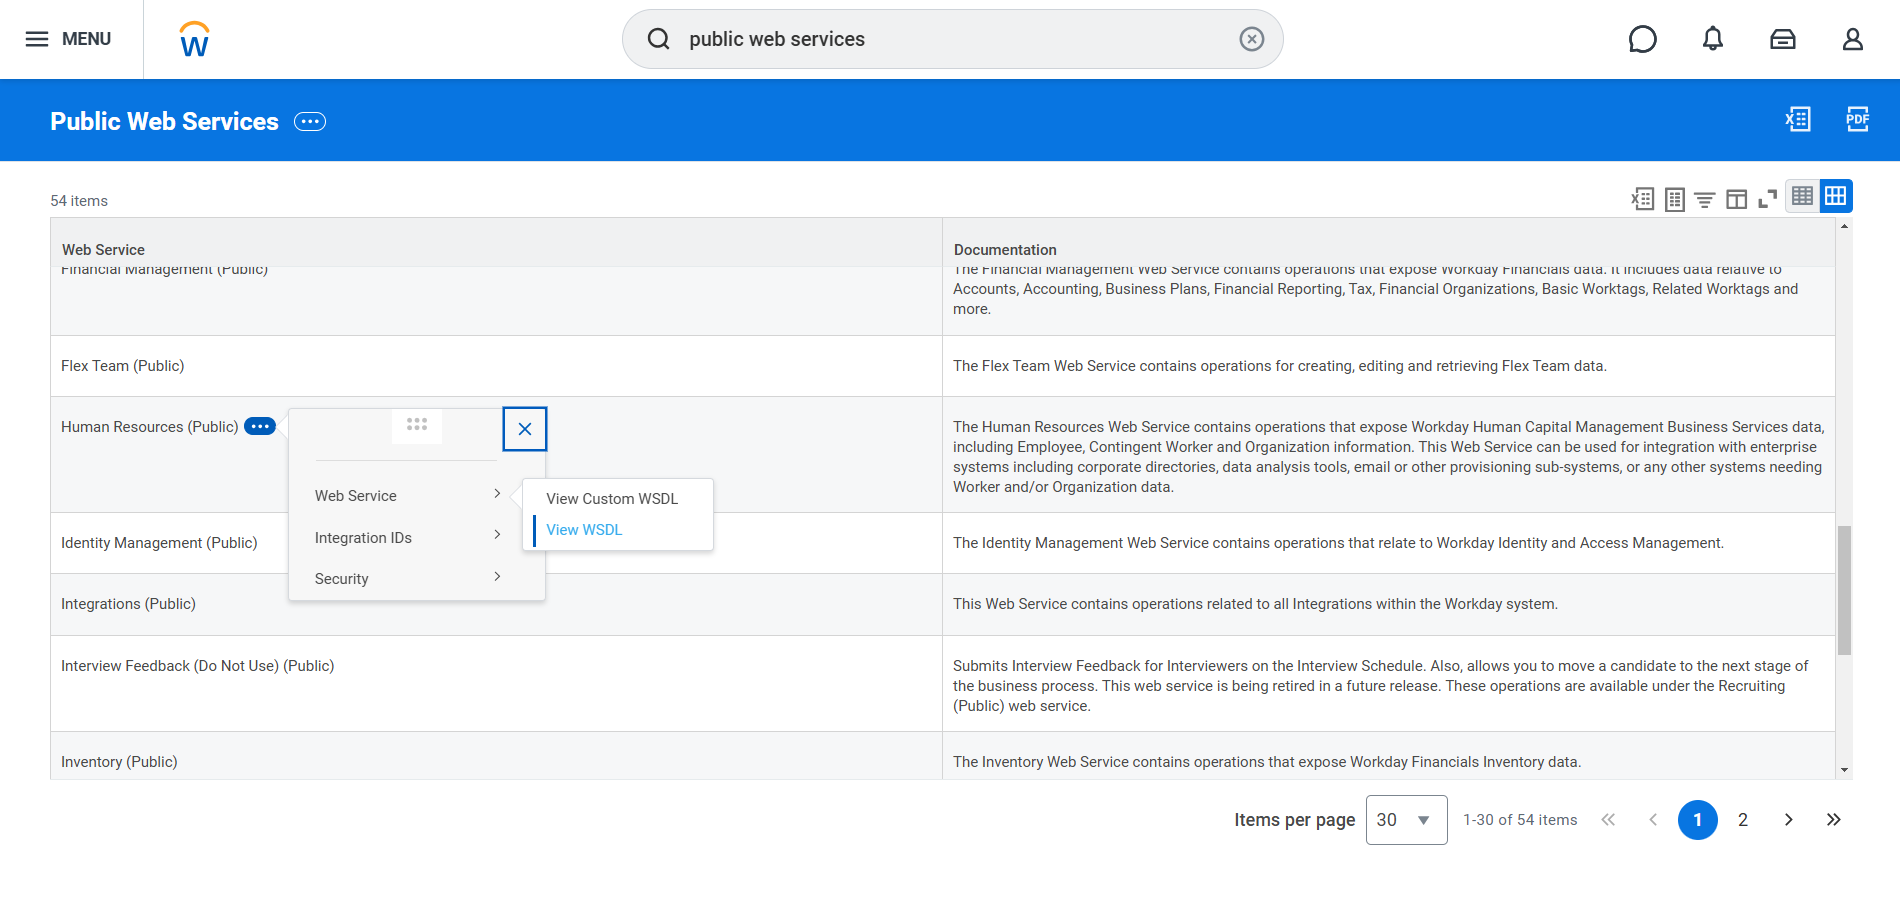
-
The resulting page will take some time to load. Once it is loaded, look for
“soapbind:address location” near the bottom of the page. You will see a
section like this:
- Copy the base tenant URL up to and including your tenant name. The service name and version should be excluded from the URL.
- Note that the API URL can differ between implementation tenants and production tenants, so the steps described above need to be repeated for each tenant individually.
2
Create API Client for Integrations
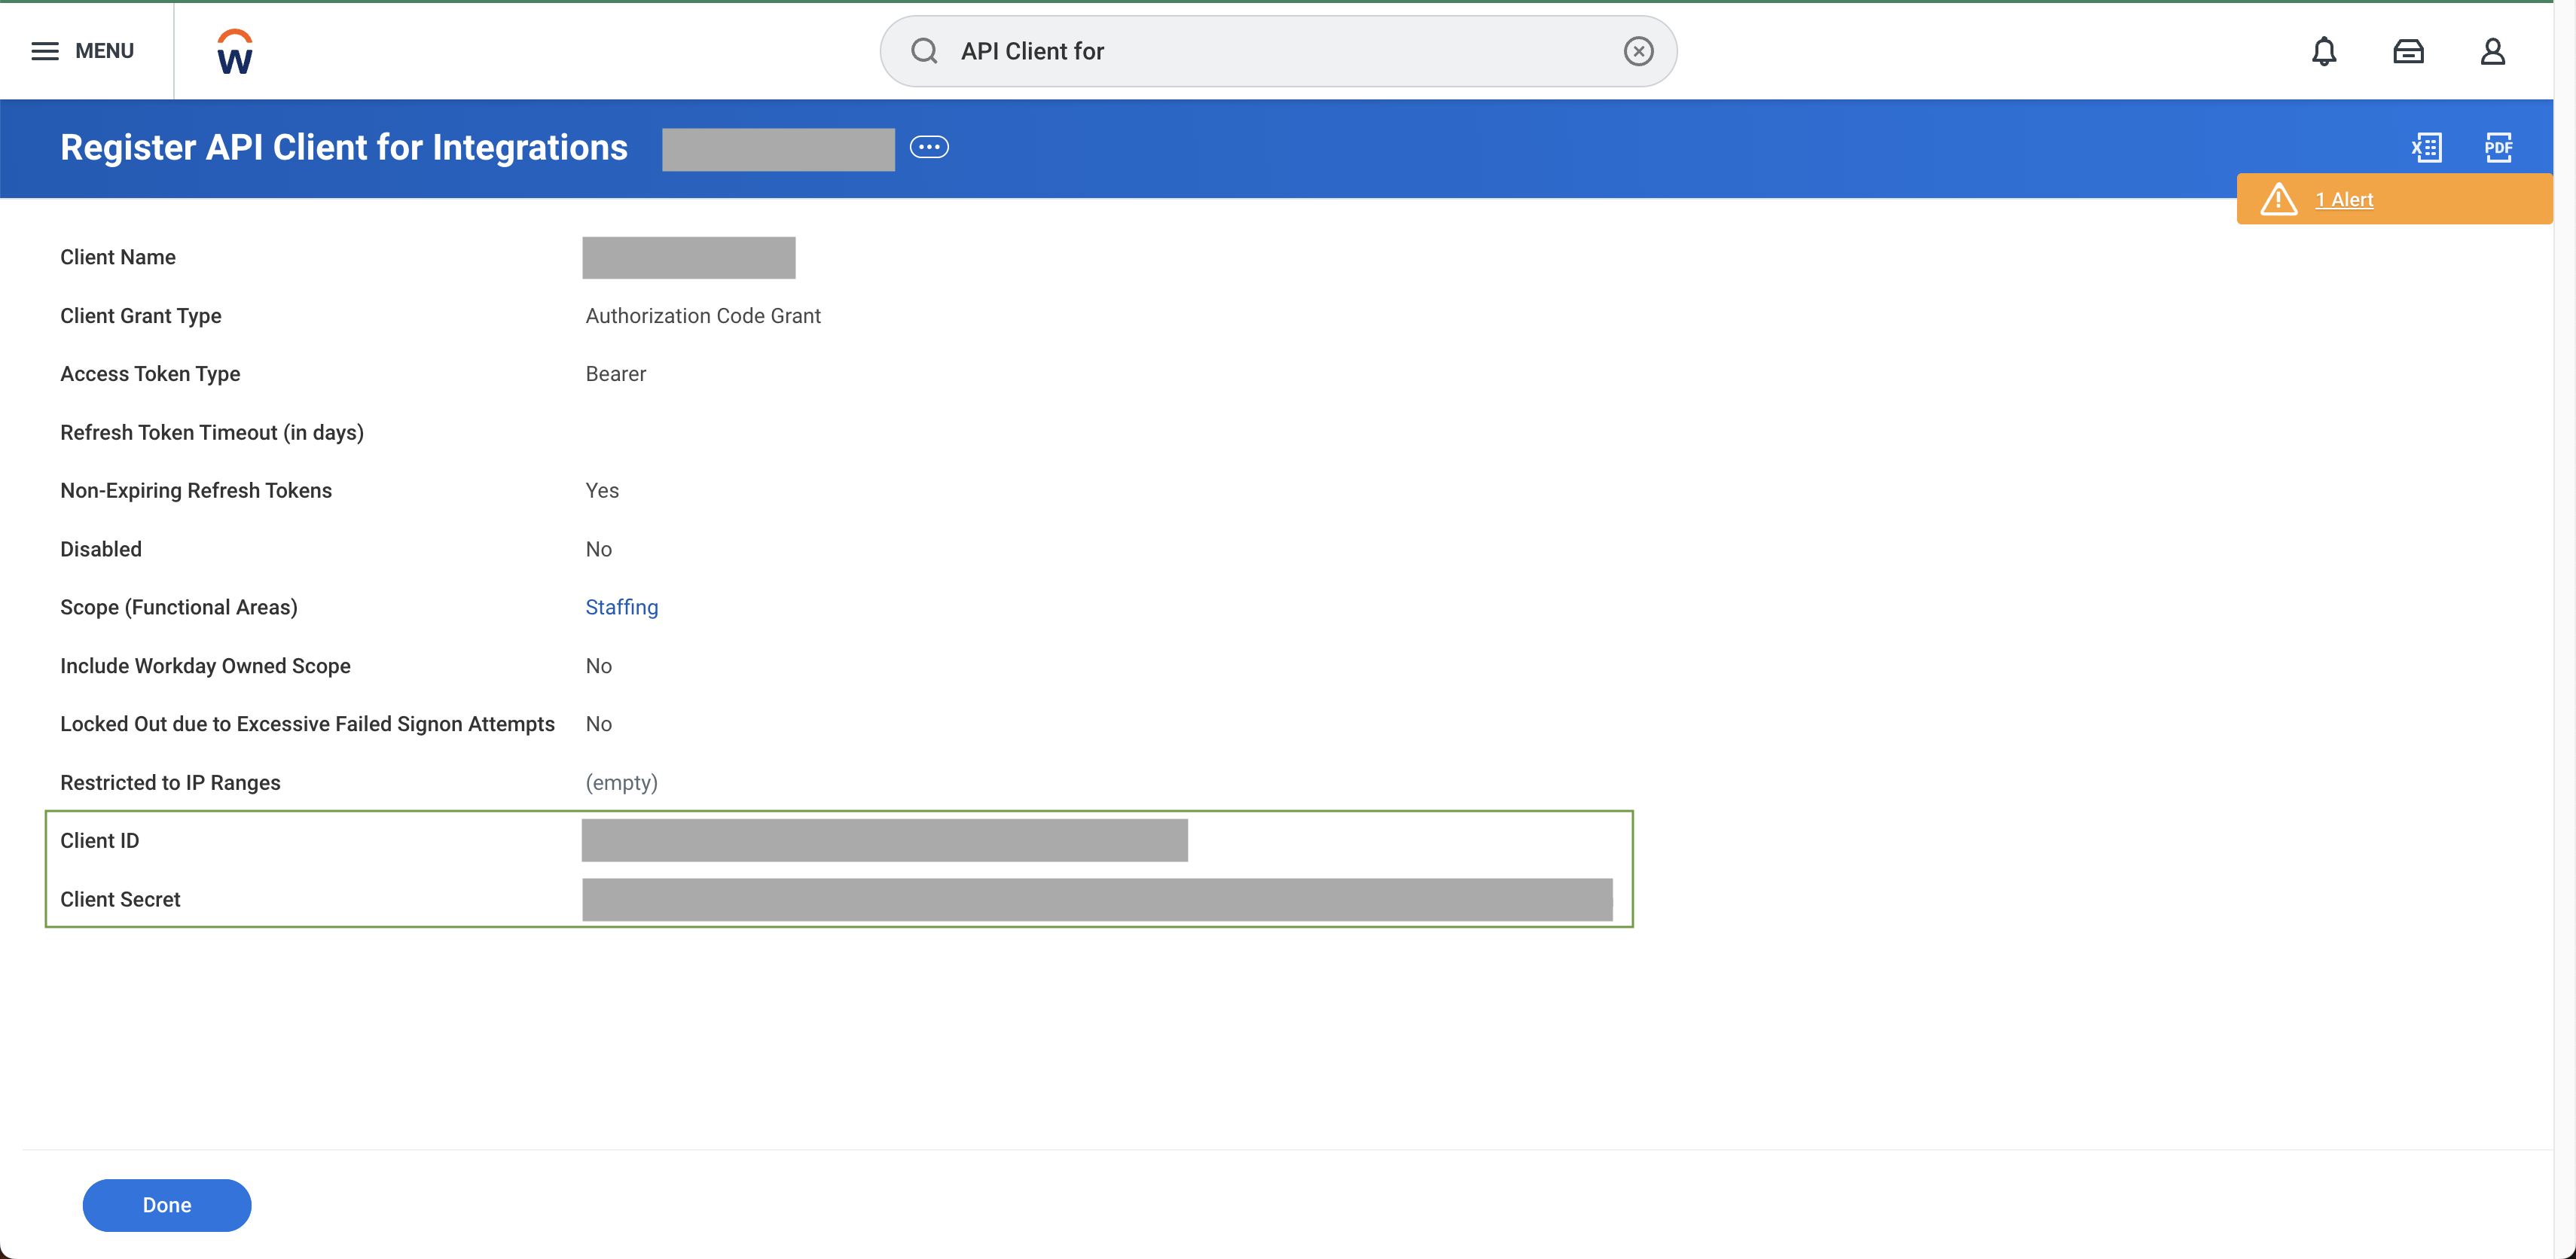
- Search for “Register API Client for Integrations” business process
- Enable non-expiring refresh tokens to ensure continuity of service
-
Under “Scope (Functional Areas)”, add exactly these scopes:
Scope (Functional Area) Needed for - Optionally, restrict the client to TechWolf’s IP ranges by filling in the “Restricted to IP Ranges” field with the values from the IP Addresses page
-
Securely store the client ID and client secret
3
Generate Refresh Token
- Search for “View API Clients” report
- Click “API Clients for Integrations” tab
- Note down the token endpoint. You will need to share this later.
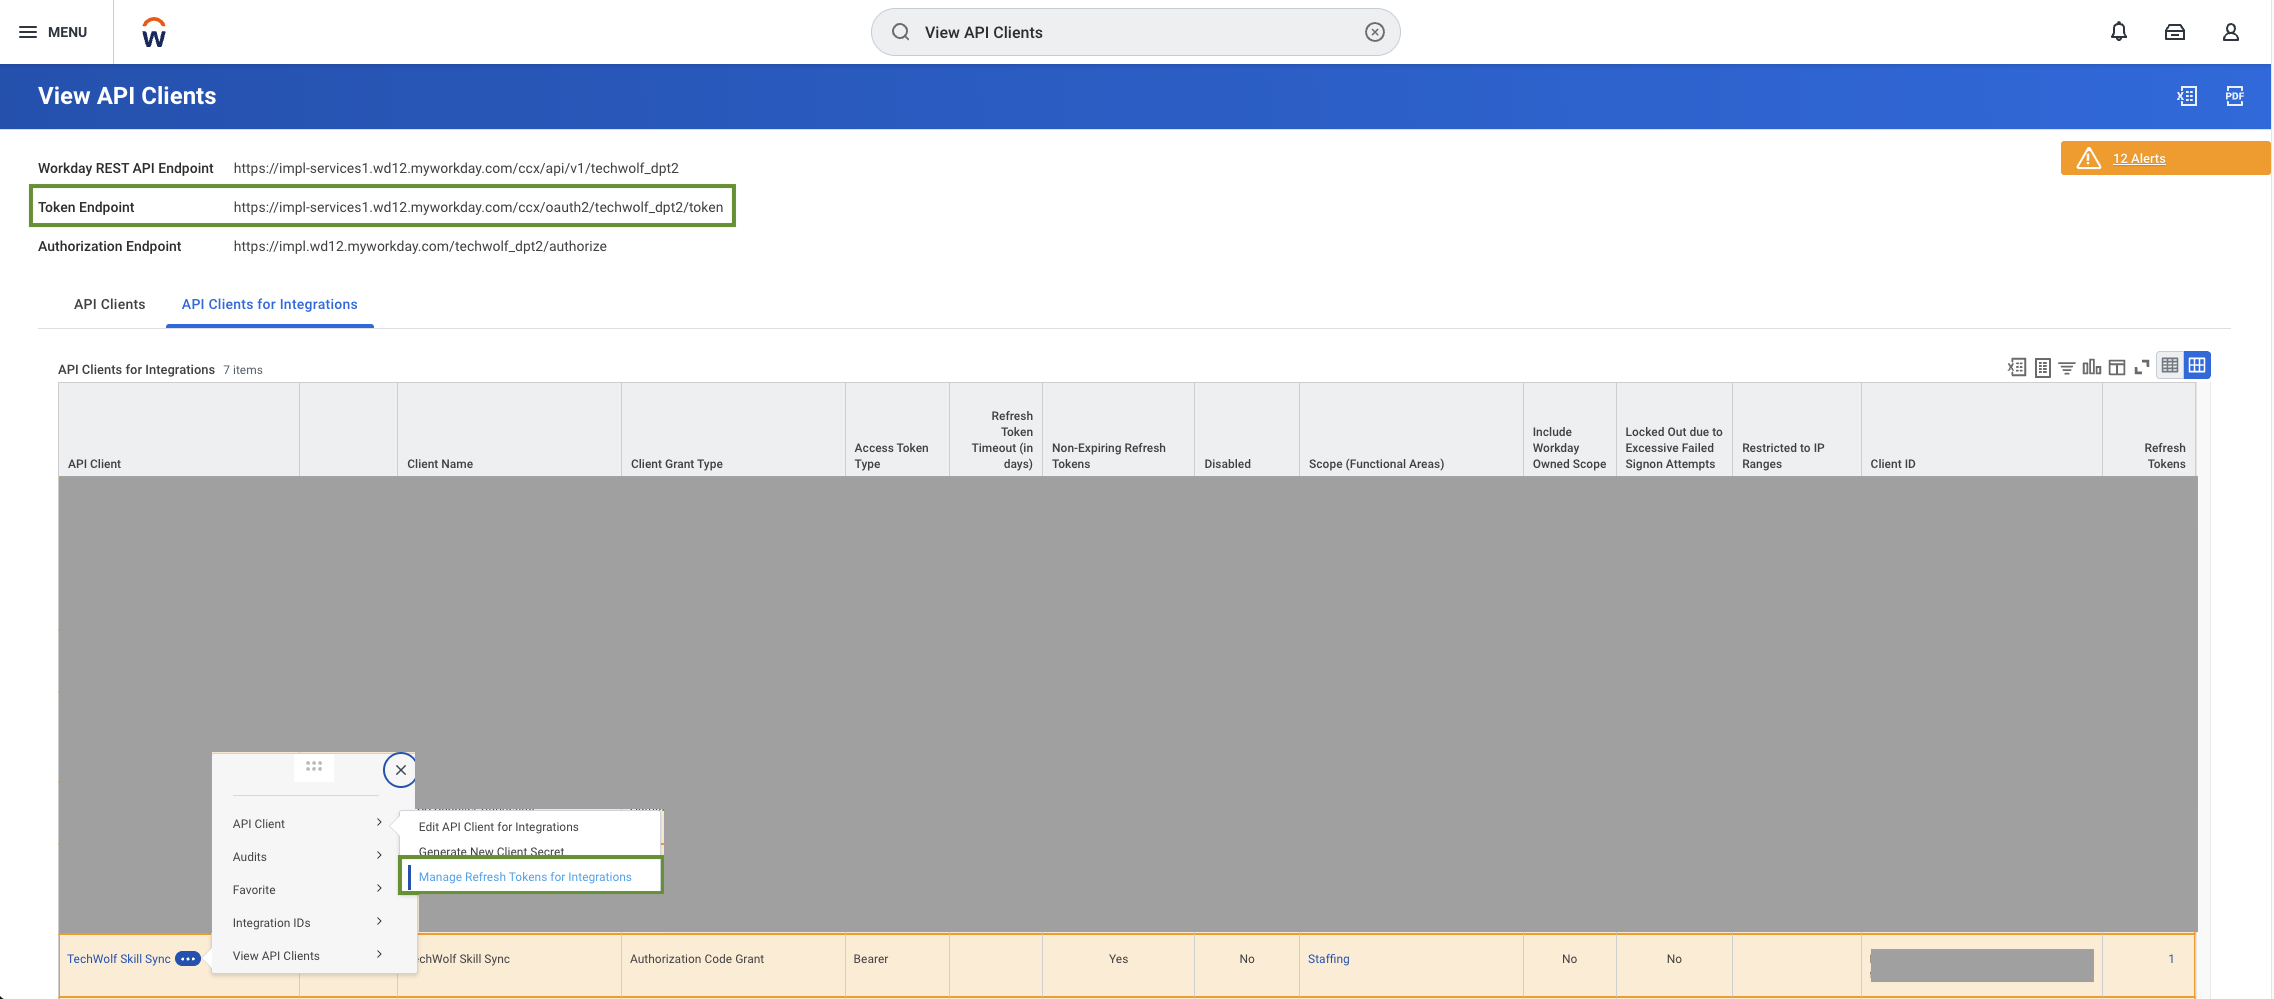
- Find your API client and select “Manage Refresh Tokens for Integrations”
- Under “Workday Account”, type in your ISU
- Press OK
- Check the box “Generate new refresh token”
- Press OK
- Securely store the refresh token.
OAuth: WCP gateway setup
The gateway uses the ISU and the domain security policies from the General setup. What you need- An administrator on the Developer Site, to create the API client.
- A Company Administrator, to authorize a non-development tenant.
- A Workday security administrator, to map the API client to the ISU.
- Your company’s Workday Named Support Contact, only if the tenant is not listed for Workday Extend.
1
Check that the tenant is listed
On the Workday Developer Site, open Console → Tenants.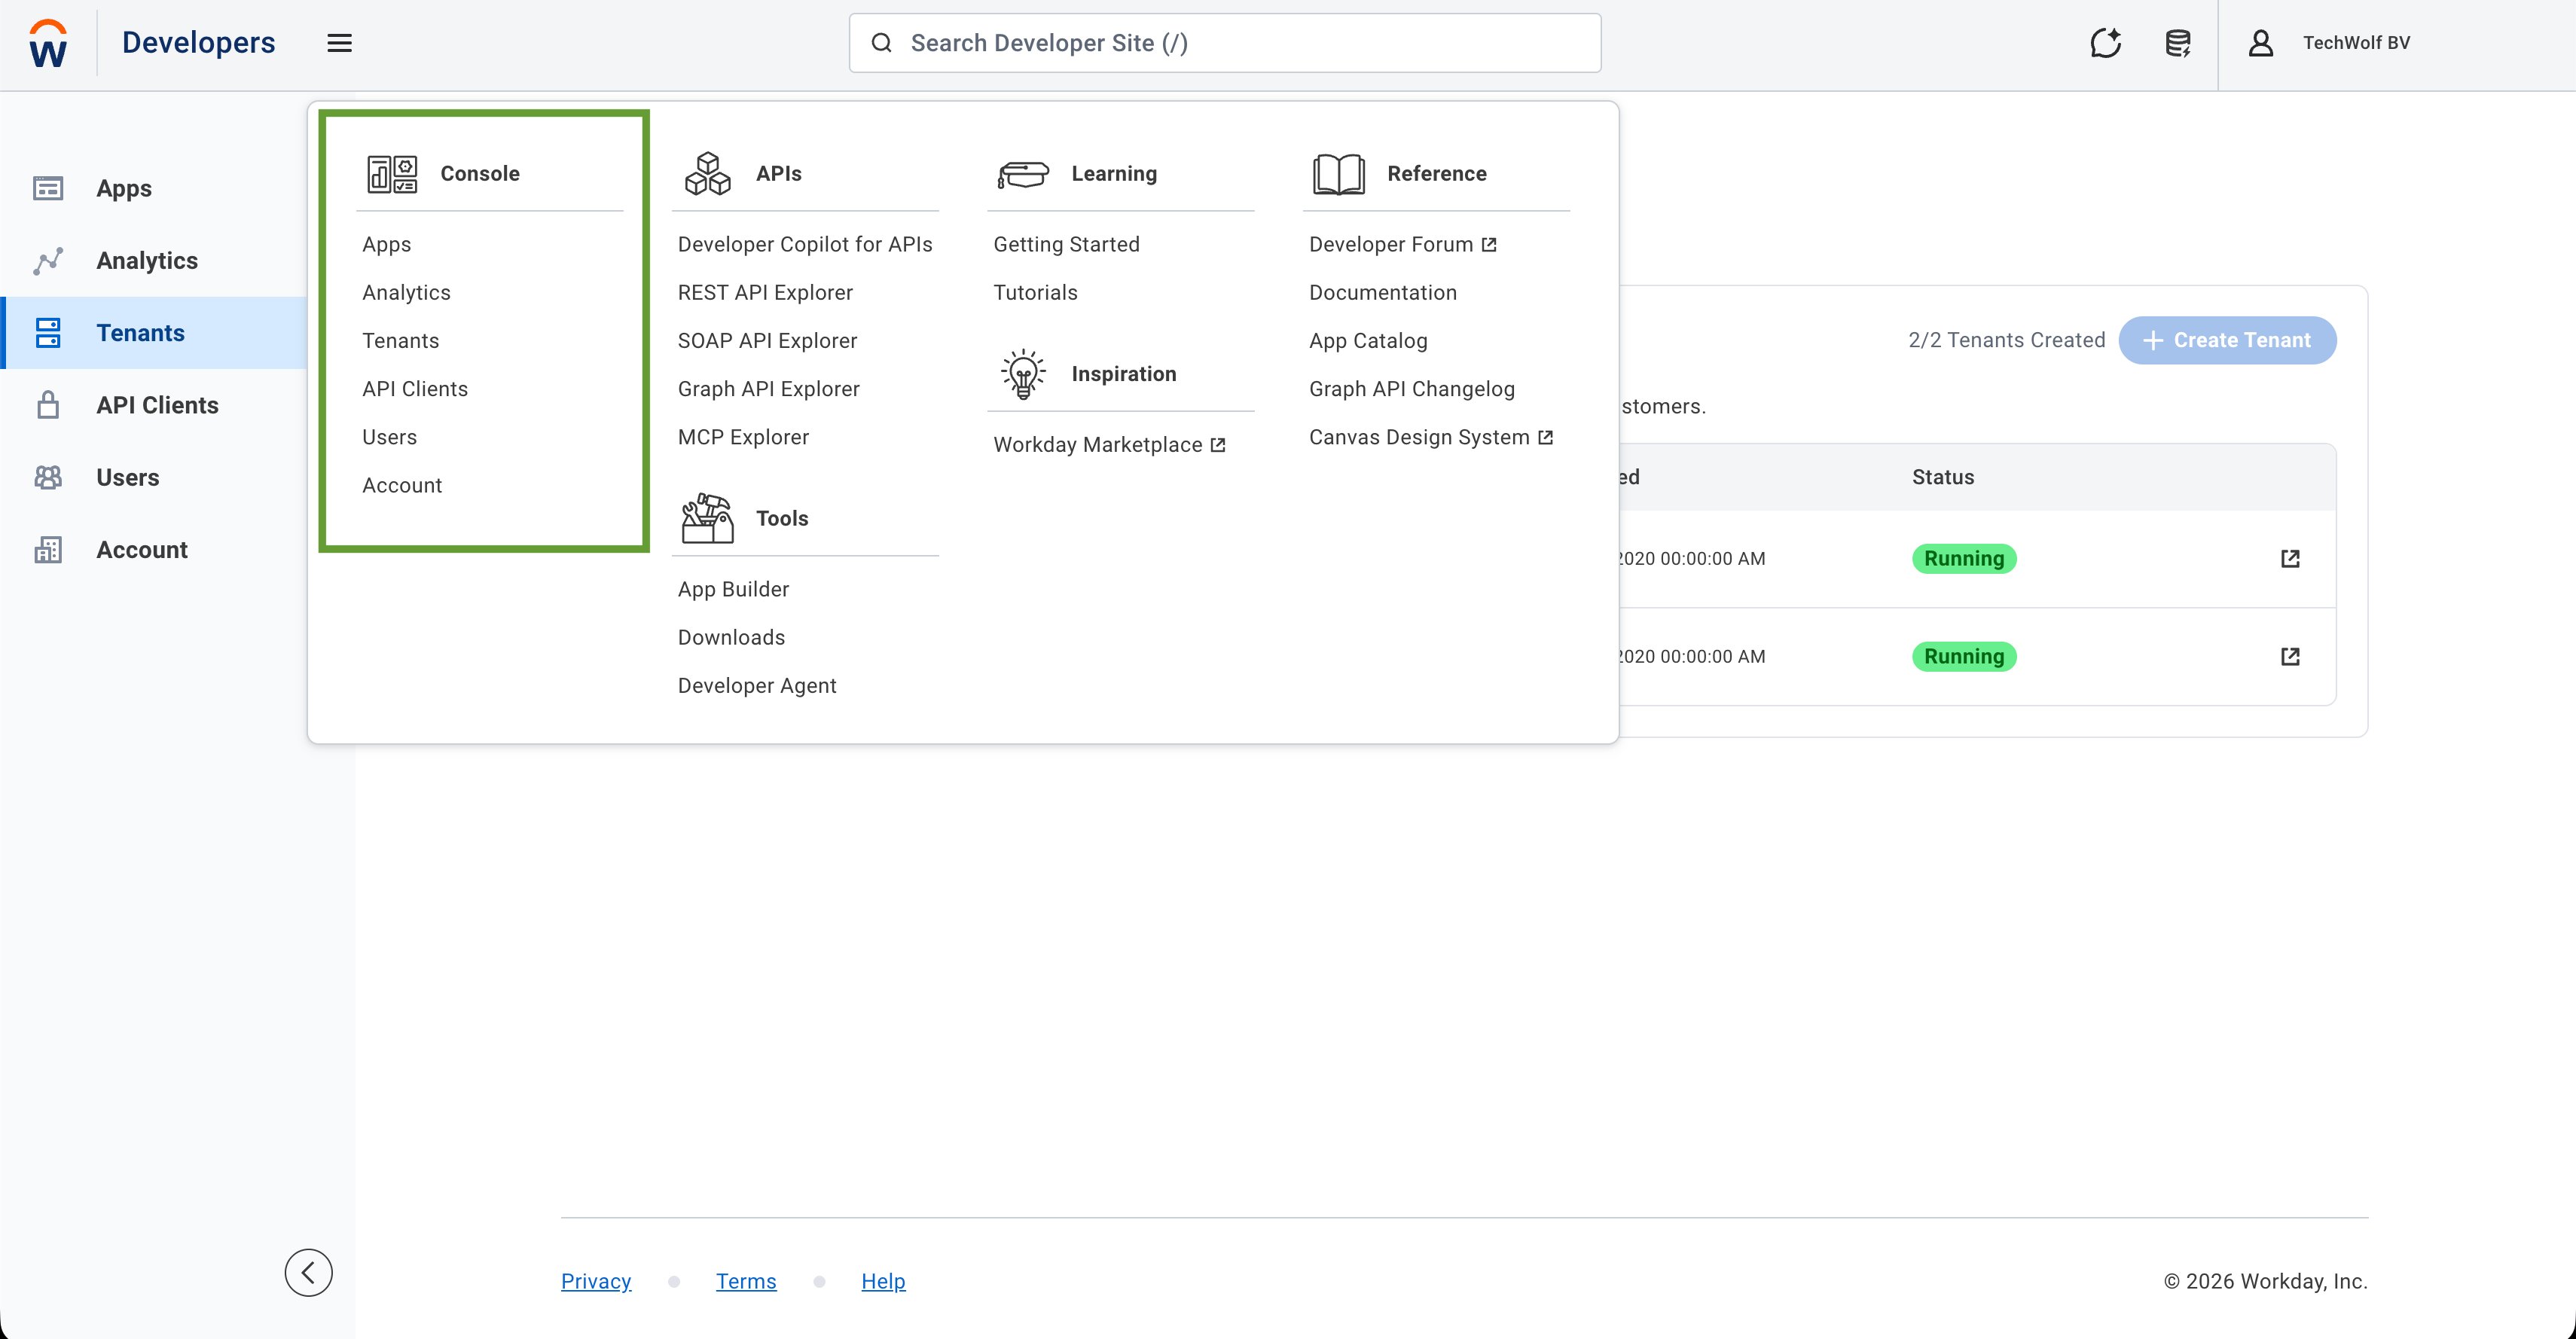
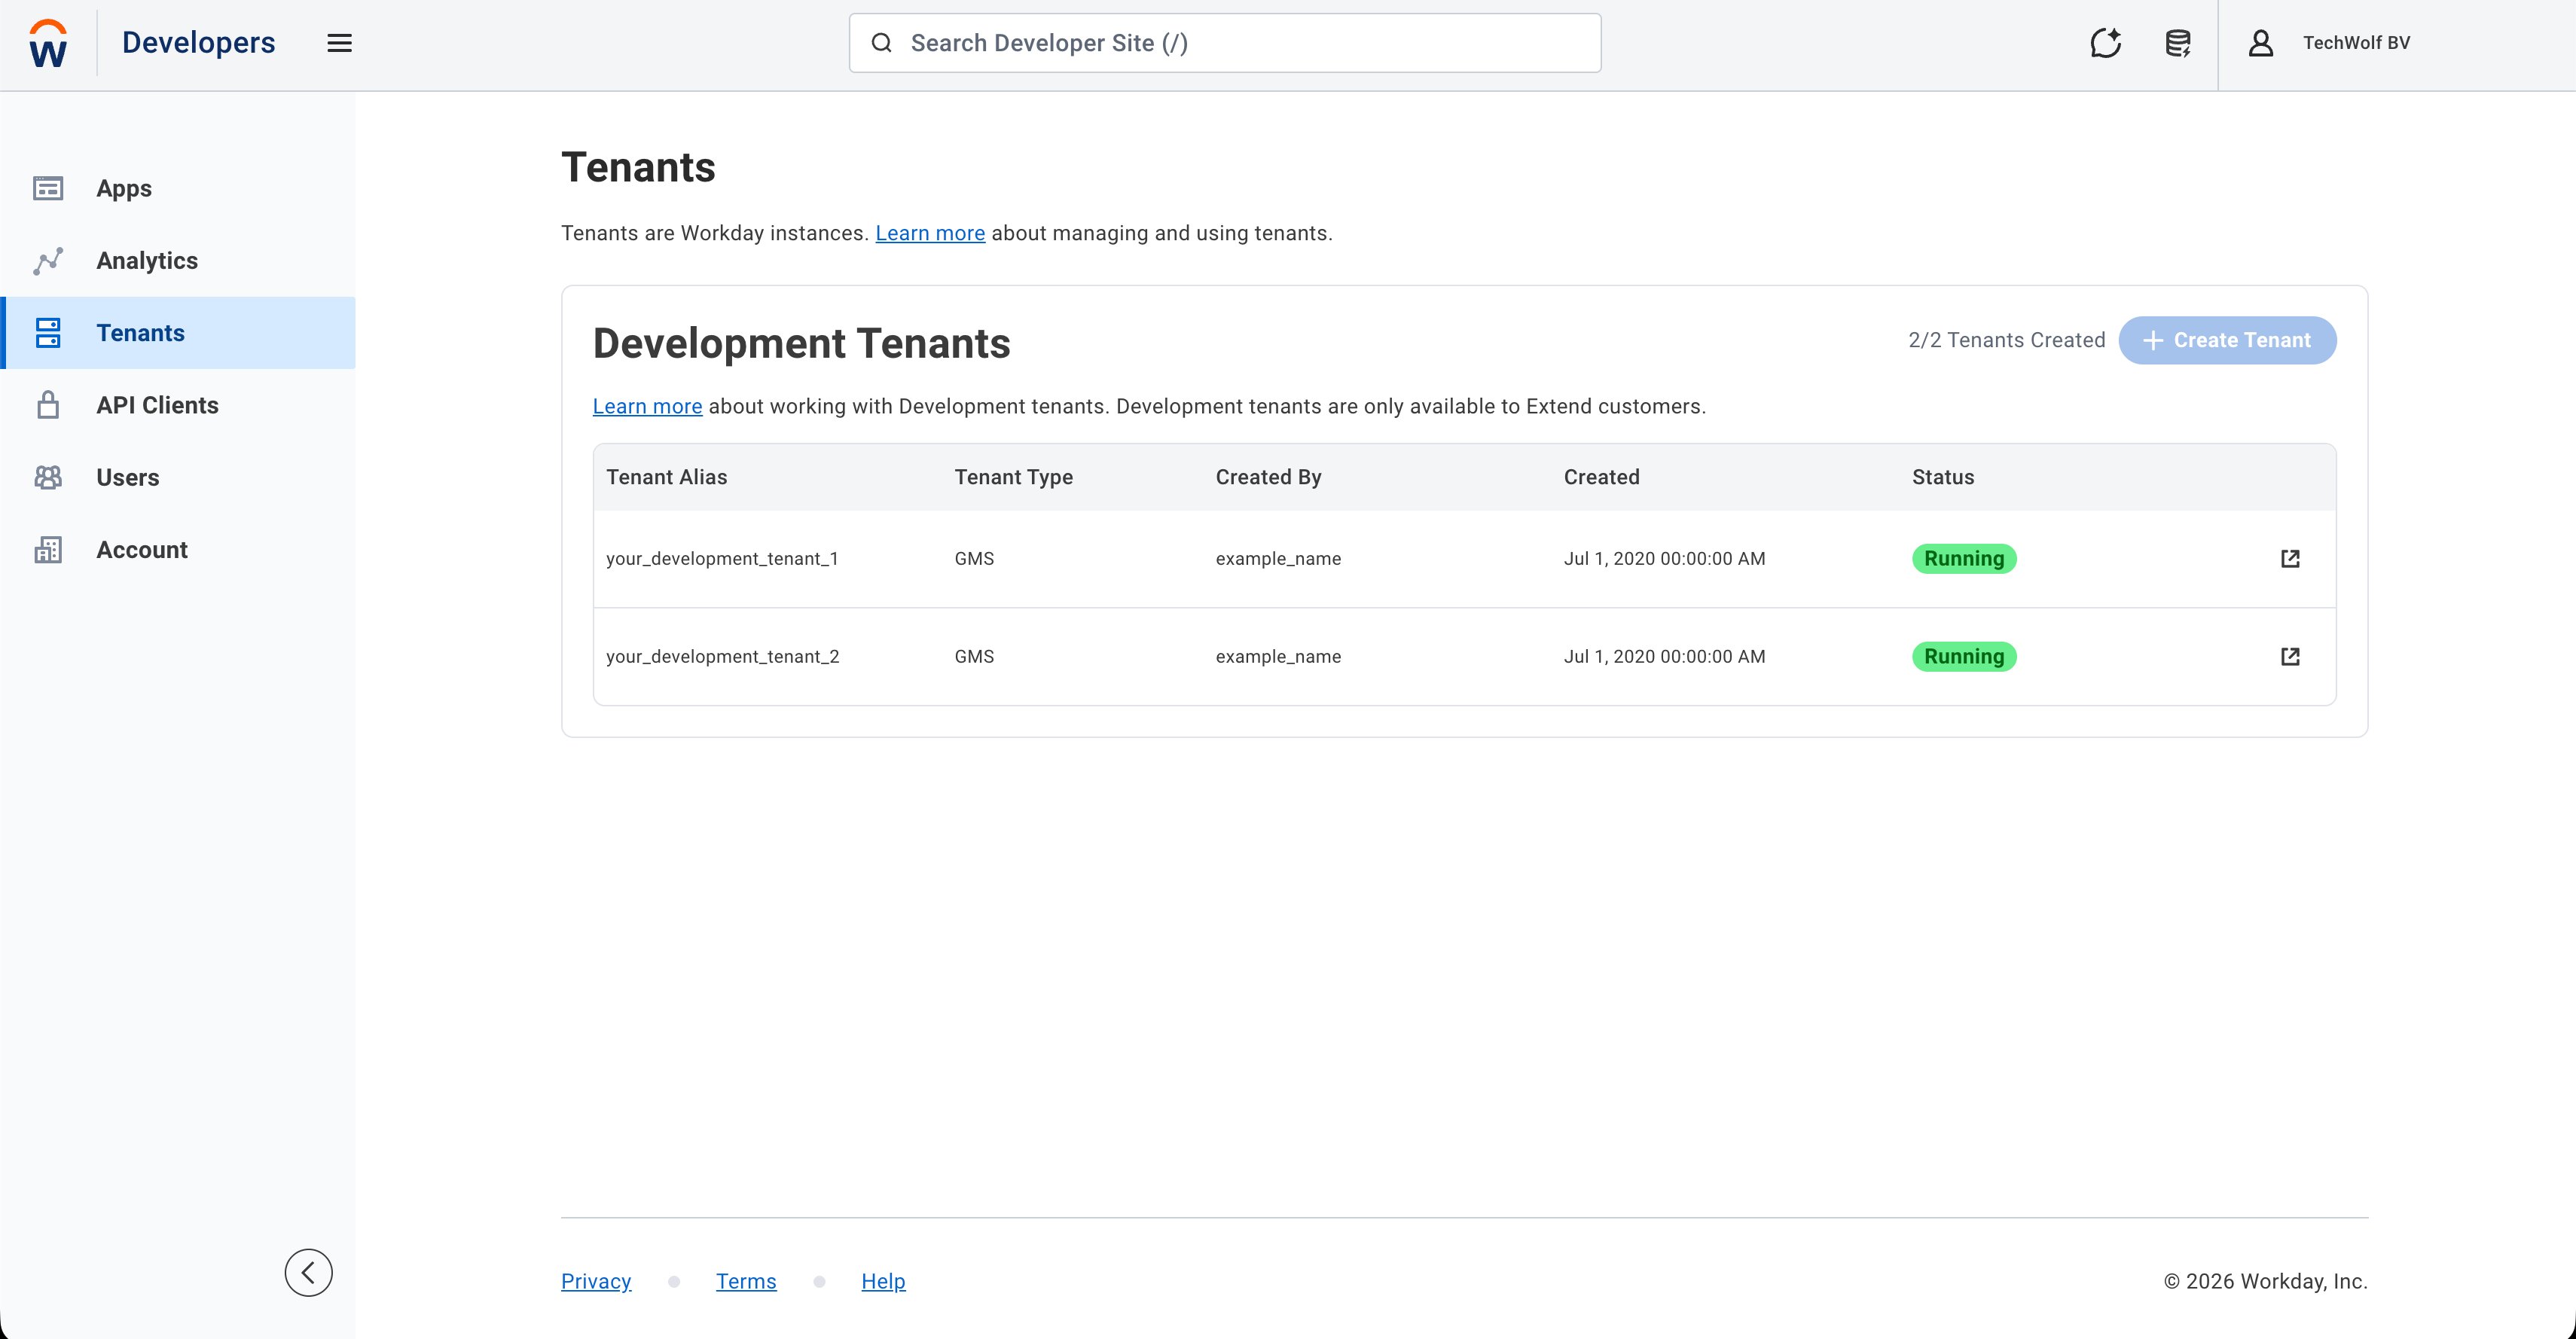
Manage Workday Cloud Platform task, once per
tenant.
See
Enable Non-Development Tenants for Workday Extend.2
Create the API client
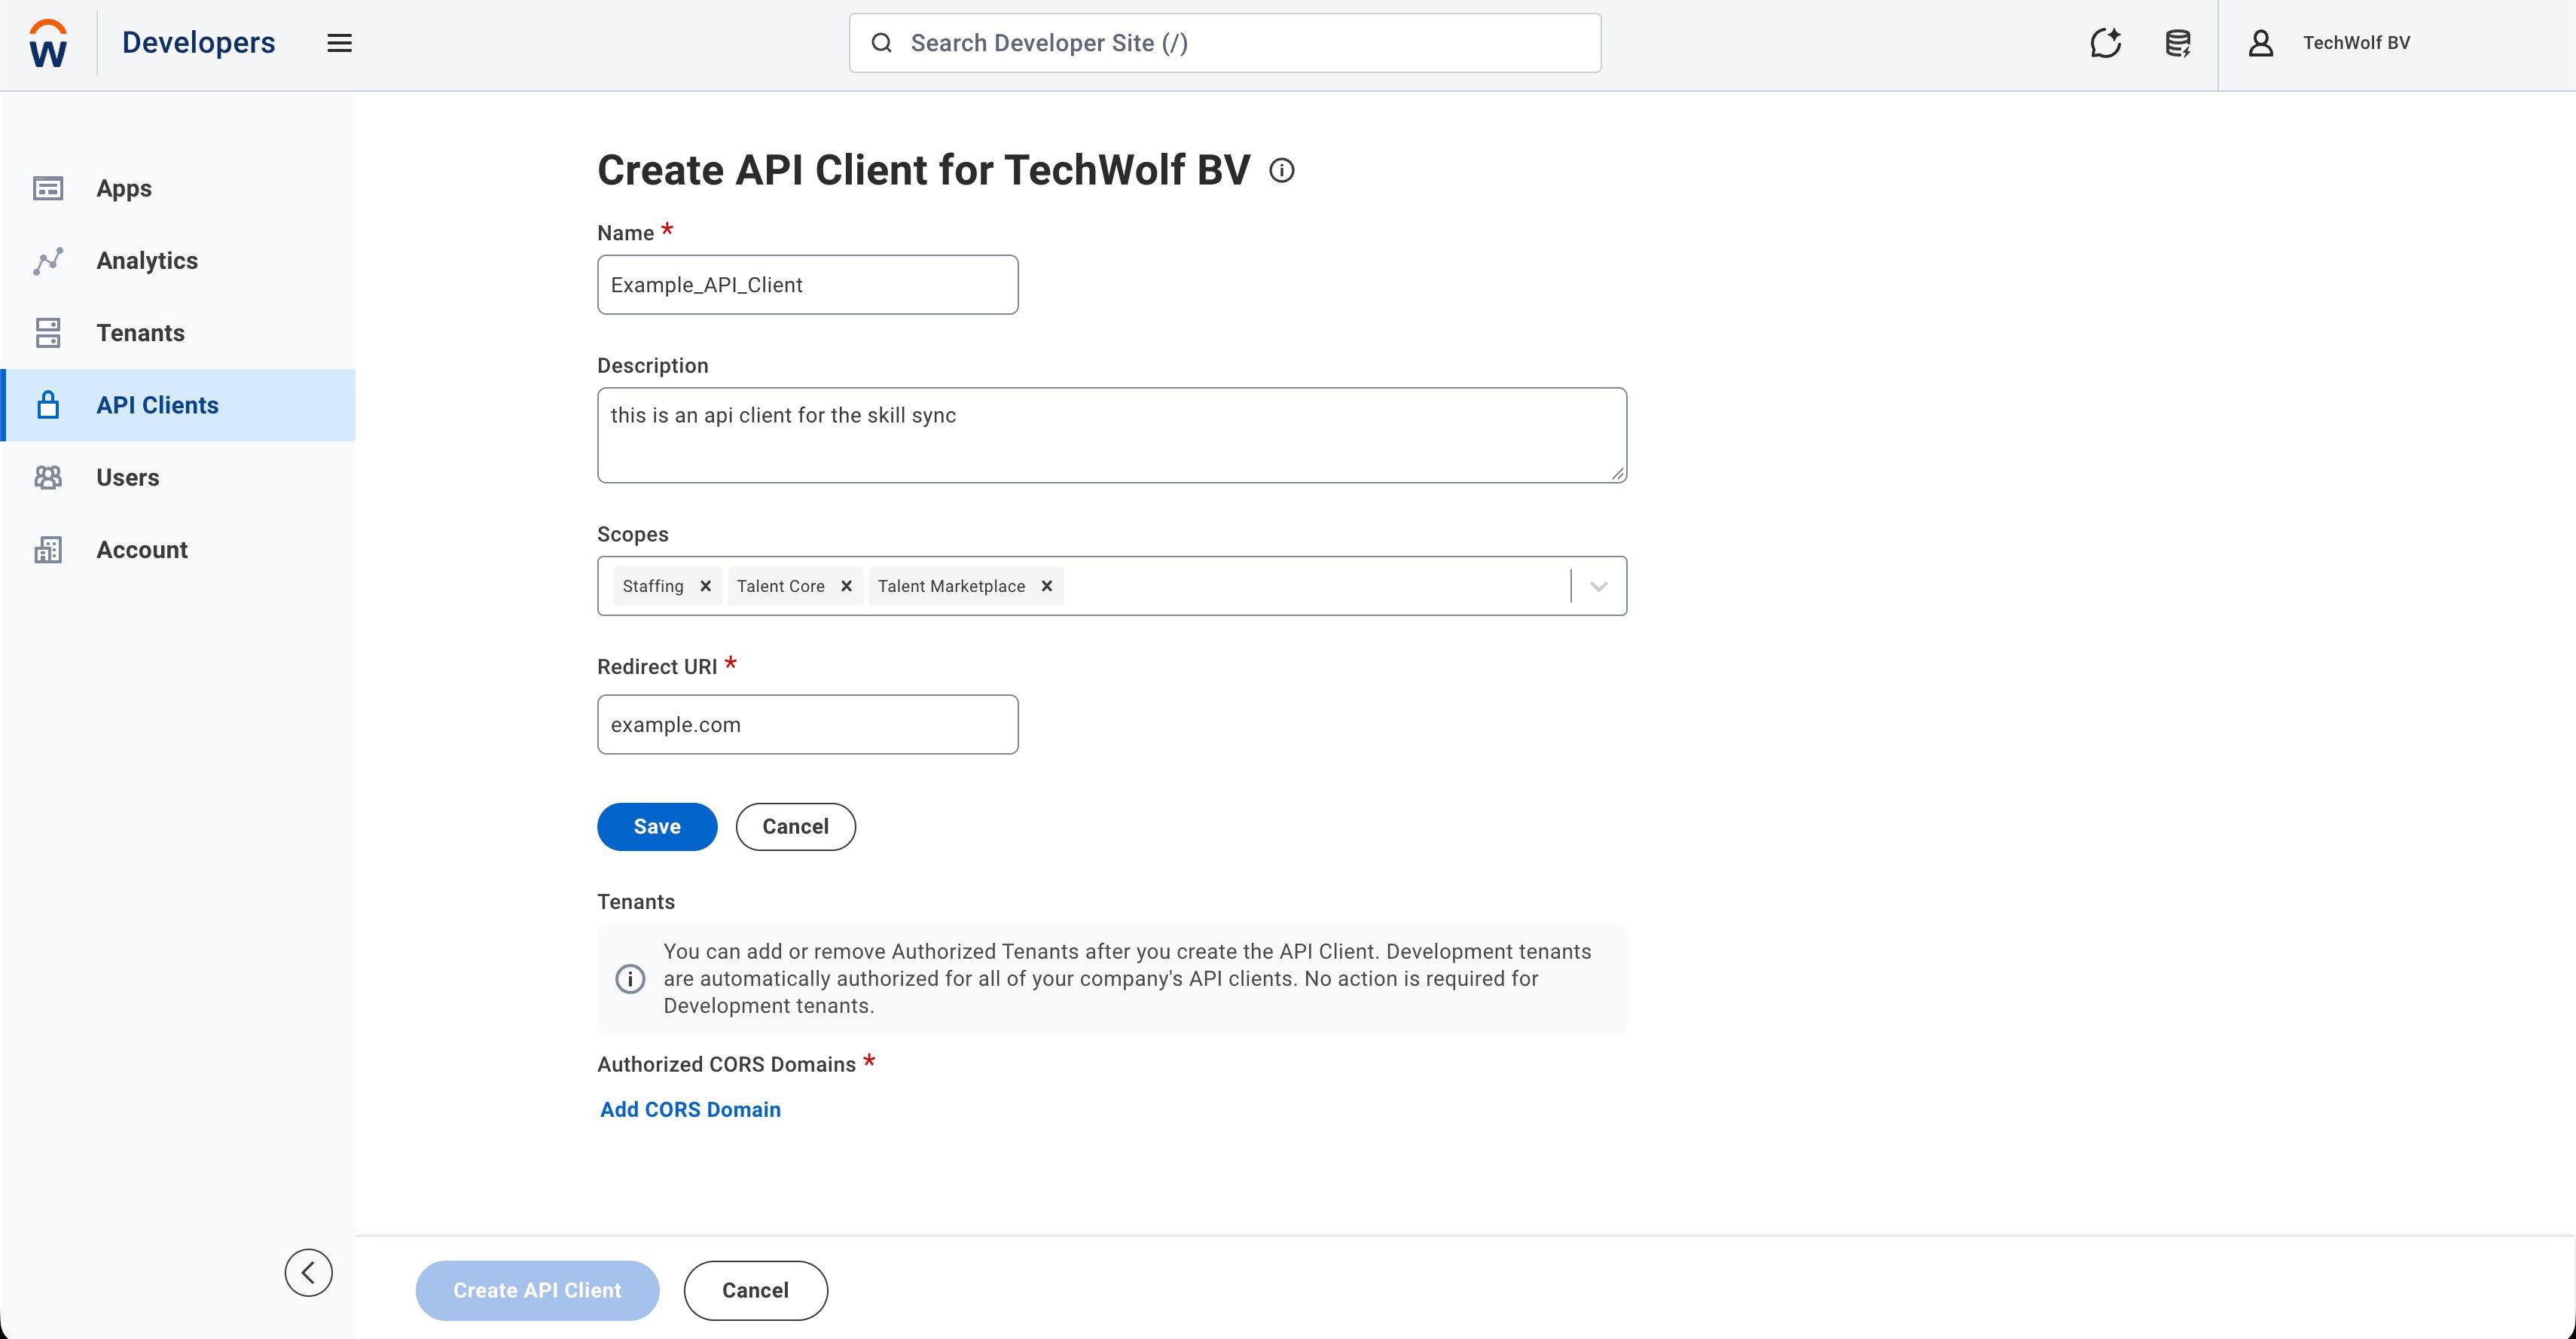
- On the Developer Site, open Console → API Clients → Create API Client.
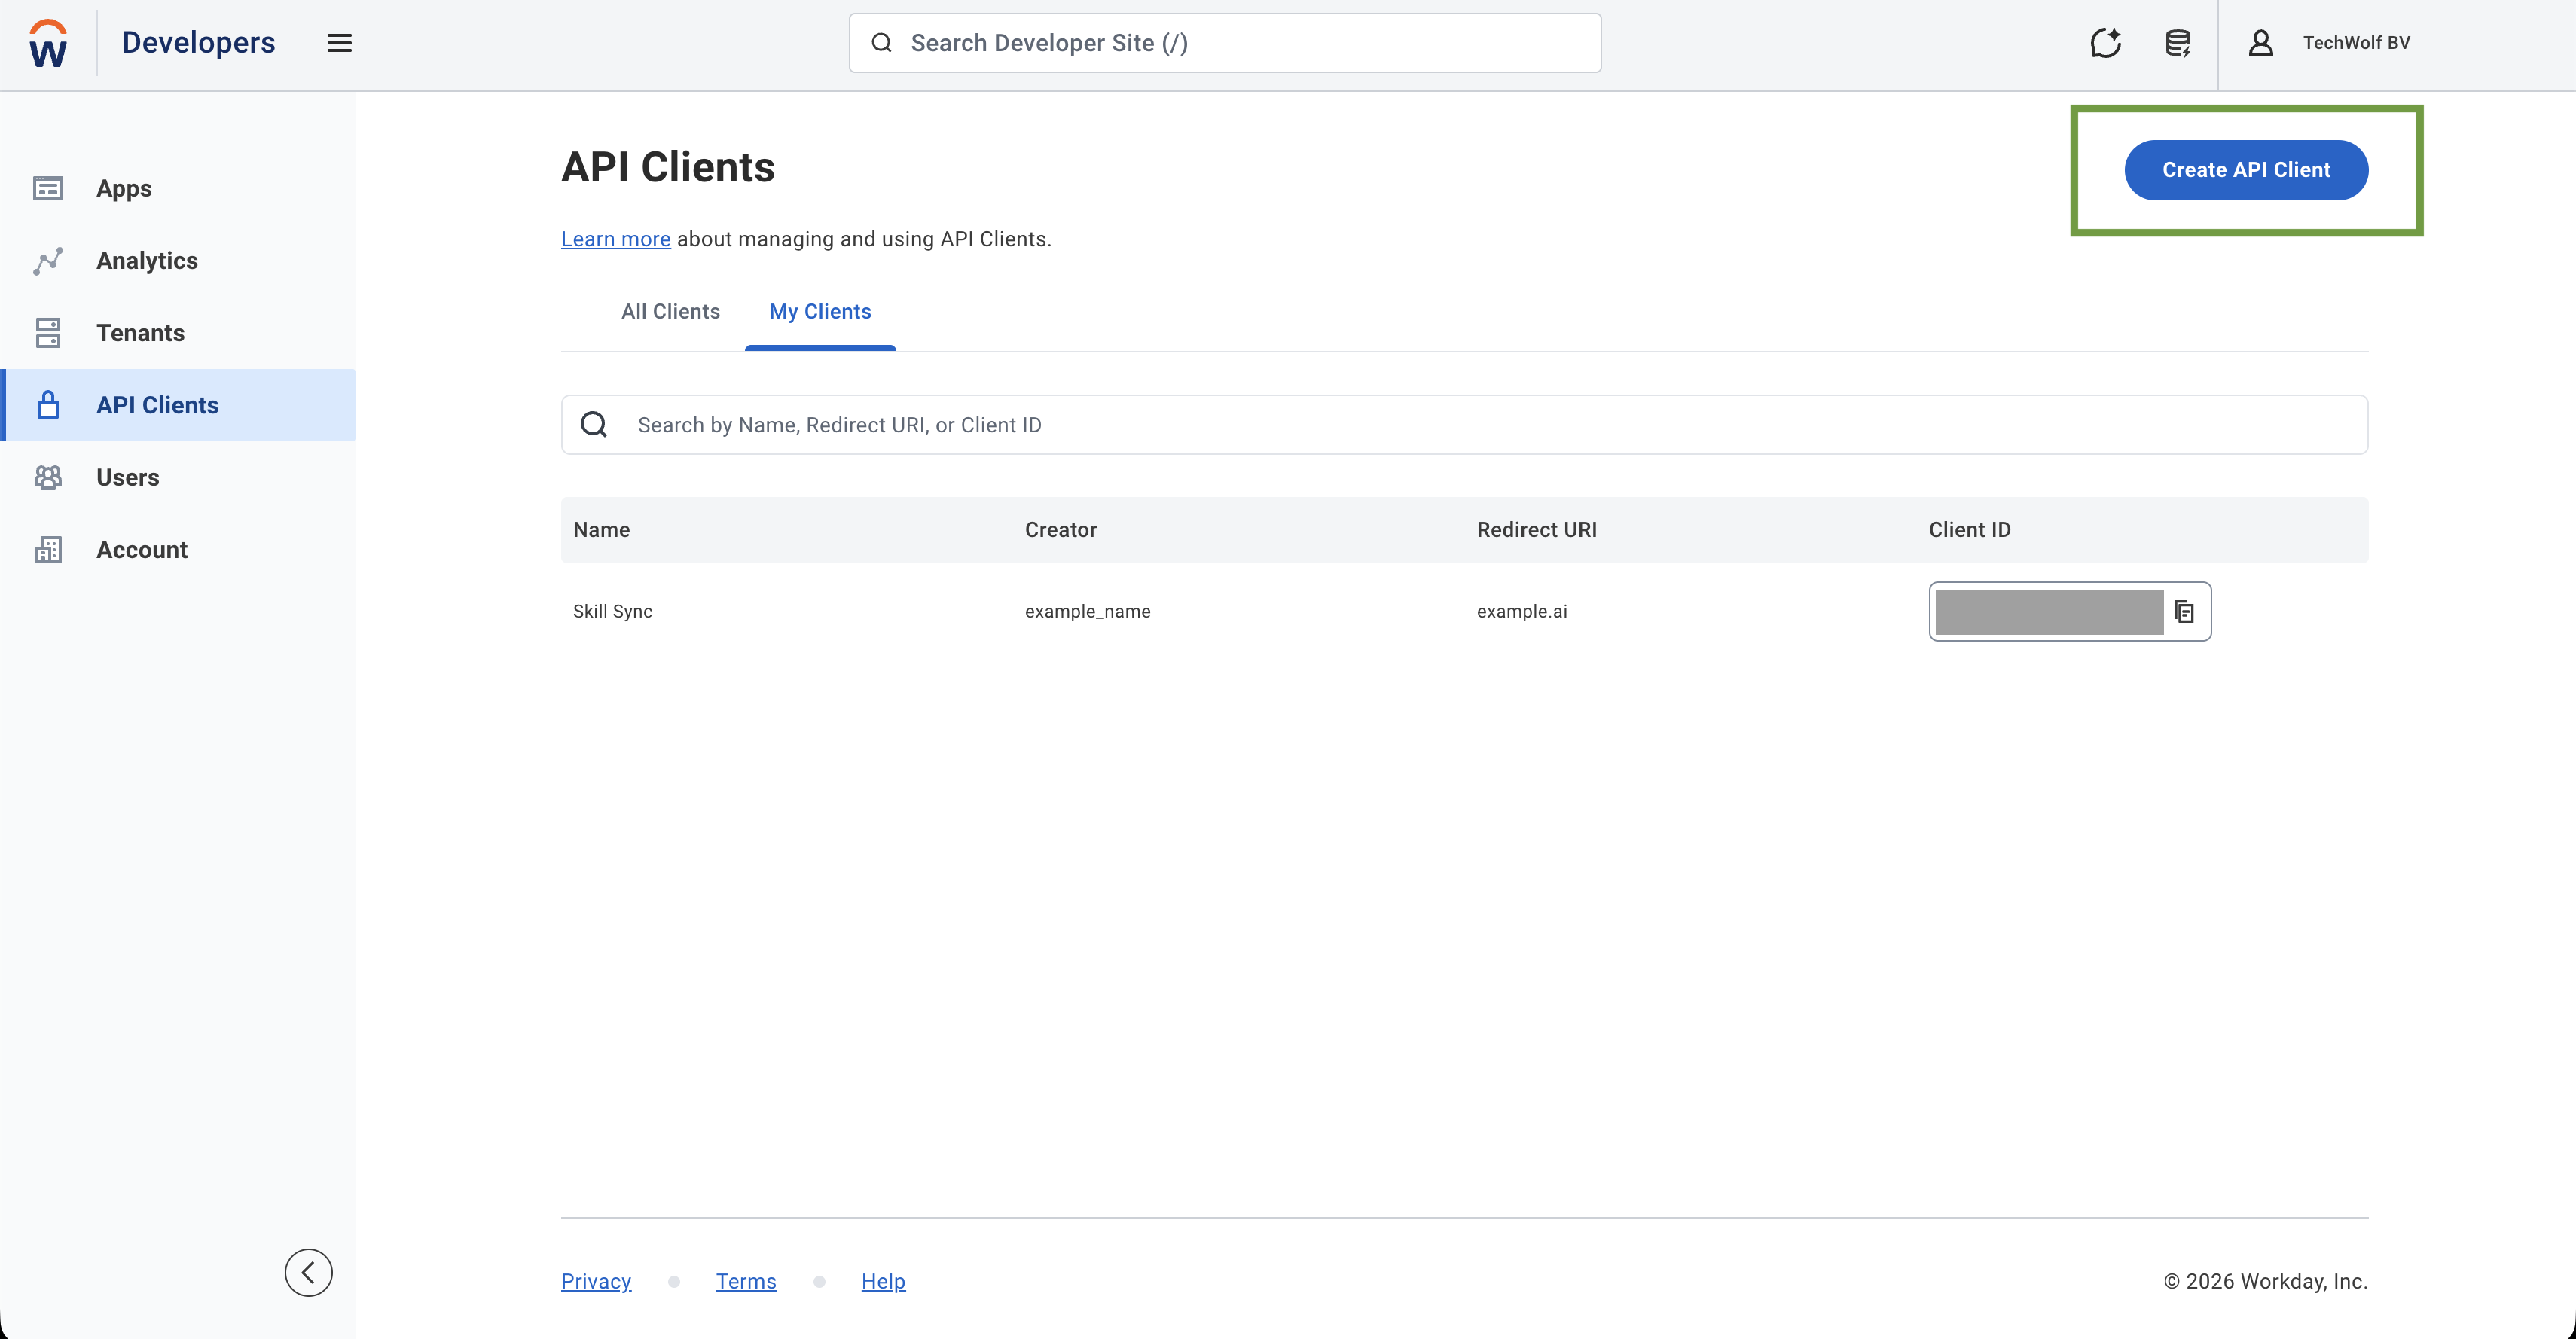
- Select the scopes Staffing, Talent Core and Talent Marketplace.
- Redirect URI and CORS are required, but this flow uses neither. Any value
works, such as your company’s own domain.
- The client secret is shown once, when the client is created. Store it
securely then. If it is lost,
Generate New Client Secreton the client creates a new one and retires the old one.
3
Authorize a non-development tenant
Only a Company Administrator can do this. Development tenants are authorized
automatically and skip this step.
- On the API client, select
Modify Authorized Tenants.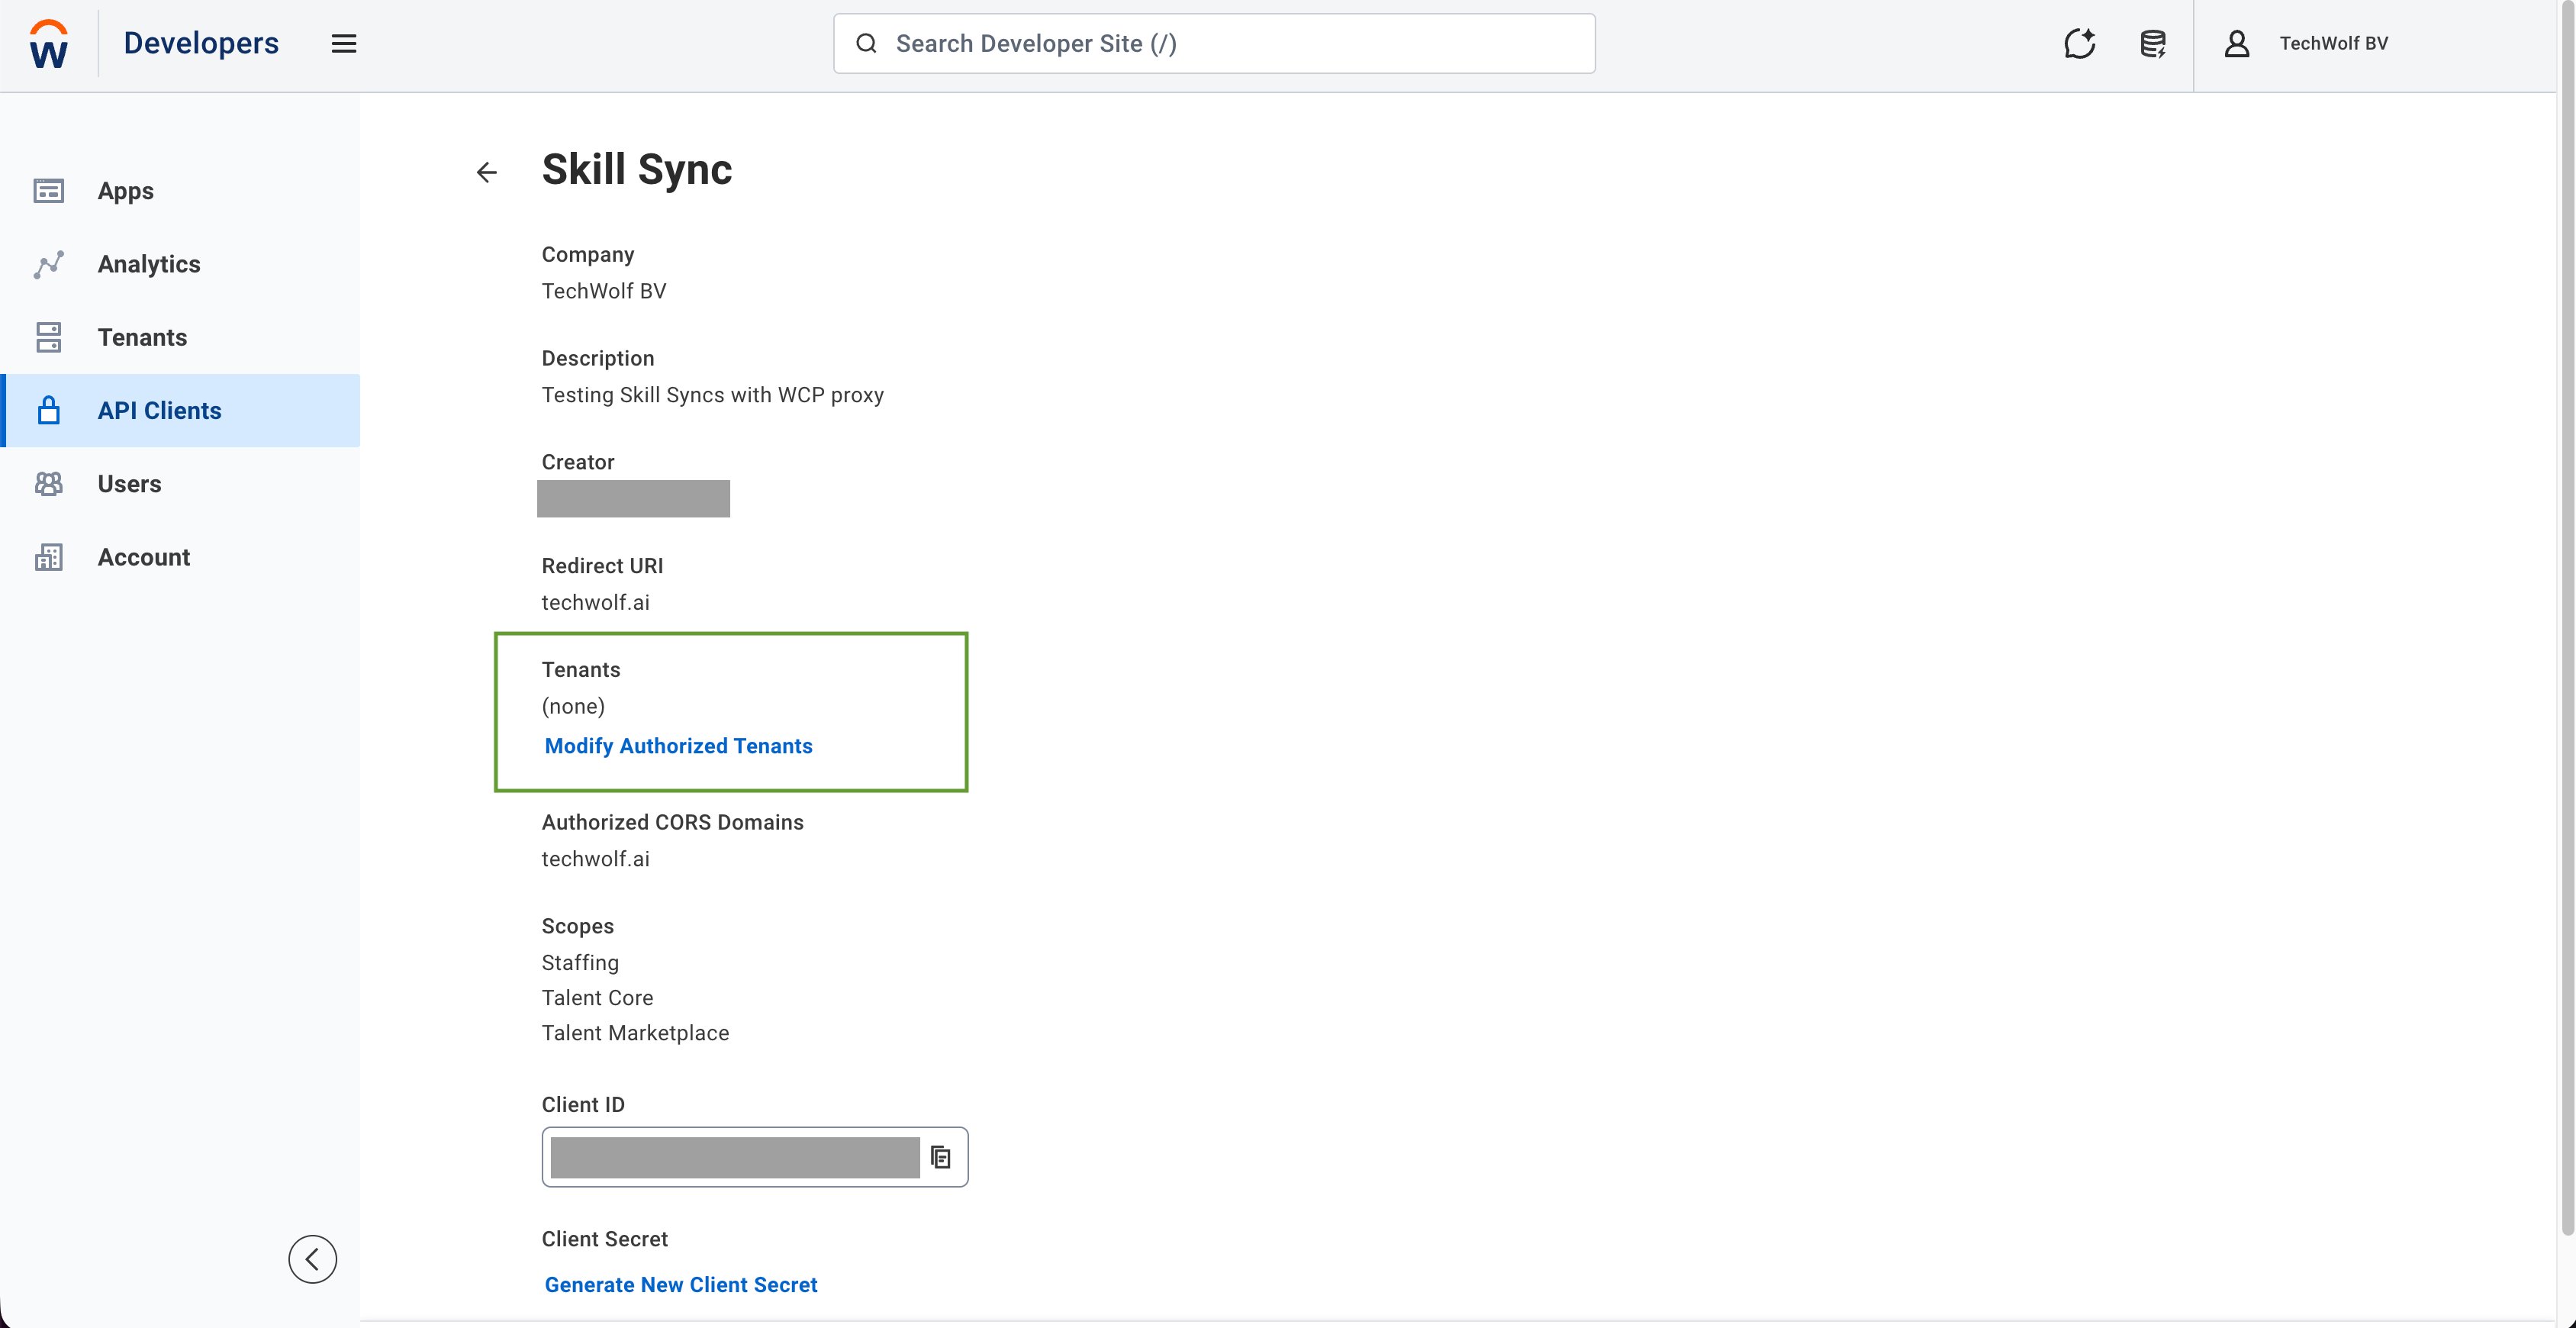
- Pick the tenant from the list and select
Save Changes.
4
Find the tenant alias
The Tenants page from the first step shows the alias in the Tenant Alias column.
For a production, implementation or sandbox preview tenant, the alias is the
tenant name. For a sandbox tenant, it is the tenant name followed by
-sb.5
Find the region
Open the account menu at the top right of the Developer Site. The entry of your
company shows its region.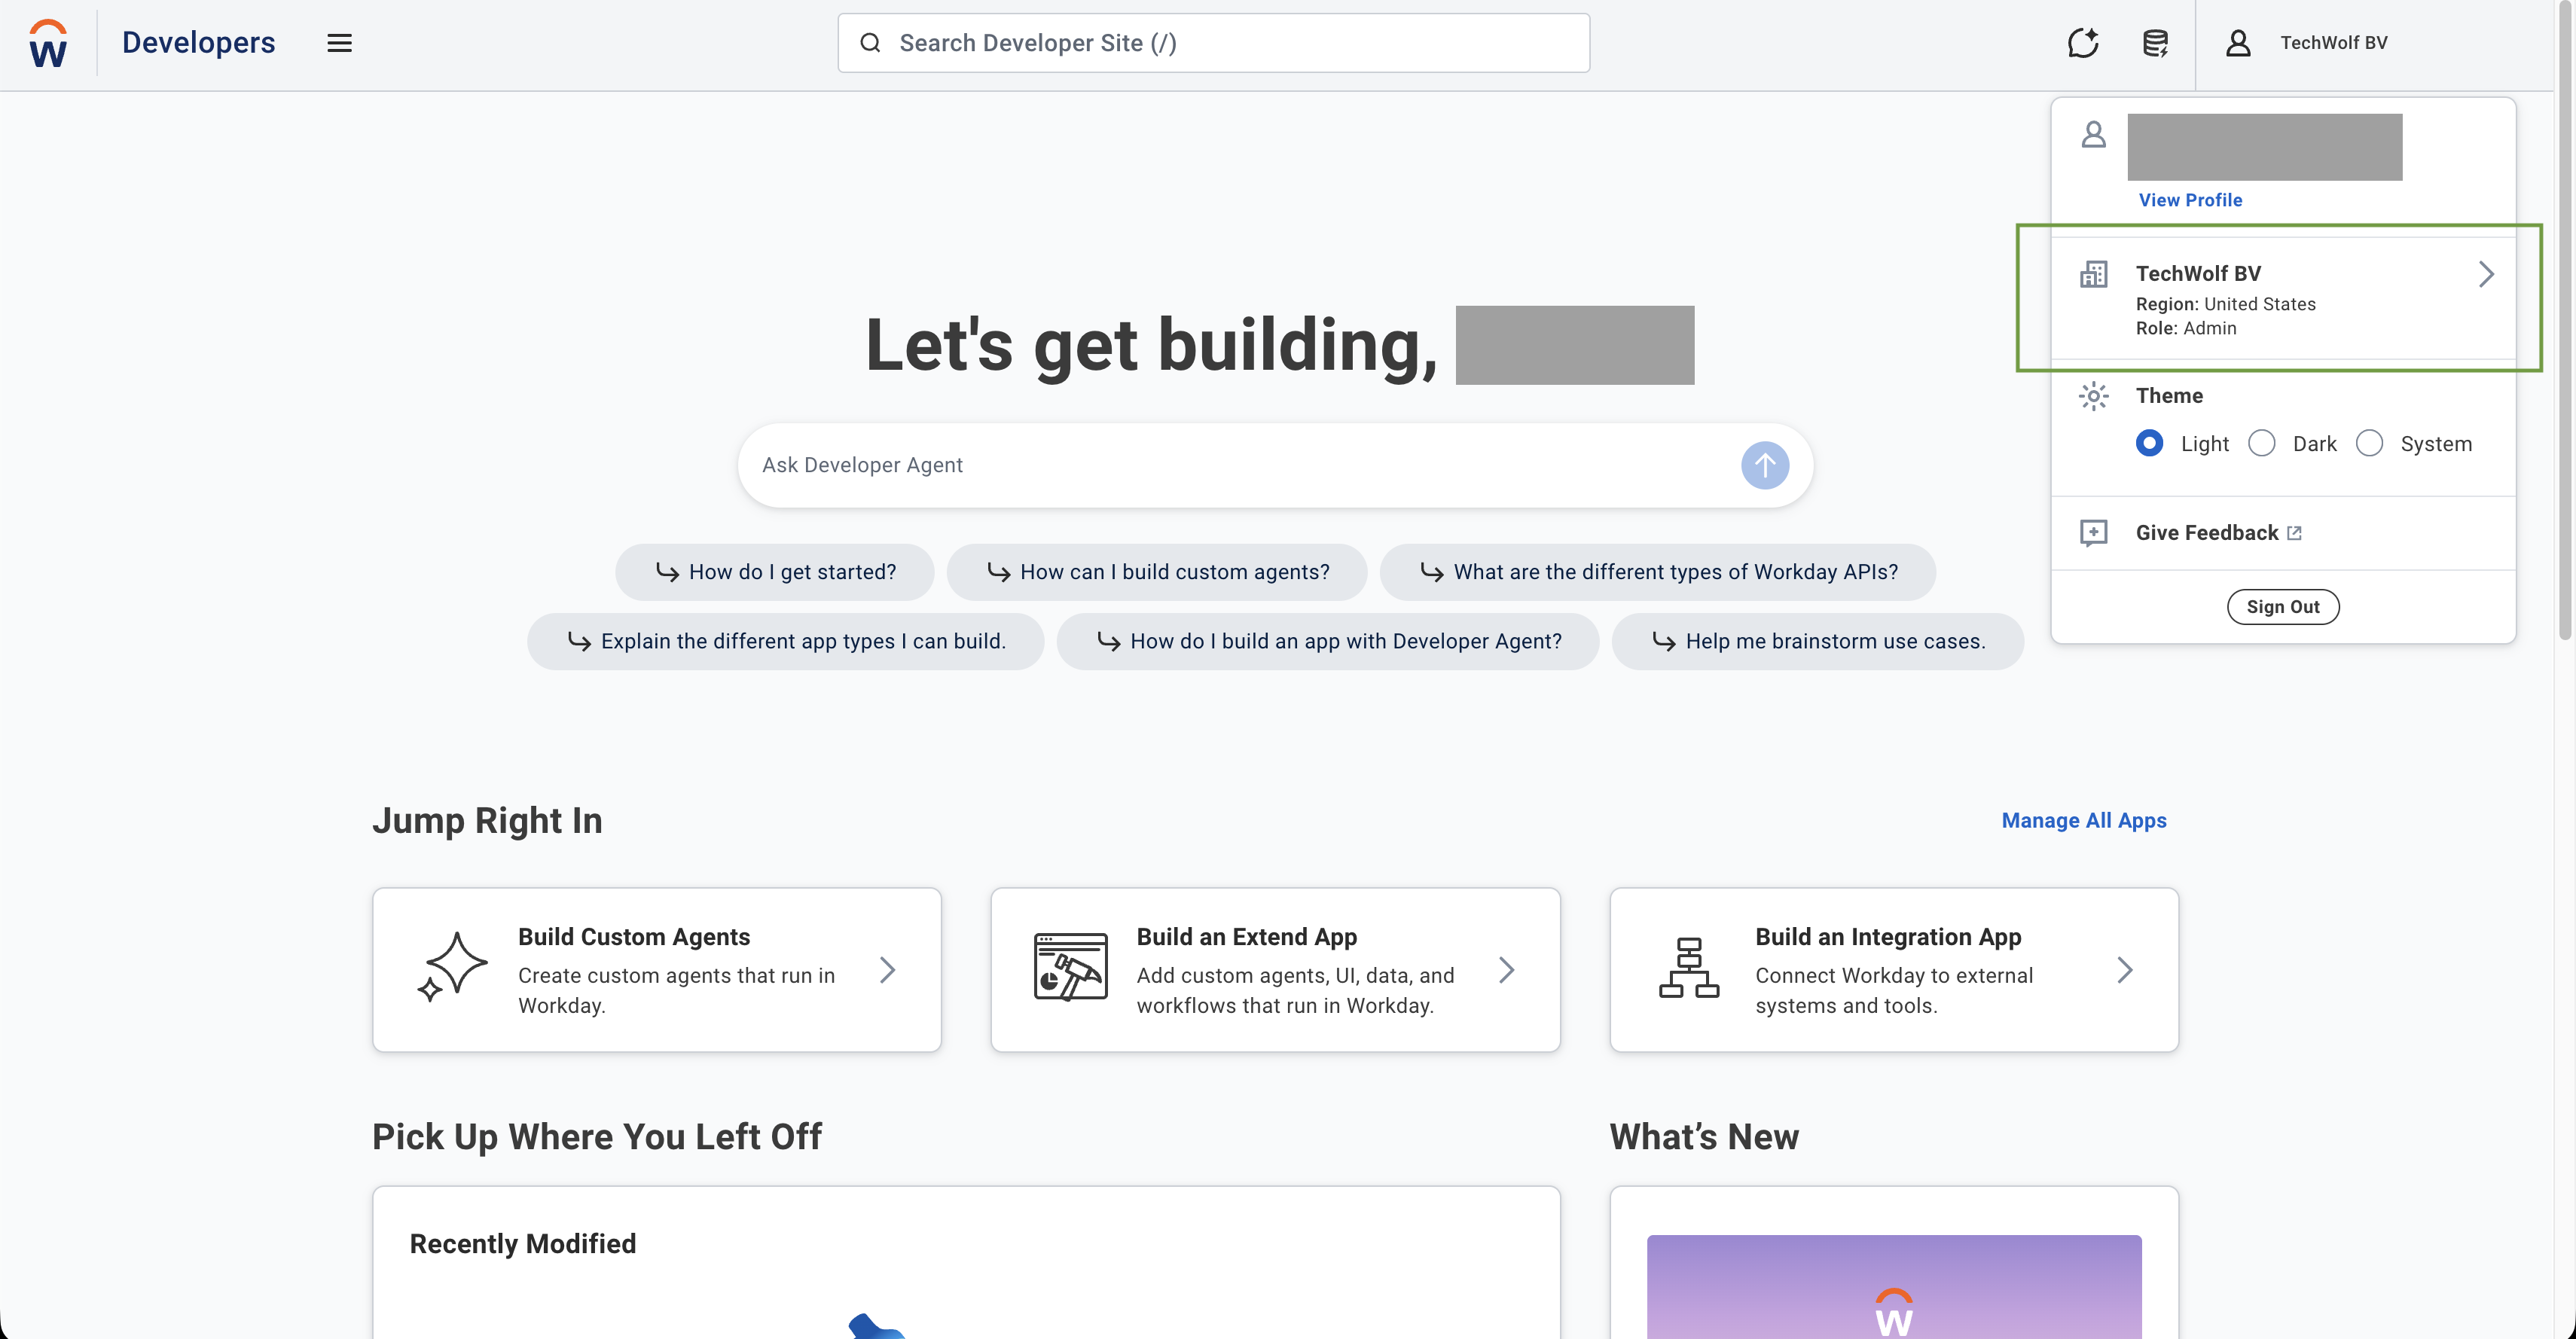
6
Map the API client to the ISU
In the Workday tenant, run the 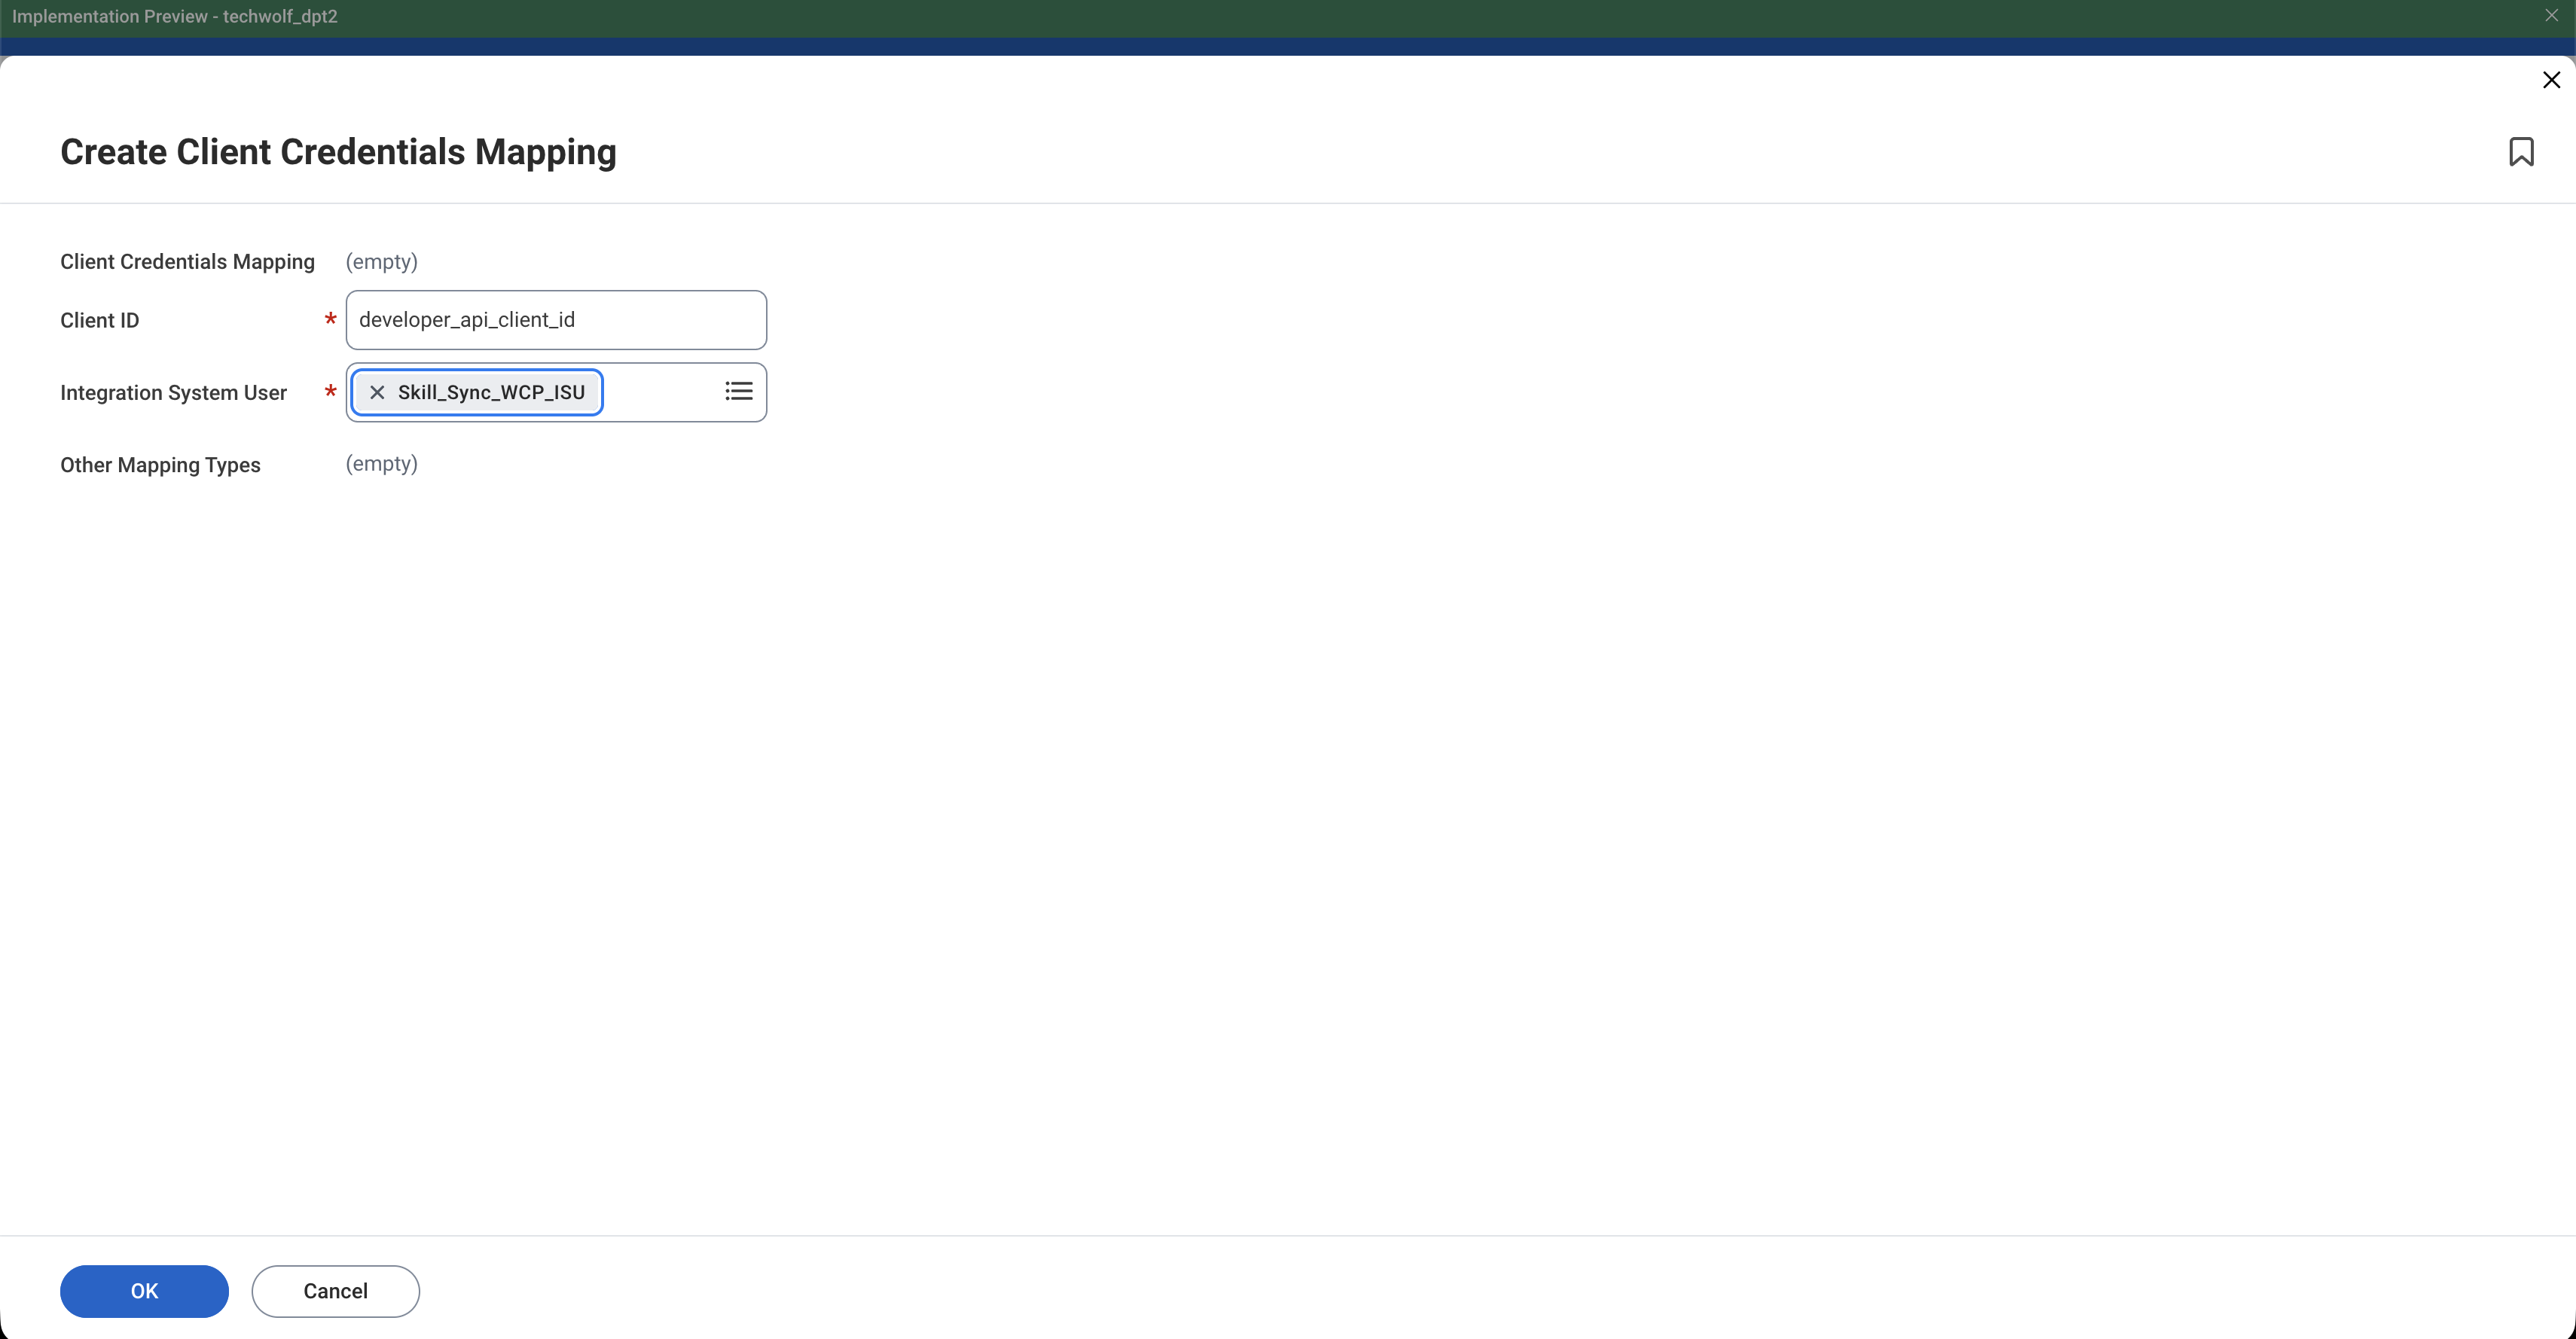
Create Client Credentials Mapping task:- Client ID: the ID of the API client you created on the Developer Site. Using WCP does not require an API client in the tenant itself.
- Integration System User: the ISU from the General setup.
View Client Credentials Mapping to see what was saved. See
Authenticate Using the Client Credentials Grant Type.Basic Authentication setup
1
Find out the correct Workday API URL
-
Search for
Public Web Servicesin the search bar at the top of the Workday home page. -
In the list, click the three dots next to the
Human Resources (public)entry. SelectView WSDLunderWeb Service. -
The resulting page will take some time to load. Once it is loaded, look for
“soapbind:address location” near the bottom of the page. You will see a
section like this:
- Copy the base tenant URL up to and including your tenant name. The service name and version should be excluded from the URL.
- Note that the API URL can differ between implementation tenants and production tenants, so the steps described above need to be repeated for each tenant individually.
TechWolf Configuration
The TechWolf tenant will be configured by TechWolf itself.-
In the integration service on the TechWolf side, TechWolf adds the
credentials of the customer-created ISU. For this, the customer will need to
share the following values with TechWolf:
- The Workday API URL (see step 1 of the Direct Tenant Communication or Basic Authentication setup), except on the WCP gateway
- Authentication credentials:
- OAuth through Direct Tenant Communication: client ID, client secret, and refresh token (see steps 2–3 of the Direct Tenant Communication setup)
- OAuth through the WCP gateway: client ID, client secret, tenant alias and region (see the WCP gateway setup)
- Basic Authentication (on request): ISU username and password (see steps 1–2 of the General setup)
- TechWolf adds TechWolf API credentials with correct scopes to have access to the TechWolf API and links that TechWolf tenant to the Workday tenant.
- TechWolf validates that the ISU has the required permissions and that the Workday API URL is correct.
- TechWolf runs an initial sync of Job profiles with the TechWolf API and sets up the tenant configuration to start the bidirectional sync process.
Routing Through an API Gateway
If your organisation fronts the Workday APIs with an API gateway, the integration can call the gateway instead of the vendor host directly. Two settings are available, both configured by TechWolf together with the credentials:- Custom URL: instead of the vendor API URL, share the gateway URL that proxies it. The integration keeps appending the same vendor API paths to it, so the gateway must forward requests to Workday unchanged.
- Custom headers: any number of extra HTTP headers (for example an API key or a correlation ID required by the gateway) that are sent on every request the integration makes.
Both settings are pass-through only. TechWolf sends the values as configured
and does not perform any gateway-specific authentication, signing, or token
refresh; the gateway is expected to forward the integration’s own
credentials to Workday. Reserved headers (e.g.
Authorization,
Content-Type) are managed by the integration and cannot be set as custom
headers.Linking Workday & TechWolf - Seamless Matching of Job IDs
A critical aspect of this process is the seamless coupling of Job IDs across both platforms. There are two options for direct ID matching:-
Using Job Codes: If you want to use Workday Job Codes (also known as Job
Profile IDs) as the identifier field in Workday, then this same ID must also
be used as the Job
external_idin TechWolf. -
Using Workday IDs (WIDs): If you want to use Workday IDs as the
identifier field in Workday, then this same ID must also be used as the Job
external_idin TechWolf. This option is only available if you have a generator configured in Workday for Job Codes. For details on how to set this up, please refer to the Workday documentation, e.g. Create ID Definitions and Sequence Generators.
Deployment Methodology
The following tasks and responsibilities assume that:- The customer has the appropriate TechWolf API license(s).
- The TechWolf API contains all Job information corresponding to Workday Jobs and data from other external systems.
Deployment Tasks & Responsibilities
- TechWolf: Setup Skill Sync environment and tenant requirements
- Customer: Verify the Synonym Management configuration (see System Requirements).
- Customer: Create Integration System User (ISU) based on workflow described above.
- Customer: Share the connection details with TechWolf:
- OAuth through Direct Tenant Communication: Workday API URL, client ID, client secret, and refresh token
- OAuth through the WCP gateway: client ID, client secret, tenant alias and region
- Basic Authentication (on request): Workday API URL, ISU username and password
- TechWolf: Run initial sync of Job profiles with TechWolf API.
- TechWolf: Setup tenant configuration and start bidirectional sync process.
- Customer: Check end-user test scenarios.